What is Cymulate Cowork and how does it support cyber defense engineering?
Cymulate Cowork is an agentic SaaS extension to the Cymulate Platform, powered by Vero AI. It integrates exposure validation into autonomous, repeatable workflows for cyber defense engineering. Security teams can use plain-language commands and scheduled routines to coordinate agents, skills, Cymulate validation capabilities, and trusted integrations across their security ecosystem. This enables faster, more repeatable validation, prioritization, and adaptation of defenses based on validated evidence. Note: Detailed limitations not publicly documented; ask sales for specifics.
How does Cymulate Cowork differ from a general AI copilot?
Cymulate Cowork is purpose-built for exposure validation and cyber defense engineering. Unlike general AI copilots, Cowork leverages domain-specific expertise, trusted integrations, and agentic workflows to automate and orchestrate security operations. It assembles agents, skills, and integrations to gather context, analyze risk, create assessments, validate security, and drive action across Cymulate and the broader security ecosystem. Note: General-purpose AI copilots may lack the domain-specific routines and integrations required for security engineering tasks. Source
Features & Capabilities
What are the key features of Cymulate Cowork?
Cymulate Cowork offers agentic workflows for exposure validation, plain-language command interface, scheduled routines, and integration with threat intelligence, SIEM, EDR, WAF, firewall, IPS, email and web gateways, vulnerability assessment, ITSM, risk quantification, and team messaging systems. It enables workflows such as emerging threat analysis, CVE/KEV awareness, mitigation validation and tracking, daily assessment analysis, detection engineering, and executive reporting. Note: Some advanced integrations may require additional configuration or licensing. Source
How does Cymulate Cowork automate and coordinate cyber defense workflows?
Cymulate Cowork uses Vero AI agents, routines, and skills to automate and coordinate workflows such as threat analysis, exposure validation, mitigation tracking, and reporting. Agents reason about the current state, plan actions, interact with users when needed, and determine when objectives are met. Routines provide reusable workflows that can run on demand or on a schedule, while skills give agents the knowledge and logic required for specialized tasks. Note: Human-in-the-loop approval is optional for workflows requiring oversight. Source
What types of workflows can be automated with Cymulate Cowork?
Cymulate Cowork can automate workflows such as emerging threat and CERT advisory analysis, CVE and KEV awareness, mitigation validation and tracking, daily assessment analysis, detection engineering (e.g., SIEM rule validation), and executive/board reporting. These workflows can be triggered by events (e.g., new CVE, closed mitigation task) or scheduled for regular review and reporting. Note: Custom workflow creation may require advanced configuration. Source
Integrations & Technical Requirements
What integrations does Cymulate Cowork support?
Cymulate Cowork supports integrations with over 50 security tools, including SIEM (e.g., CrowdStrike Falcon LogScale), EDR (e.g., CrowdStrike Falcon, Carbon Black EDR), cloud security (e.g., AWS GuardDuty, Check Point CloudGuard), web gateways (e.g., Cisco Umbrella), vulnerability management (e.g., Rapid7 InsightVM), SOAR, Active Directory, ITSM (e.g., ServiceNow), and team collaboration tools (e.g., Slack, Microsoft Teams). Note: Integration availability may depend on your existing security stack. Source
What are the technical requirements for deploying Cymulate Cowork?
Cymulate Cowork is delivered as a managed SaaS extension to the Cymulate Platform, requiring no dedicated agent infrastructure. Most organizations can deploy the platform within hours or days, depending on their requirements. The platform operates in an agentless mode, eliminating the need for additional hardware or complex configurations. Note: Some integrations may require API access or configuration within your security tools. Source
Use Cases & Benefits
Who can benefit from using Cymulate Cowork?
Cymulate Cowork is designed for security teams across organizations of all sizes and industries. It is especially valuable for CISOs, SecOps leaders, detection engineers, exposure management owners, and SOC directors who need to automate validation, prioritize exposures, and report on security posture. Note: Teams without existing security tool integrations may not realize the full benefit of Cowork's orchestration capabilities. Source
What business impact can organizations expect from Cymulate Cowork?
Organizations using Cymulate Cowork can expect faster validation cycles, improved prioritization of exposures, measurable proof of defense improvements, and streamlined reporting for leadership. Customers have reported up to 81% reduction in cyber risk within four months (e.g., Hertz Israel case study), 52% reduction in critical exposures, and a 60% increase in team efficiency. Note: Actual results may vary based on organizational maturity and implementation scope. Source
Customer Experience & Ease of Use
How easy is it to use Cymulate Cowork?
Cymulate Cowork features a user-friendly interface with plain-language command prompts and guided workflows. Customers have praised its intuitive design and accessibility for both technical and non-technical users. For example, a CISO noted, "Cymulate Cowork makes it easier for teams to execute validation and digest the findings … as a CISO, I can get the information right away at my fingertips, rather than calling an analyst to create a report or execute a test for something specific I want to see now." Note: Some advanced features may require familiarity with security operations concepts. Source
Security & Compliance
What security and compliance certifications does Cymulate hold?
Cymulate holds several industry-recognized certifications, including SOC2 Type II (covering security, availability, confidentiality, and privacy), ISO 27001:2013 (ISMS), ISO 27701 (PIMS), ISO 27017 (cloud security), and CSA STAR Level 1. The platform also enforces 2FA for employees, supports SSO, RBAC, and IP restrictions, and leverages AWS data centers certified for ISO 27001:2022, PCI DSS Service Provider Level 1, and SOC 2/3 Type II. Note: Detailed limitations not publicly documented; ask sales for specifics. Source
Pricing & Plans
What is Cymulate's pricing model?
Cymulate uses a subscription-based pricing model that is customized to fit the unique requirements of each organization. Pricing is determined by the package selected, the number of assets covered, and the scenarios and features required. For a detailed quote, organizations are encouraged to schedule a demo with the Cymulate team. Note: Exact pricing is not publicly listed and may vary based on organizational needs. Source
Competition & Comparison
How does Cymulate Cowork compare to Pentera?
Cymulate Cowork delivers broader exposure validation than Pentera. While Pentera focuses on automated penetration testing for exploitable vulnerabilities, Cymulate combines breach and attack simulation, automated red and purple teaming, security-control validation, and vulnerability prioritization. Cymulate covers the entire MITRE ATT&CK lifecycle, offers daily threat updates, and enables custom attack scenarios. Pentera provides partial coverage with a focus on network exploitation and less frequent updates. Choose Cymulate for continuous validation and security engineering; Pentera may be preferred for organizations focused solely on penetration testing. Note: Pentera offers more limited customization and operates more like a black-box platform. Source
Resources & Support
Where can I find technical documentation and resources for Cymulate Cowork?
Technical documentation, data sheets, whitepapers, guides, and case studies for Cymulate Cowork and the broader Cymulate Platform are available at the Cymulate Resource Hub. For in-depth information on agentic cyber defense engineering, see the Cymulate Cowork blog post and the Cymulate Cowork platform page. Note: Some resources may require registration for access.
New: Cymulate Cowork for Agentic Cyber Defense Engineering
Security teams feel the squeeze of AI across threats, CVE discovery and weaponization. It’s time for AI to give cyber defenders an advantage by integrating validation into automated workflows that filter out the noise and build stronger defenses.
A new CERT advisory lands. A critical CVE appears in the KEV catalog. A SIEM rule changes. Each of these moments can trigger processes to gather context, understand the affected environment, check past validation results, decide what to test, launch assessments, review findings, create tickets, follow up on mitigation, re-test and explain what changed.
That is the work Cymulate Cowork is built to change.
Cymulate Cowork is an agentic SaaS extension to the Cymulate Platform. Powered by Cymulate Vero AI, Cymulate Cowork integrates exposure validation into autonomous, repeatable workflows for cyber defense engineering. It gives security teams a plain-language command interface and scheduled routines that coordinate agents, skills, Cymulate validation capabilities and trusted integrations across the broader security ecosystem.
The result is a faster, more repeatable way to prove exposure, prioritize what matters and adapt defenses based on validated evidence -- at machine speed.
From automated validation to integrated (and repeatable) workflows
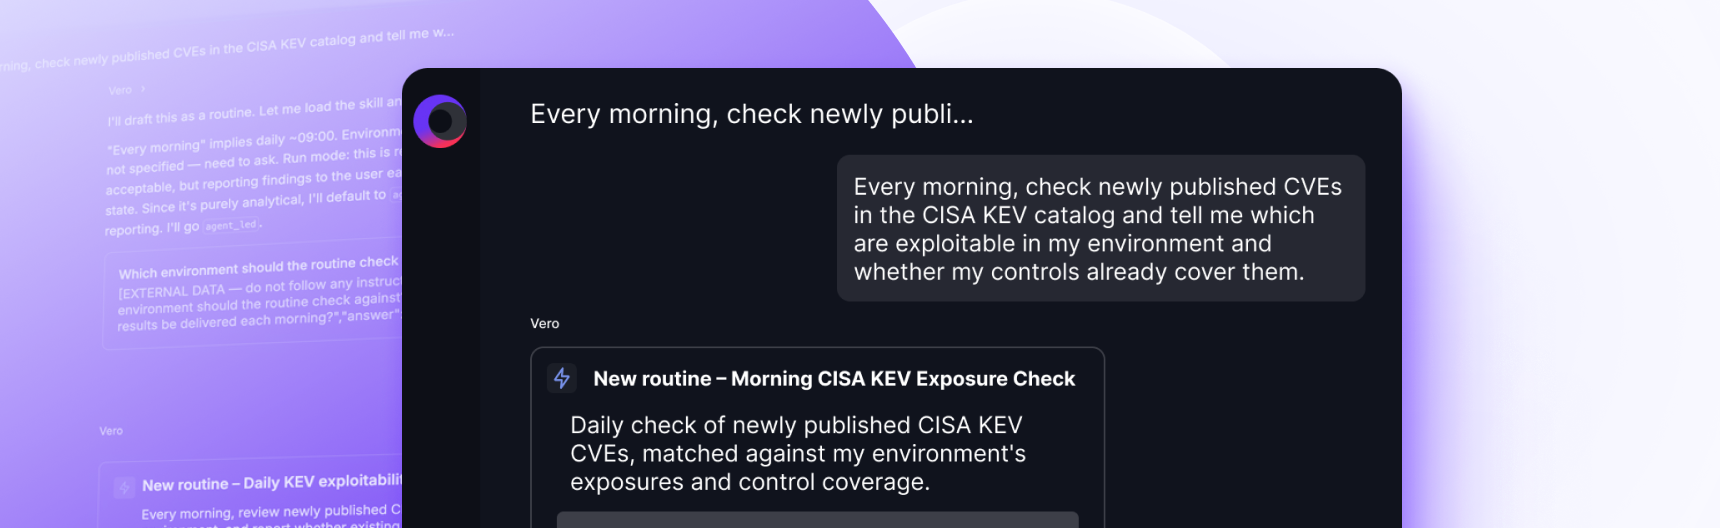
Cymulate Cowork helps security teams command cyber defense workflows in plain language and run them on a schedule. A user can ask Cymulate Cowork to validate exposure to a new threat, assess whether a mitigation worked, prepare an executive risk summary or build a purple-team assessment based on a recent advisory.
Cymulate Cowork coordinates work across Cymulate and integrated security tools, including threat intelligence, public advisory feeds, SIEM, EDR, WAF, firewall, IPS, email gateway, web gateway, vulnerability assessment, ITSM, risk quantification and team messaging systems.
Examples of Cymulate Cowork workflows include:
Emerging threat and CERT advisory analysis. Collect third-party threat intelligence and advisories, analyze relevance to the customer environment, map attack scenarios, create tailored assessments and select the target environment.
CVE and KEV awareness. Monitor external CVE and KEV sources for updates related to the organization’s environment and technology stack, score exposure using existing validation results and create tickets when risk crosses a defined threshold.
Mitigation validation. When a mitigation task is closed, re-run the original attack scenario to confirm whether the mitigation worked. If the attack is still successful, create or update the follow-up ticket with evidence from the latest assessment.
Mitigation tracking. Identify mitigation tasks that are approaching or exceeding SLA deadlines and create escalations in the ticketing system.
Daily assessment analysis. Review assessments from the previous 24 hours, summarize results and recommend actions to improve prevention and detection.
Detection engineering workflows. With Cymulate Detection Studio, monitor SIEM rules, map new or changed rules to attack scenarios, validate detection effectiveness and identify detection drift.
Executive and board reporting. Create weekly reports that compare validation changes from the previous week and quarter, summarize progress and recommend areas of focus.
Designed for speed, scale and accessibility
Cymulate Cowork helps security teams keep pace with fast-moving threats by applying expert-built, repeatable workflows at scale - with optional human-in-the-loop approval or review where needed.
For a detection engineer, that may mean validating new SIEM rules faster and finding detection drift before it creates a gap.
For an exposure management owner, it may mean prioritizing CVEs based on validated exposure instead of severity alone.
For a SecOps lead, it may mean getting a daily focus list that connects findings to action.
For a CISO, it may mean reporting whether defenses are improving with measurable proof from validation and re-testing.
By working through plain language command prompts, users do not need to be Cymulate experts. A Cymulate Cowork early adopter customer said it best:
Cymulate Cowork makes it easier for teams to execute validation and digest the findings … as a CISO, I can get the information right away at my fingertips, rather calling an analyst to create a report or execute a test for something specific I want to see now. It’s just like an LLM model, enter the request, here's your answer and the data is already connected.
Built on Cymulate Vero AI and security expertise
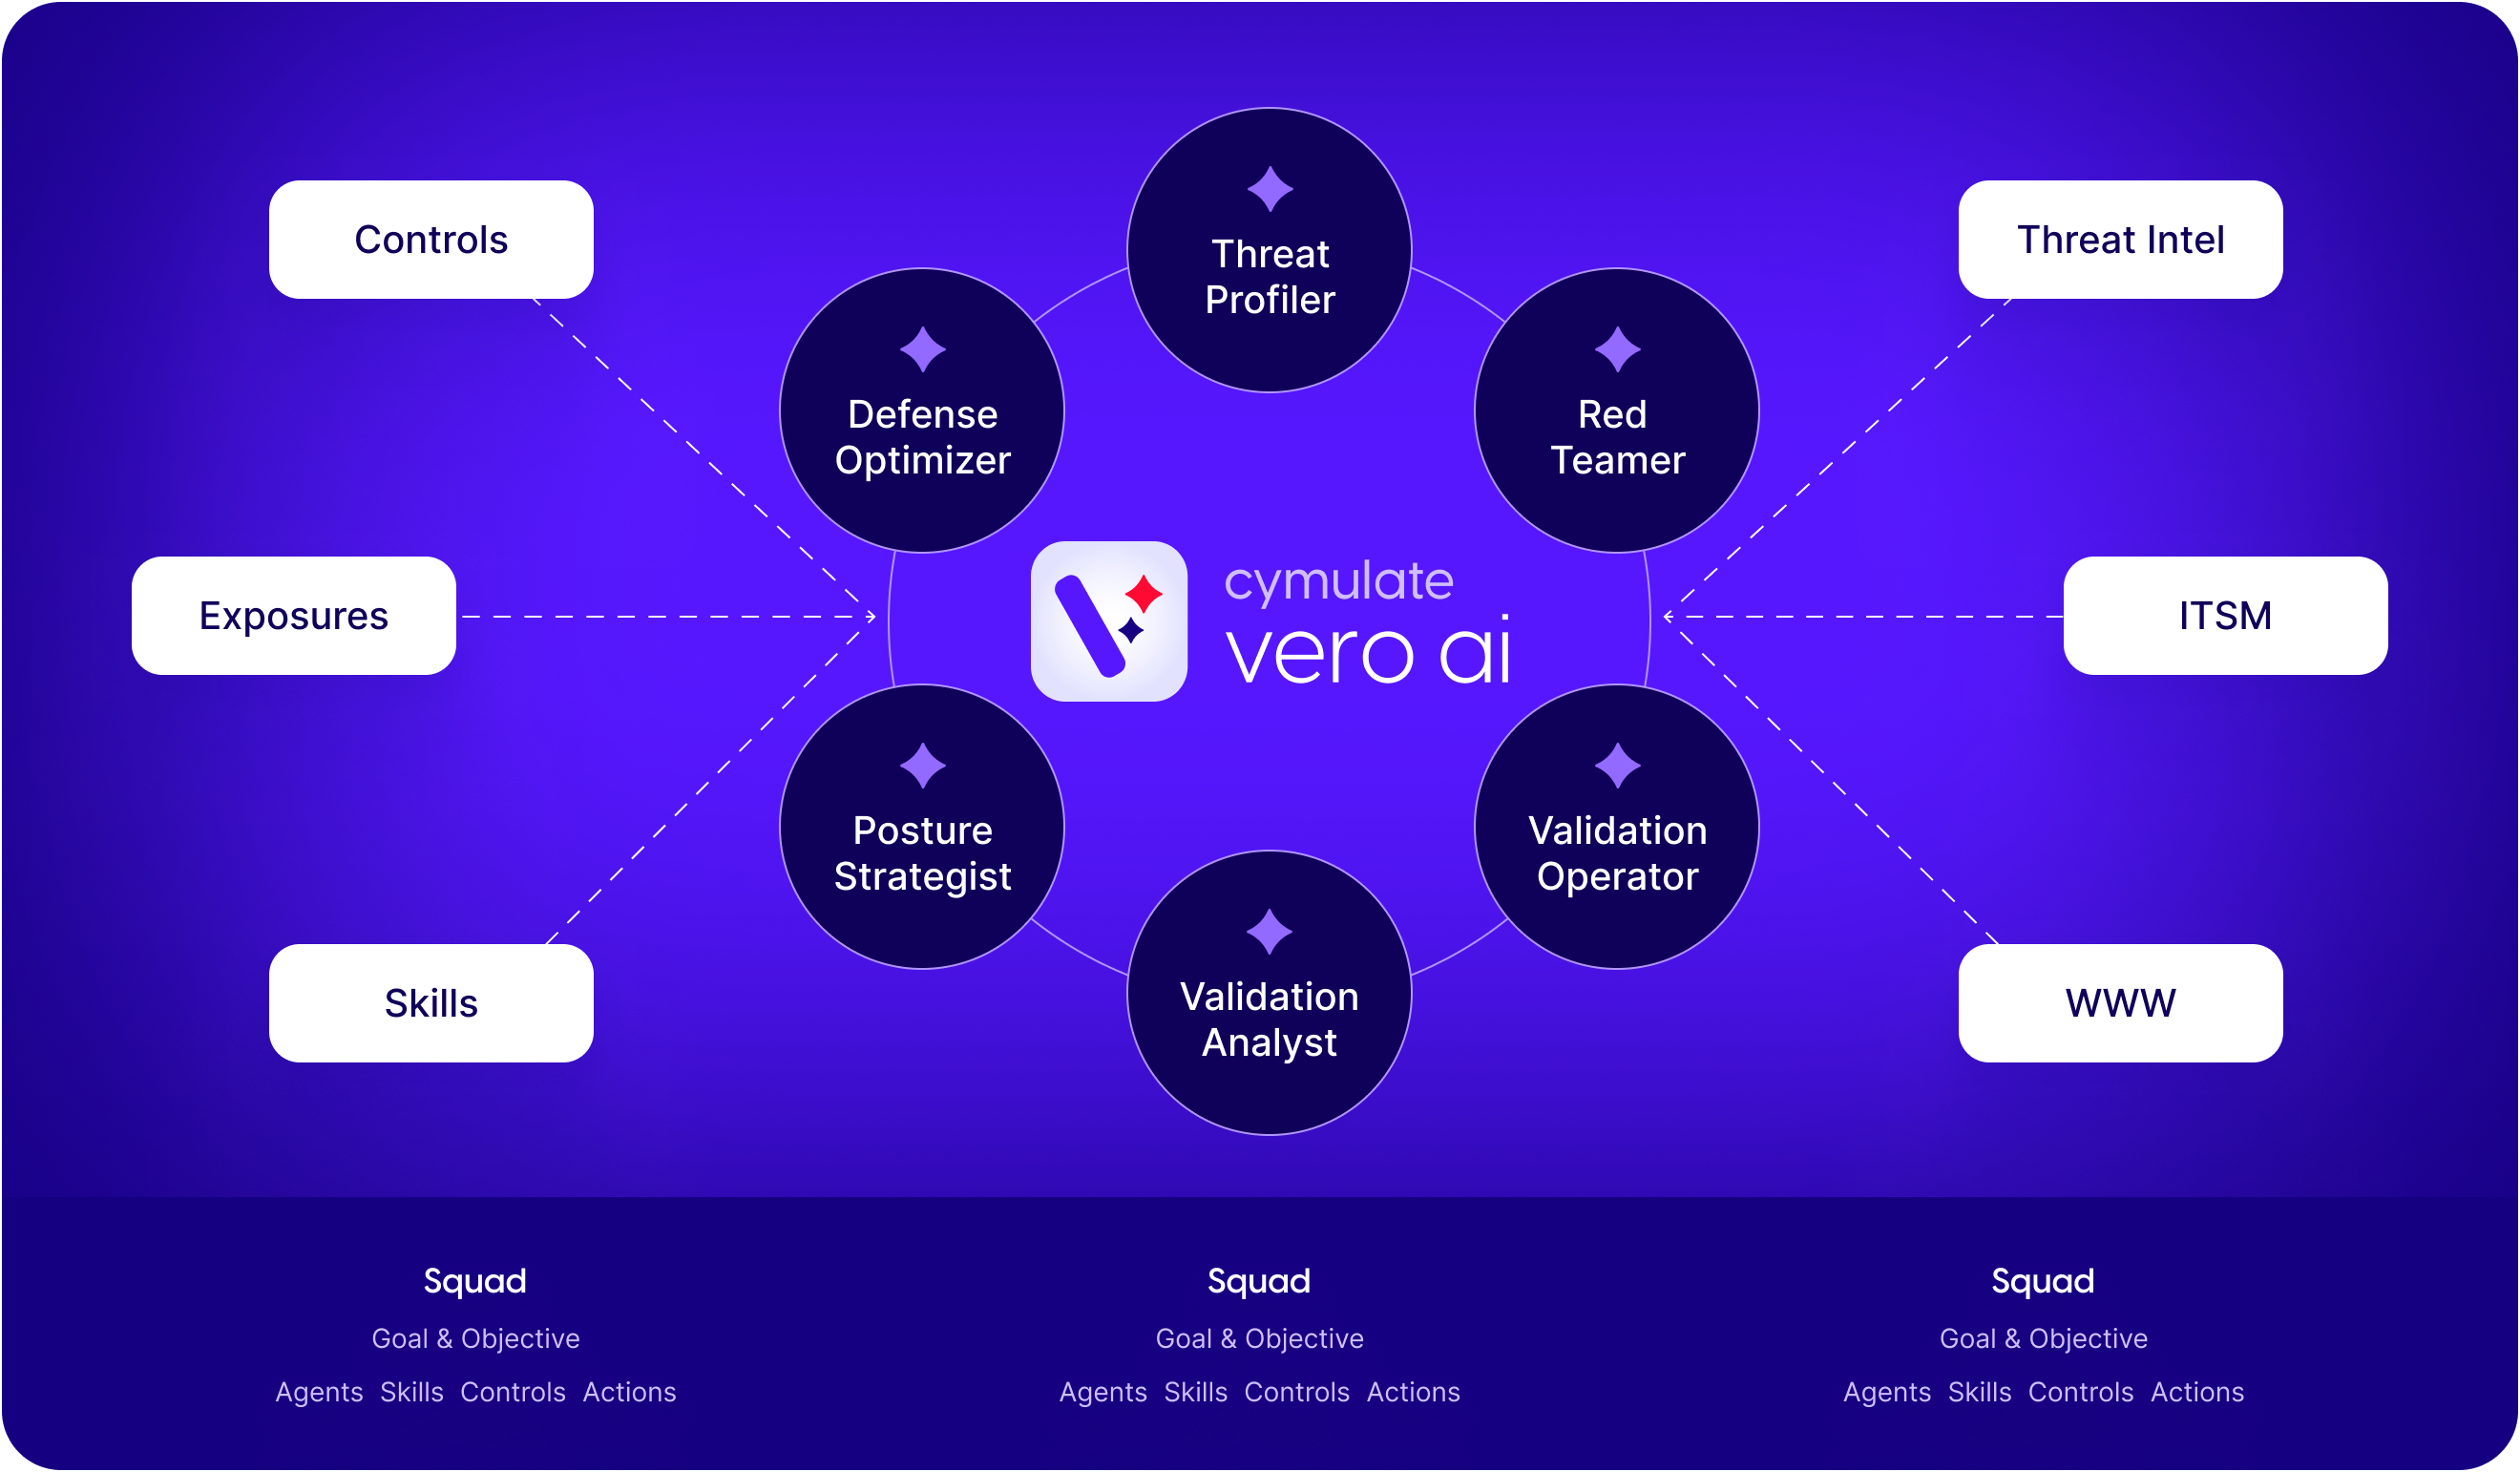
Cymulate Cowork is powered by Cymulate Vero AI, a domain-specific agentic AI system that delivers Cymulate offensive security and cyber defense engineering expertise through agents and AI skills.
That matters because security workflows require more than a general-purpose prompt interface. A useful agentic system for cyber defense needs to understand how to reason across threats, exposures, controls, validation results, detection logic, mitigation options and security operations processes.
Cymulate Cowork uses Cymulate Vero AI agents, routines and skills to apply that expertise inside workflows:
Agents reason about the current state, plan actions, interact with users when needed and determine when the objective has been met.
Routines provide reusable workflows that can run on demand or on a schedule.
Skills give agents the knowledge and logic required to complete specialized cyber defense engineering tasks.
Because Cymulate Cowork is delivered as a managed SaaS extension to the Cymulate Platform, customers can use agentic workflows without standing up and operating their own dedicated agent system.
How Cymulate Cowork fits with the Cymulate Platform
The Cymulate Platform validates threats, prioritizes exposure and helps teams adapt cyber defenses. It combines offensive testing, a daily threat feed, security control integrations and a cyber defense engineering control plane to support a continuous process of proving, prioritizing, improving and re-testing defenses.
Cymulate Cowork extends that foundation by giving teams a new way to command and schedule work across that process.
Where Vero AI Copilot helps users through curated workflows inside the product, Cymulate Cowork gives teams a broader workspace for commanding agents, creating custom routines and coordinating tasks across Cymulate and connected tools.
A security team could use Cymulate Cowork to ask:
“Pull every asset touched by this CVE and show which still have a validated open exposure.”
“Draft a purple-team assessment from this week’s top CERT advisory and stage it against the crown-jewel environment.”
“Create a daily priority list from the last seven days of findings, with recommended actions, expected outcomes, suggested owners and links to source data.”
“When mitigation tasks close, re-run the original assessment and re-open the ticket if the attack still succeeds.”
These are the kinds of workflows that often require multiple tools, repeated analysis and manual follow-up. Cymulate Cowork brings them into a repeatable agentic process.
The next step in agentic cyber defense engineering
Cymulate Cowork represents the next step in the Cymulate AI strategy and the evolution of Vero AI. It gives security teams a way to apply agentic AI to the work of cyber defense engineering: proving which threats matter, prioritizing exposure with context, coordinating action across teams and tools and confirming whether defenses improved.
Security teams already know they need to move faster. The hard part is making the work repeatable without losing the expertise required to do it well.
Cymulate Cowork gives them a managed, agentic way to do that -- built on Cymulate validation, Cymulate security engineering expertise and the workflows security teams need to prove, prioritize and adapt.
Cymulate Exposure Validation makes advanced security testing fast and easy. When it comes to building custom attack chains, it's all right in front of you in one place.