

SIEM Validation
Test and optimize your SIEM detections against the latest threats, campaigns, tactics and techniques.
Detection is your last line of defense against exposure
to a potential cyber incident.
38 of 201
Average coverage
of MITRE techniques
Source: IBM
194
Average days
to discover a breach
Source: IBM
$4.88M
Average cost
of a data breach
Source: IBM
Agentic Cyber Defense Engineering for SIEM
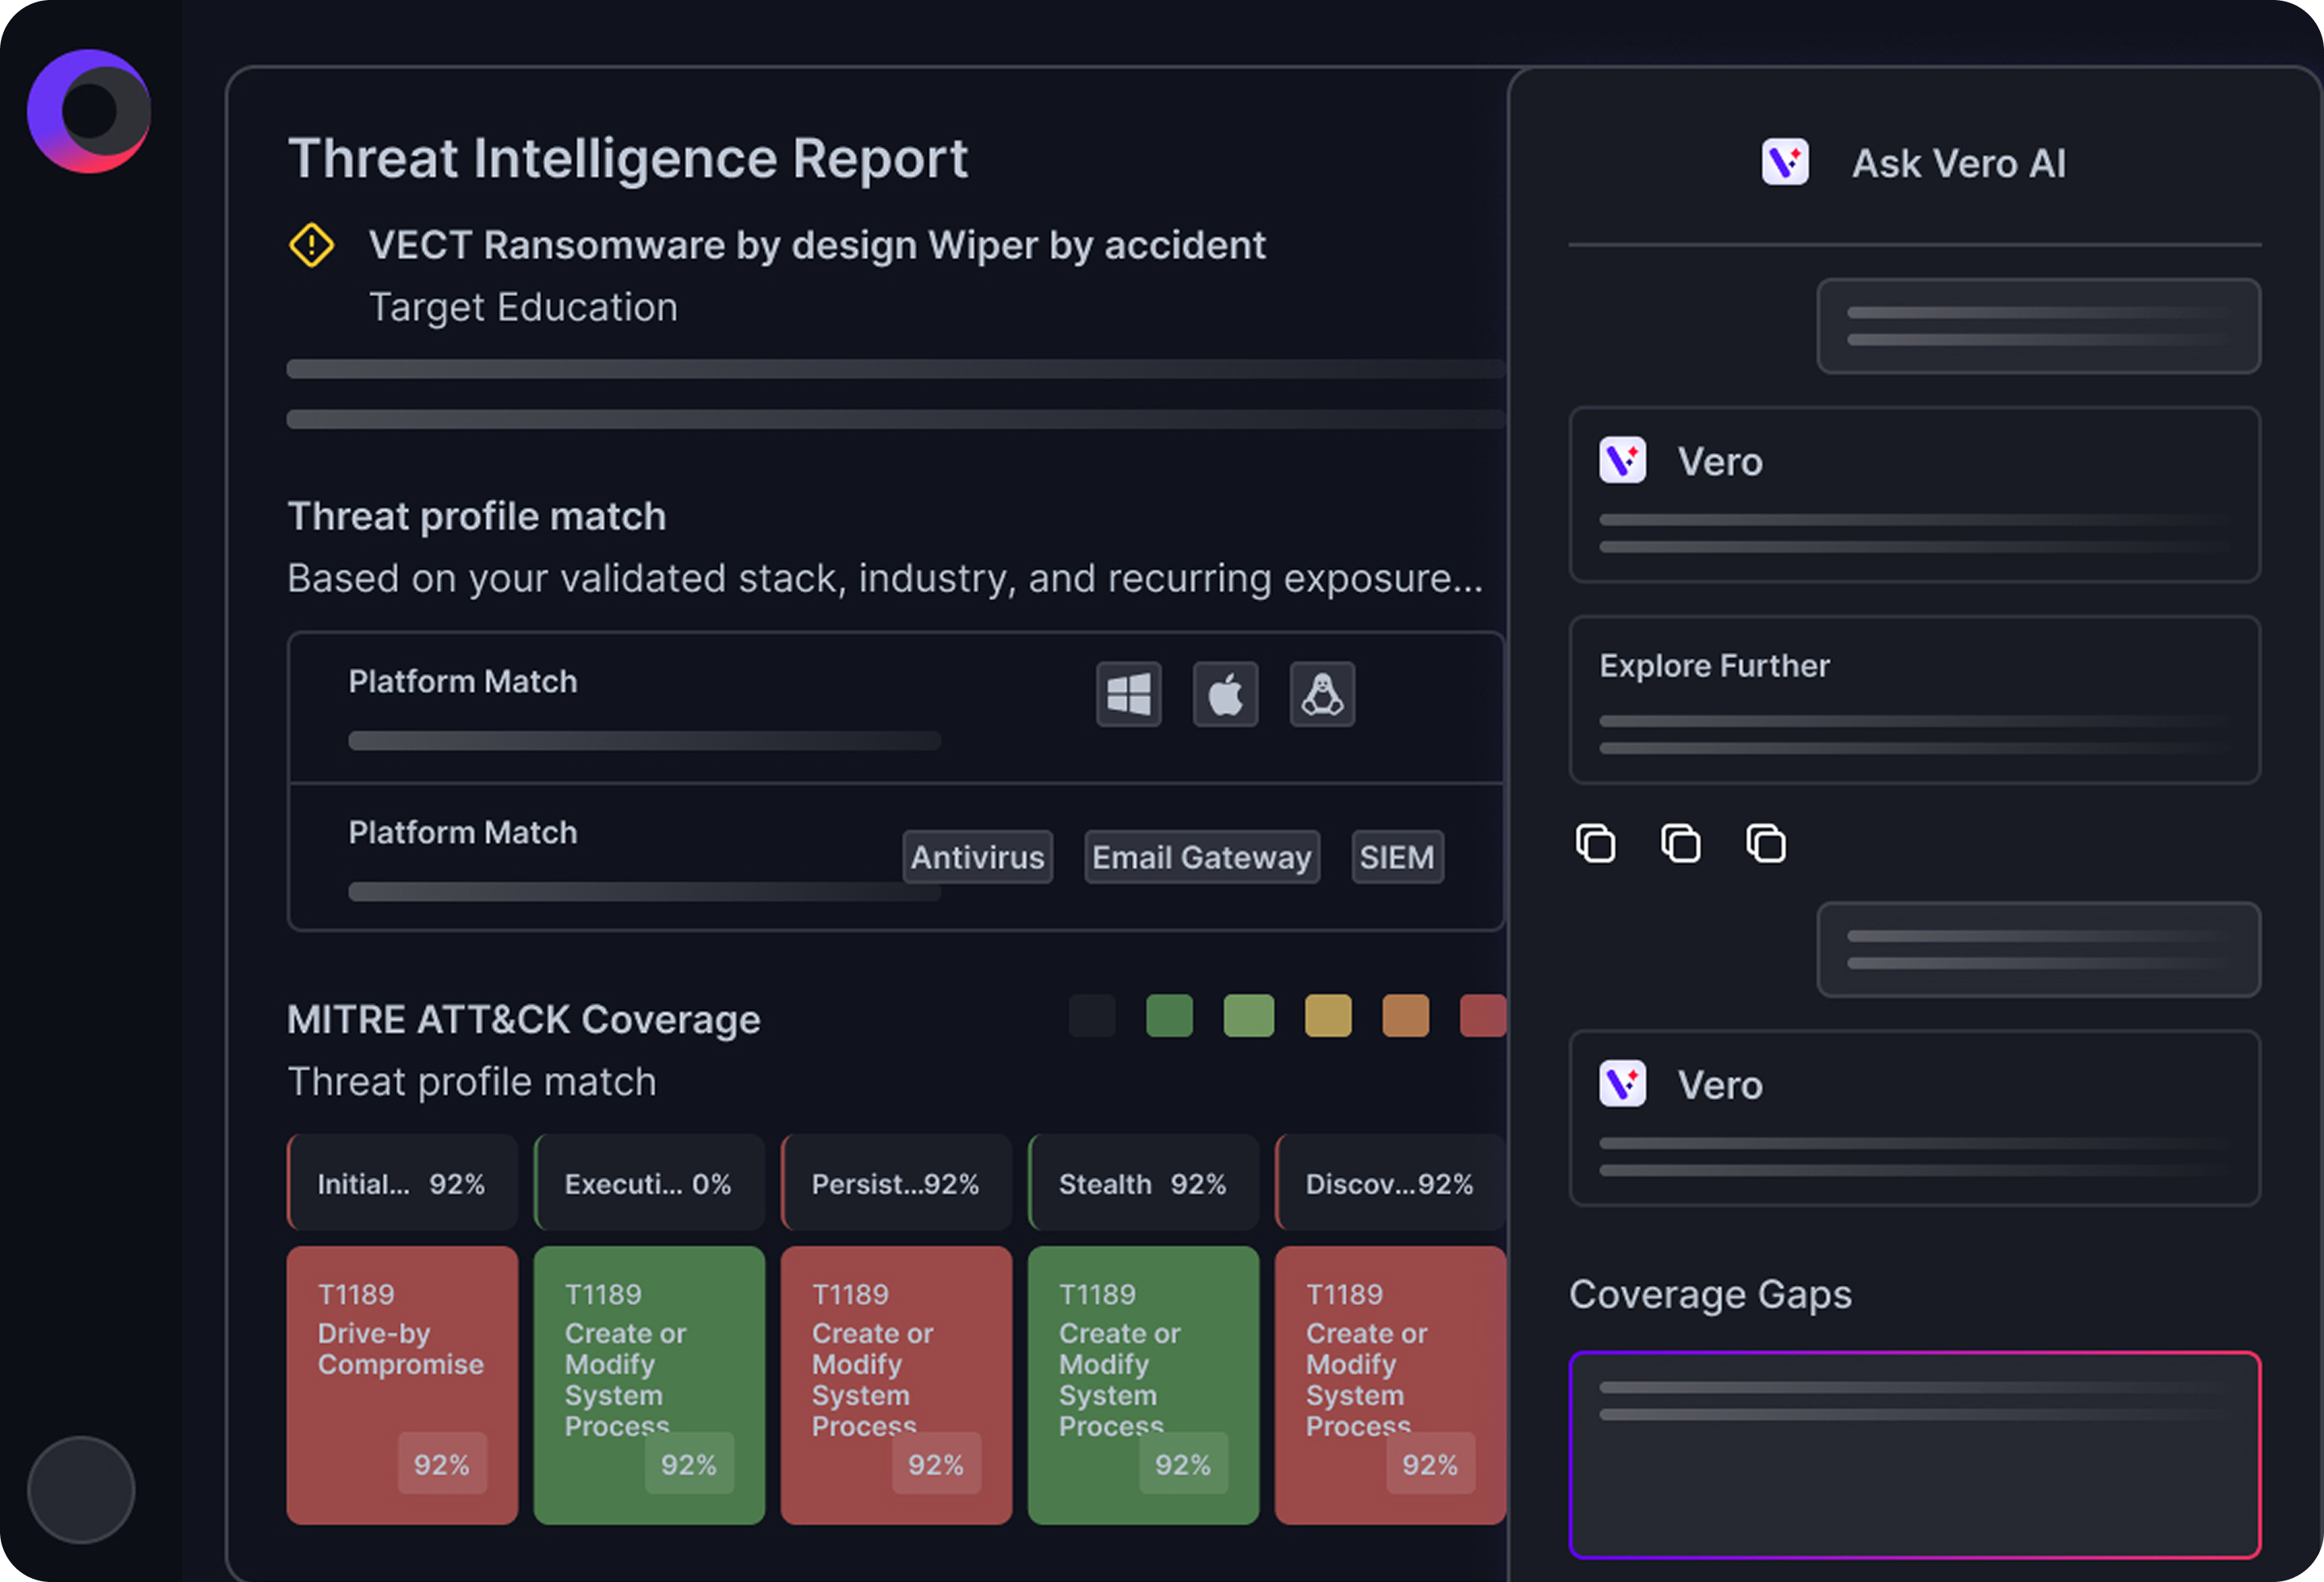
Today’s AI-powered threats move faster than detection engineering can keep up, demanding a new approach to prove, prioritize and adapt your SIEM detections at machine speed. Cymulate integrates with your Security Information and Event Management (SIEM) to go beyond validation and deliver agentic cyber defense engineering.
Powered by Vero AI, Cymulate demonstrates detection effectiveness through production-safe attack simulation, prioritizes coverage gaps with real-world impact and helps fine-tune your detections with vendor-specific rules.
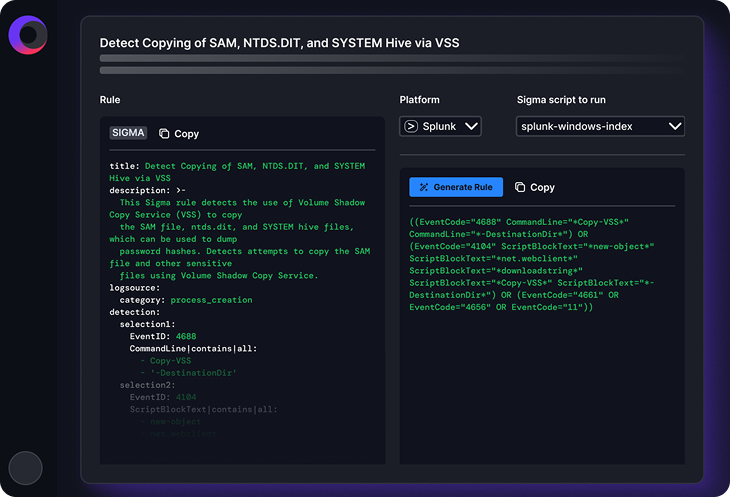
When Cymulate identifies a missed detection, a rule that never fires or a gap in log collection, it closes it by generating and tuning targeted detection rules for your SIEM. Every update is revalidated against the original attack scenario, so stronger detection is proven, not assumed.
Instead of one more list of findings, Cymulate closes the risk-to-fix gap and continuously proves, prioritizes and adapts your SIEM against the threats targeting your environment.
SIEM Validation and Optimization
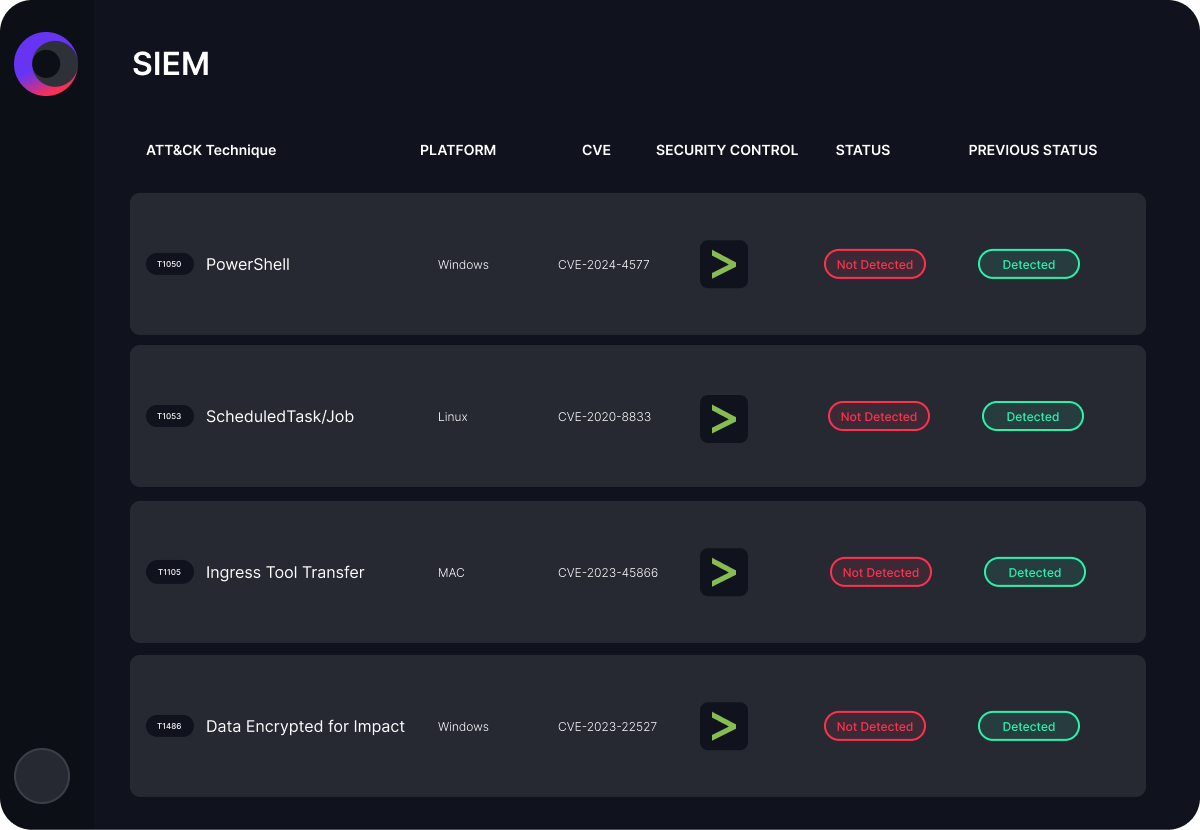
Solution Results

91%
Improvement in malicious
file detection
50%
Improvement in the prevention of known exploit techniques

168
Exploits prevented from a single recommended policy change
Solution Benefits
Reduce mean time to detect
Reduce manual SecOps effort
Prove improved detection
Continuously optimize your SIEM

Integrate with Your SIEM to Tune and Optimize Threat Detection
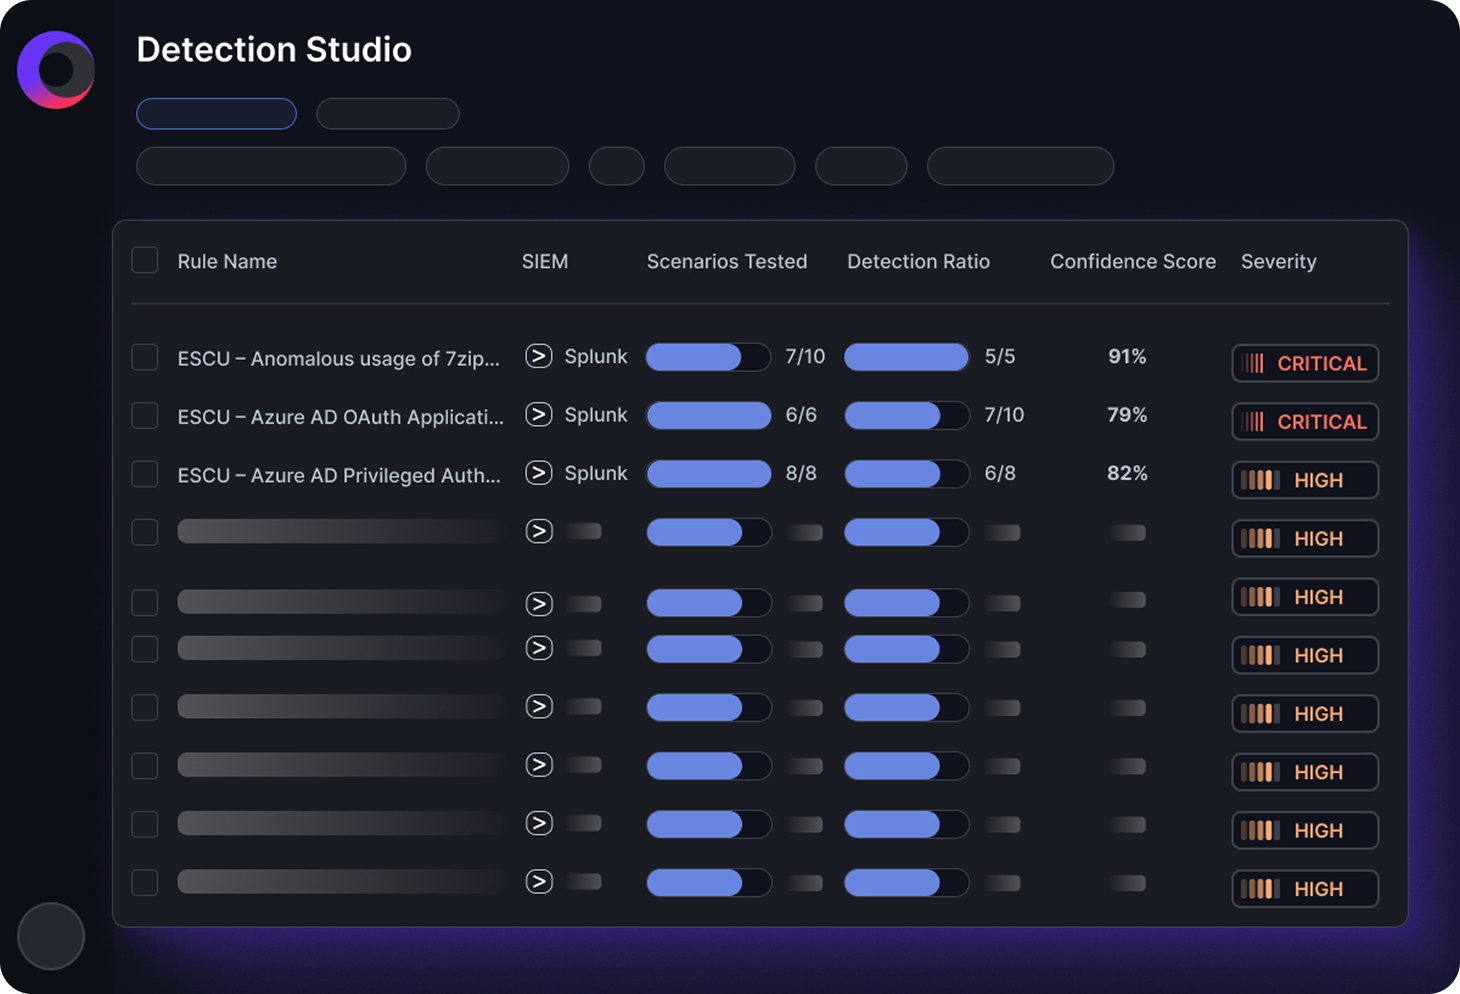
Seamless integration with SIEM platforms is essential for effective detection validation. Cymulate, powered by Vero AI, connects directly to your SIEM to automatically ingest rules and collect the required data, accelerating validation and eliminating manual workflows.
What Our Customers Say
Featured Resources
View More Resources
Detection Engineering
Automate detection engineering with AI-powered attack simulations to close gaps, cut false positives, and stop threats faster.
Cymulate Detection Studio
Cymulate Detection Studio automates SIEM rule validation and detection tuning against real-world attacks.
RBI Validates and Optimizes SIEM
Discover how RBI increased their efficiency and improved their security with Cymulate.
FAQs
SIEM validation is the practice of testing whether your SIEM actually collects the right telemetry, correlates it correctly and alerts on real attacker behavior, rather than assuming it does based on rule inventory or default content packs. Cymulate does this by running production-safe attack simulations mapped to MITRE ATT&CK against your environment and comparing what the attack did against what your SIEM logged, correlated and alerted on. The result is evidence of where your detections hold up and where they don’t.
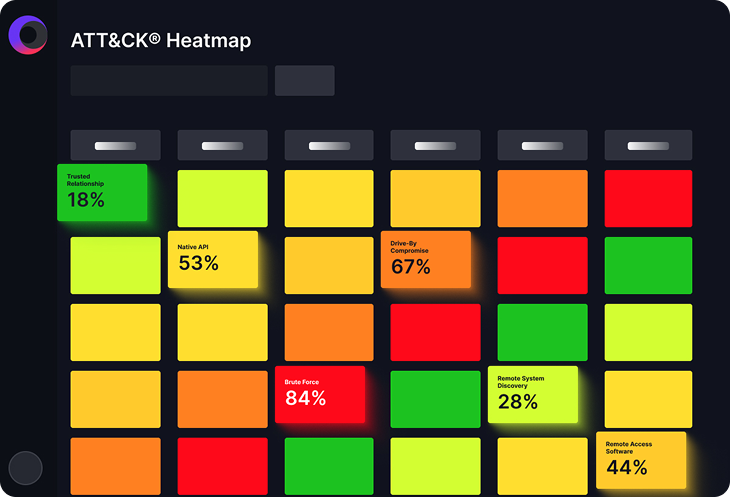
Cymulate ingests your existing SIEM rules through native integrations and uses Vero AI to map them to attack techniques and scenarios. It then executes real-world attack simulations, correlates the simulation with your SIEM’s logs and alerts, and determines whether each technique was detected, alerted on or missed entirely. Findings map directly to MITRE ATT&CK, so you see coverage gaps by technique rather than a single pass/fail score, and each finding shows the detection logic needed to close the gap.
Cymulate closes the loop between validation and detection engineering. Vero AI maps rules to the attack techniques they are meant to catch, simulation proves which ones fire, and guided tuning fixes the ones that don’t. New rules are generated for uncovered techniques and retested automatically.
Yes. Cymulate simulations are production-safe: they reproduce the techniques and behavior of real attacks without executing actual malicious payloads or causing damage to systems or data. This is what allows validation to run continuously in live environments rather than being confined to a test lab or a scheduled maintenance window.
Yes. Cymulate generates Sigma rules and vendor-specific detection rules from validated gaps and provides guided tuning for the rules you already have. Once deployed, rules are retested against the original attack scenario to confirm they improved detection.