

Email Gateway Validation
Continuously test and optimize your secure email gateway against phishing, malicious links, attachments and other email-borne threats.
Email remains the number-one attack vector and the most frequently used delivery method for cyber attacks.
94%
Organizations suffered email security incidents
Source: Egress Software
79%
Cyber attacks started with
a phishing email
Source: Egress Software
69%
Ransomware attacks
began with an email
Source: Barracuda Networks
Agentic Cyber Defense Engineering for SEG
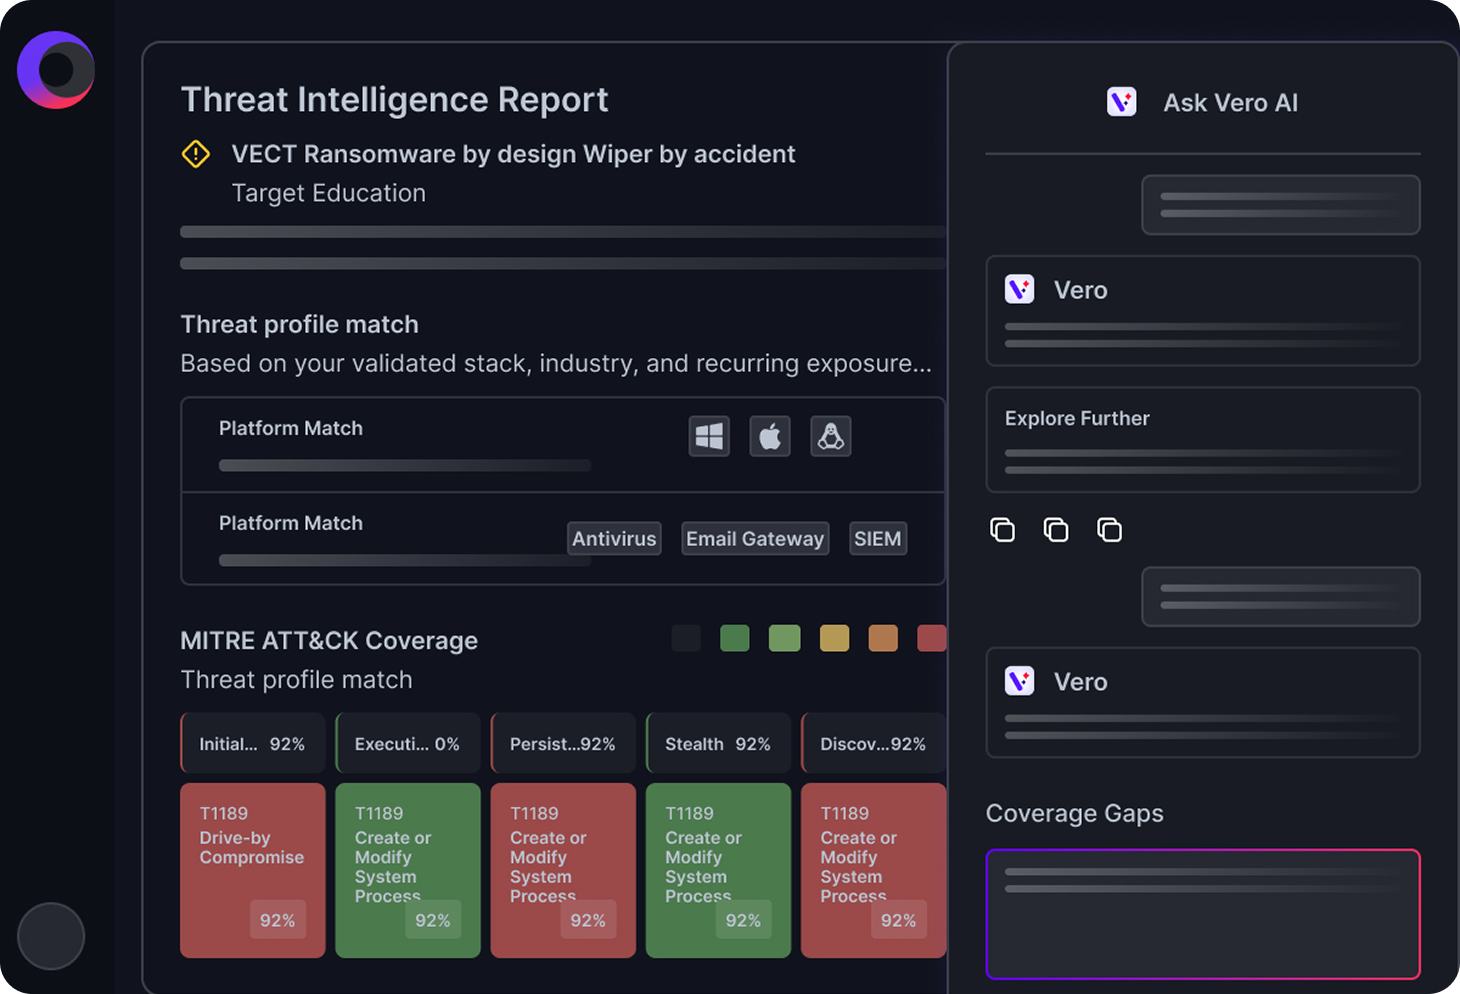
Attackers use AI to create and modify phishing emails, malware and evasive payloads at machine speed. Proving that your email gateway can stop these evolving threats demands a new approach. Cymulate integrates with your SEG (secure email gateway) and other security controls to go beyond validation and deliver agentic cyber defense engineering.
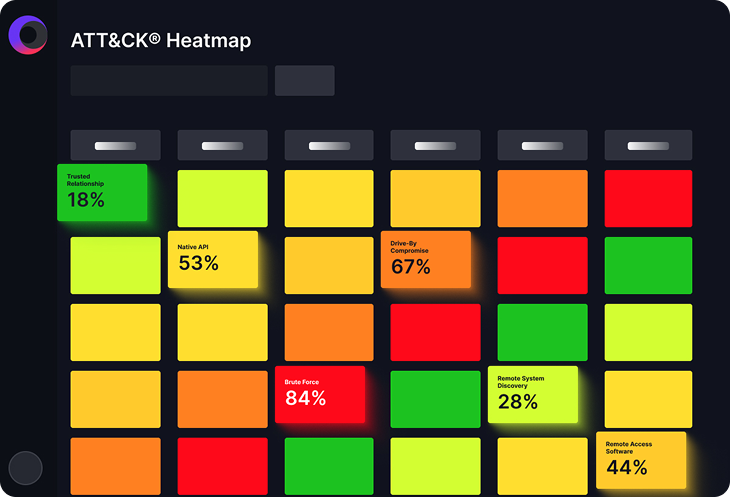
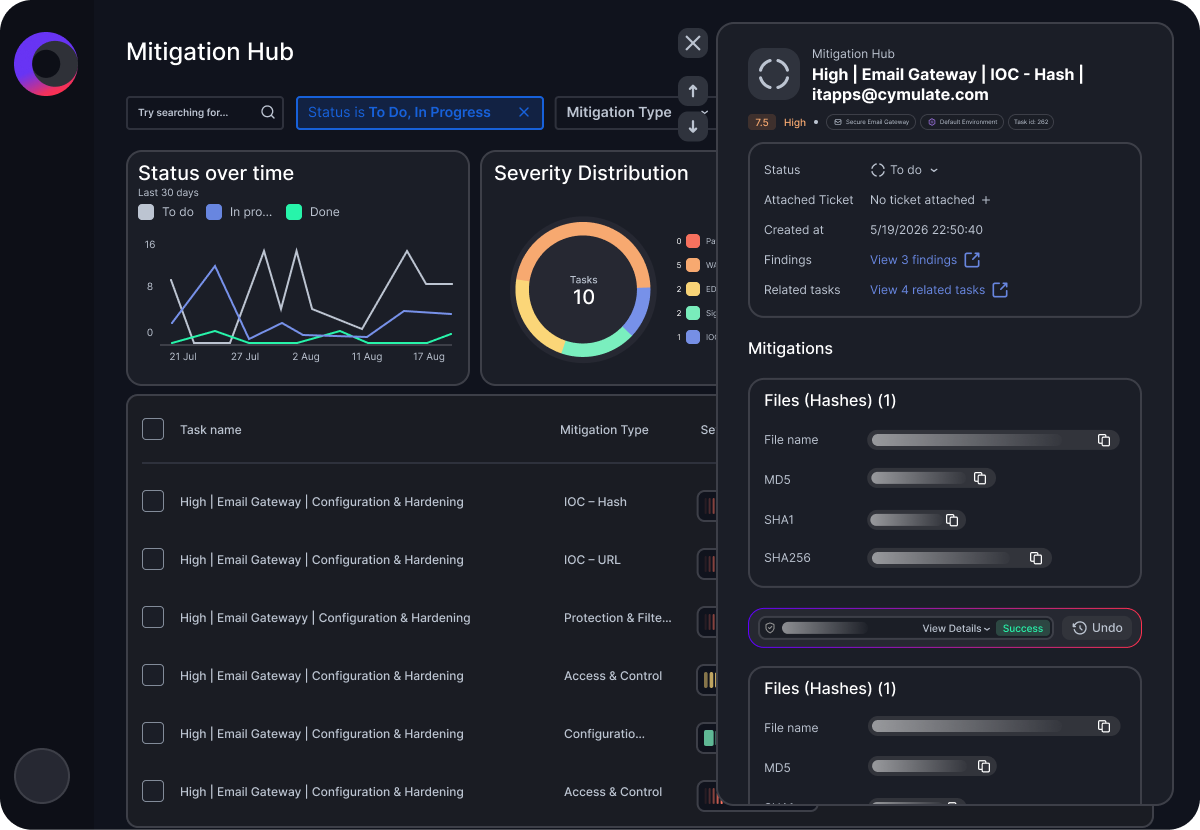
Powered by Vero AI, Cymulate proves email security effectiveness through production-safe attack simulation, prioritizes gaps with real-world impact and adapts your defenses with remediation guidance and streamlined mitigation workflows.
When Cymulate identifies a malicious file or link that reached the inbox, a misconfigured policy or a gap in email filtering, it provides guidance so you can close it. Every update is revalidated against the original attack scenario, so stronger email protection is proven, not assumed.
Instead of one more list of findings, Cymulate closes the risk-to-fix gap and continuously proves, prioritizes and adapts your email gateway against the threats targeting your inboxes.
SEG Validation and Optimization
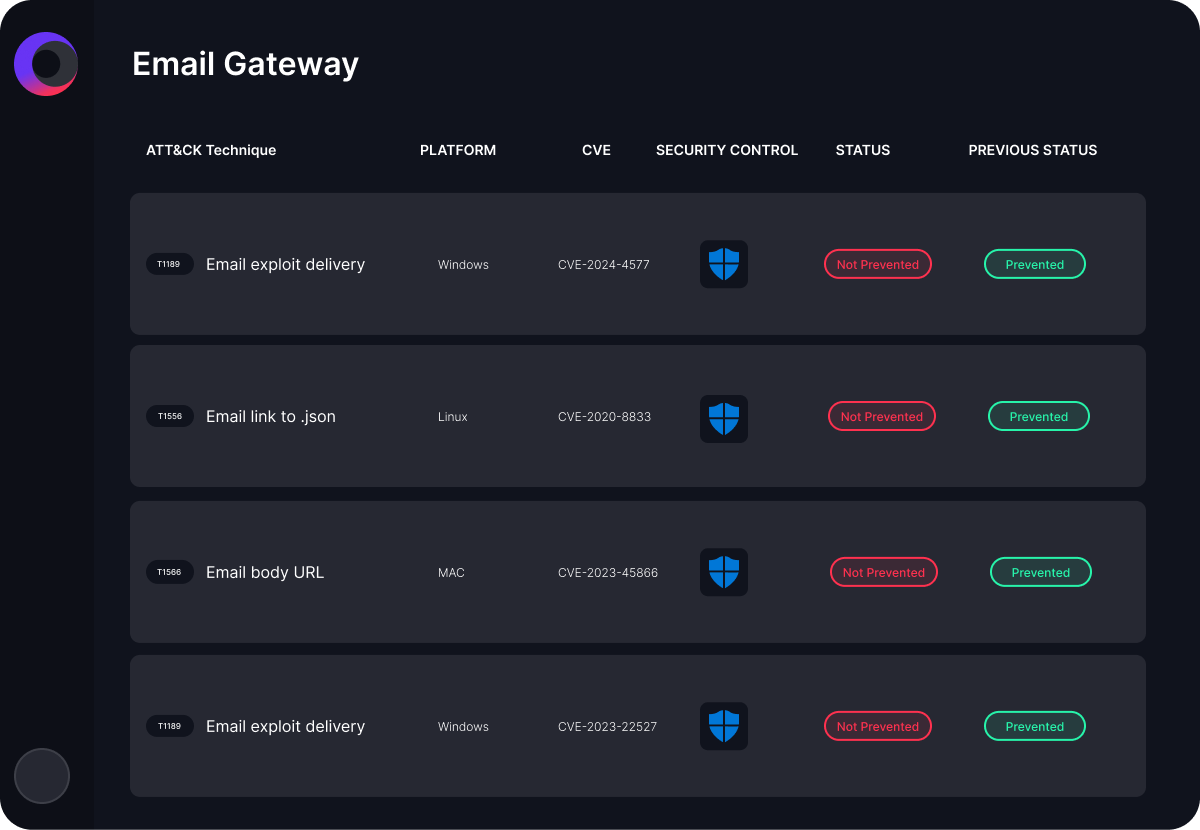
Results & Outcomes

90%
Threat prevention
AVG. of CYMULATE CUSTOMERS
60%
Boost in team efficiency
FINANCE CUSTOMER
50%
Better threat detection
AVG. of CYMULATE CUSTOMERS
Solution Benefits
Automated security validation
Identify gaps and weaknesses
Optimize security controls
Reduce exposure risk
Integrate with Your Secure Email Gateway to Tune and Optimize Email Security
Cymulate connects with your secure email gateway and other security controls to analyze how it handled each simulated email attack, show which malicious links, attachments and payloads reached the inbox and provide the mitigation guidance to tune gateway controls and policies.
What Our Customers Say
Featured Resources
View More Resources
11 Email Threats You Needs to Know
Email remains the primary entry point for cyberattacks. From nation-state actors to low-level cybercriminals, adversaries continually exploit the ubiquity and
The Stress from Email-based Threats
Read this practical guide for validating and optimizing email gateway controls.
Validation Best Practices: Email Gateway
Learn about security validation best practices for email gateway controls.
FAQs
Email gateway validation is the practice of testing whether your secure email gateway (SEG) actually catches phishing, business email compromise (BEC), and malware, instead of assuming it does based on configuration or vendor claims. Cymulate does this by sending simulated malicious emails through your live mail flow and checking what happened at every stage: quarantined, flagged, delivered with a warning, or landed in the inbox untouched. The result is evidence of how your email gateway performs against current attacker tactics, not just its published detection rates.
Cymulate sends simulated phishing, BEC, and malware emails through your actual mail path and correlates the outcome with alert and event data from your email gateway, showing whether it detected and acted on each technique and where alerting or filtering fell short. Because tests run against your live configuration and mail flow, results reflect your actual environment and policy setup, not a generic lab environment.
Cymulate simulates the full range of email-borne attack techniques, including phishing, spear phishing, business email compromise, and malware delivered through attachments or links across email and collaboration workloads. Simulations reproduce the delivery mechanism and behavior attackers use without carrying an actual malicious payload, so you can test detection and filtering effectiveness against realistic tactics without risking a real infection or compromise.
Yes. Cymulate’s email simulations are production-safe: they use the same delivery techniques as real phishing and malware campaigns without executing actual malicious code or putting mailboxes, endpoints, or data at risk. That safety is what allows testing to run continuously against your live email gateway and mail flow, rather than being limited to a lab environment or a periodic campaign window.
When a simulated email reaches the inbox instead of being quarantined or blocked, Cymulate flags it as a bypass, showing exactly which technique got through and why the gateway’s policy or filtering missed it. Cymulate then provides prioritized, actionable tuning guidance — what policy, rule, or filtering setting to adjust — and lets teams retest the same scenario after the change to confirm the bypass is closed. Findings route to the right owners through Cymulate’s workflow and ticketing integrations, so a bypass becomes a tracked fix rather than a one-off alert.
Continuously, or at minimum weekly: phishing and BEC tactics change faster than the annual or quarterly cycle most organizations use for email gateway testing today. Cymulate’s threat library updates daily, so new attacker techniques and lures can be tested against your gateway as they emerge rather than waiting for the next scheduled review. Continuous validation also catches configuration drift, such as a policy change or rule update that quietly opens a bypass between test cycles.