

Agentic Cyber Defense Engineering Model: 6 Requirements and 3 Foundations
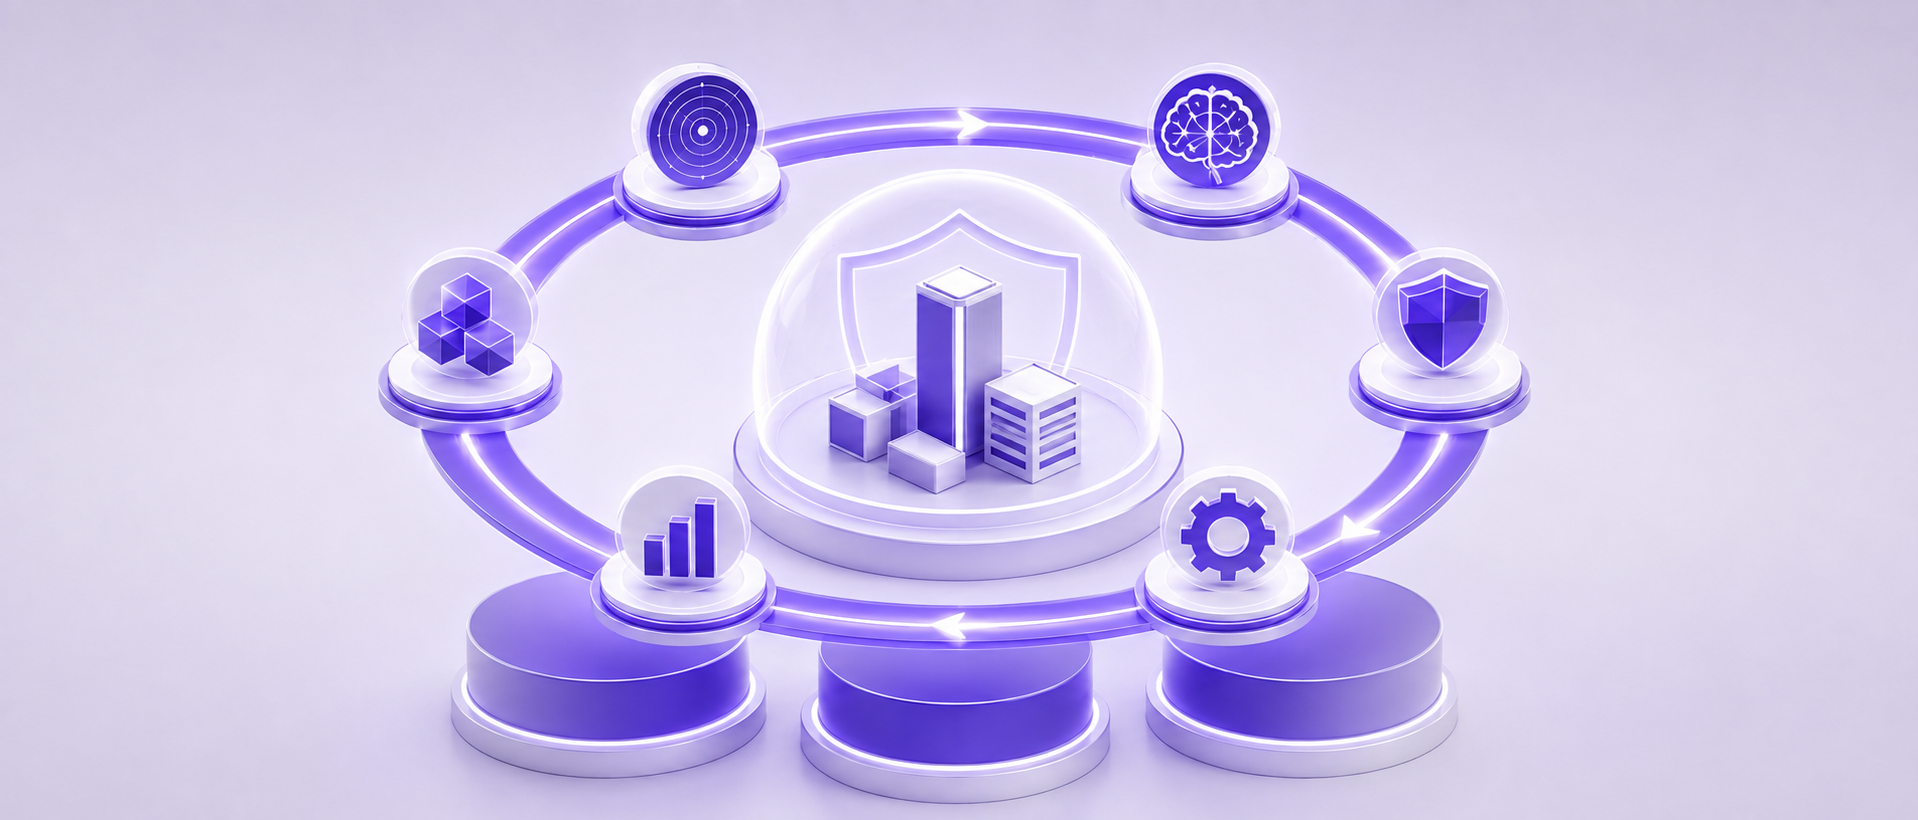
Agentic cyber defense engineering solution utilizes specialized agents to automate distinct security analyst activities and coordinate their work through a continuous closed loop. At a minimum, it must provide an end-to-end, event-driven process that adapts to changes in the threat landscape and environment and continuously proves and improves security defenses, without requiring teams to manually design workflows or manage each handoff.
It expands upon today’s automation with one integrated capability that moves from threat identification to verified improvement. Before diving into this framework, check out the first post in this series to learn all about agentic cyber defense engineering and check out our e-book.
This blog defines the six solution requirements and three foundations needed to deliver this capability continuously and at scale.
Key takeaways
- Automation is not the same as agentic AI. An agentic system is more than automation; it maintains profiles, monitors for triggers, applies context, automates analyst activities and adapts its next action based on the outcome.
- Agentic defense requires six connected capabilities. Specialized agents must profile the environment, tailor assessments, execute attacks safely, measure prevention and detection, prioritize gaps by actual risk and optimize controls.
- Three foundations power the closed loop. The three foundations essential to enabling coordinated, governed action at scale include purpose-built agentic AI, an intelligent control plane and a comprehensive and executable attack library.
Agentic Cyber Defense Engineering: The Closed-Loop Explained
Traditional automation executes activities along predefined paths. As an example, a scanner identifies a vulnerability, a workflow creates a ticket and a dashboard records its status. These steps improve efficiency, but practitioners must still decide which threats matter, determine what to test, configure the assessment, interpret the evidence and verify that mitigation worked.
An agentic model goes further. Specialized AI agents interpret changing conditions, determine the appropriate next action and perform activities traditionally handled by security analysts. They operate autonomously within defined objectives, permissions and guardrails, escalating when human judgment or approval is required.
Each phase follows a consistent pattern in a closed-loop: Trigger → Agent activity → Outcome → Context for the next phase. This loop responds to events such as an emerging threats, new vulnerability, security control change or failed validation instead of waiting for the next scheduled assessment.
Six Core Requirements
An agentic cyber defense engineering solution must satisfy these six core requirements.
1. Integrate and maintain a living contextual-based model (Profile)
Agentic cyber defense engineering integrates with security tools across the environment and continuously maintains a current model of the organization’s assets, exposures, security architecture, controls and relevant attacker behavior.
Integration with asset discovery, exposure management, threat intelligence, security controls and telemetry allows agents to understand the current environmental and risk context. Agents must correlate this data to maintain a living model and monitor for triggers such as new assets, vulnerabilities, control changes, threat campaigns or failed validations. Relevant changes update the model and automatically advance the closed loop.
Example: Agents identify a ransomware campaign targeting manufacturers as relevant, update the threat profile and trigger the tailor phase.
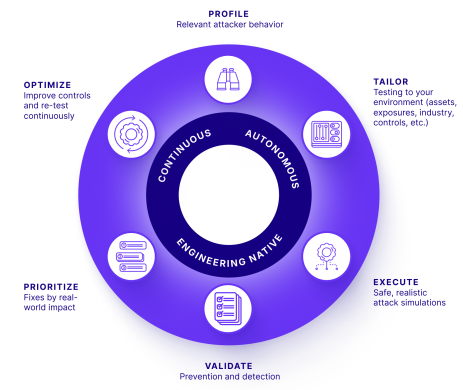
2. Configure and customize organization-specific assessments (Tailor)
Agentic cyber defense engineering applies threat and environmental context to automatically configure an attack assessment that is relevant to the organization.
Security operations often struggle to determine what to test and how to configure assessments correctly. This phase requires agents to apply threat and environmental context to select the right attack scenarios, environments, test points and integrations. By automating routine configuration, agents reduce the expertise and effort required while analysts focus on complex attack paths and high-risk threats.
Example: Agents apply the output of the environment profile to configure the attack scenarios, test points and integrations, then triggers the execute phase.
3. Safely execute realistic attacks (Execute)
Agentic cyber defense engineering automatically execute realistic, controlled and repeatable attack assessments without disrupting business operations.
Execute agents run attacks that mimic realistic adversary behavior. They enforce scope and safety boundaries, manage prerequisites, prevent operational impact and remove test artifacts when execution is complete. Human-defined policies specify where tests may run, which actions require approval and how operational risk is controlled.
Example: Agents verify all dependencies are met and safely executes the tailored ransomware scenarios across selected test points, remove test artifacts and record the evidence needed for validation.
4. Measure prevention and detection (Validate)
Agentic cyber defense engineering correlates attack activity with security controls and telemetry to prove what was prevented and detected.
Execution alone does not confirm that defenses worked. Validate agents determine which attack actions were blocked and query integrated platforms to identify the expected telemetry, alerts and detections. The outcome is measurable evidence of control performance and clear identification of prevention and detection gaps.
Example: Agents correlate the ransomware activity with security controls and telemetry to determine what was prevented, detected or missed.
5. Analyze gaps by demonstrated risk (Prioritize)
The agents must correlate validation evidence with threat relevance, exploitability, attack paths, control performance and business impact.
Agents calculate risk scores by correlating validation evidence with threat relevance, demonstrated exploitability, attack-path reachability, control performance, asset criticality and business impact. This moves prioritization beyond static severity scores to identify the exposures attackers can actually use and the gaps most likely to affect critical assets.
Example: Agents score and prioritize identified ransomware prevention and detection gaps based on demonstrated exploitability, control performance, attack-path context and business impact.
6. Configure controls and improve security (Optimize)
Agentic cyber defense engineering generates and automatically deploys approved mitigations through security-control integrations
For prevention gaps, agents push relevant indicators of compromise to enforcement controls. For detection gaps, they generate and deploy new detection rules in the vendor-specific formats required by each platform. All changes remain governed by defined policies and approval requirements.
After deployment, agents detect the control change and trigger the closed loop to rerun the relevant attack assessment. The resulting evidence confirms whether the new mitigation prevents or detects the activity as intended.
Example: Agents push ransomware indicators to a prevention control and deploy a vendor-specific rule for a detection gap. Agents detect the changes and trigger the assessment process to verify both outcomes.
Requirements at a Glance
| Requirement | Required Inputs | Expected Outcome |
| 1. Profile — Integrate and maintain a living contextual model | Asset discovery, exposure management, threat intelligence, security control and telemetry feeds | A continuously current model of assets, exposures, architecture, controls and relevant attacker behavior that automatically advances the closed loop |
| 2. Tailor — Configure organization-specific assessments | Maintain current environment/threat profile, and configure test points, environments and tool integrations | An attack assessment scoped and configured to the organization's specific environment, without manual setup |
| 3. Execute — Safely run realistic attacks | Tailored attack scenarios, defined scope and safety boundaries, approval and escalation policies | Controlled, repeatable execution of realistic attacks with no disruption to business operations |
| 4. Validate — Measure prevention and detection | Attack execution results with integrated security control and telemetry data | Measurable evidence of what was prevented, detected or missed |
| 5. Prioritize — Analyze gaps by demonstrated risk | True risk scores by correlating validation evidence, threat intelligence, exploitability, attack-path reachability and business impact data | A stacked ranked list of exposures based on demonstrated impact rather than static severity scores |
| 6. Optimize — Configure controls and improve security | Mitigate priority exposures with vendor specific prevention and detection improvements | Auto-deployed, governed mitigations with automatic re-validation that mitigation was successful |
Three Technical Foundations That Power the Closed Loop
The six phases define what the solution must accomplish. Three foundations enable it to operate continuously and at scale.
1. Purpose-Built Agentic AI
The AI architecture must be purpose-built for cybersecurity and include specialized agents, shared context and a framework for coordinating decisions and actions across the closed loop. It must support event-driven reasoning, adaptive planning and governed access to security tools and data.
The design must also include role-based permissions, approval controls, audit trails and evidence explaining consequential actions.
2. An Intelligent Cyber Defense Engineering Control Plane
The control plane coordinates agents, triggers and integrations across the closed loop. It maintains shared context, assigns work, tracks outcomes, enforces policies and determines the next action. By connecting asset systems, validation infrastructure, security controls and remediation workflows, it enables governed, auditable coordination rather than fragmented automation.
3. A Comprehensive, Executable Attack Library
The attack library converts threat intelligence into safe, executable scenarios. It must cover relevant techniques and threat vectors, support realistic multi-step attacks and include the context agents need to select, configure, execute and interpret assessments safely
Evaluation Checklist for Security Leaders
Security leaders who are evaluating agentic cyber defense engineering solutions should use the checklist below as a guide.
☐ Operates as a single integrated capability across all six requirements, not a set of disconnected AI features.
☐ Moves continuously from environmental or threat change to relevant testing, without waiting for a scheduled assessment.
☐ Produces measurable evidence of what was prevented, detected or missed, not just a completed task log.
☐ Prioritizes action by demonstrated risk, exploitability, attack path reachability and business impact, rather than static severity scores.
☐ Deploys approved mitigations and automatically re-validates them to confirm the fix worked.
☐ Enforces governance throughout: defined permissions, approval controls, policy-bounded execution and audit trails for every consequential action.
Organizations that do not adopt this model remain constrained by human latency, widening exposure windows, and increasing cyber and business risk.
Coming next in the series
This is the second blog in a series all about agentic cyber defense engineering. You can read the previous blog Agentic Cyber Defense Engineering: A New Model for AI-Powered Cyber Defense.
In our next blog, “Inside the Agentic Cyber Defense Engineering Architecture: How it Works”, we will reveal how specialized agents execute governed security routines and coordinate across integrated security tools to continuously improve defenses.
Until then, download the Agentic Cyber Defense Engineering e-book for a deeper look at the operating model and how it can help organizations strengthen threat resilience at machine speed.
Ready to explore how agentic cyber defense engineering can transform your security program?
Featured Resources
View More Resources
Agentic Cyber Defense Engineering: A New Model for AI-Powered Cyber Defense
See how agentic cyber defense engineering uses AI agents and continuous validation to improve defenses at machine speed.
From AI Hype to AI Risk: A New Security Reality
Join Cymulate CTO Avihai Ben-Yossef: explore AI-driven attacks and how continuous validation helps defenders prioritize.
Cymulate Cowork
Use AI agents and automated routines to validate exposures and streamline cyber defense engineering.