Frequently Asked Questions

Product Overview & Agentic Cyber Defense Engineering

What is Cymulate and what does it do?

Cymulate is an AI-powered cyber defense engineering platform that helps security teams prove, prioritize, and improve their cyber defenses against real threats and exposures. It operates a continuous loop—prove, prioritize, improve, and re-prove—so organizations can validate their security posture, automate mitigation, and drive measurable risk reduction. Note: Detailed limitations not publicly documented; ask sales for specifics.

What is agentic cyber defense engineering and how does Cymulate use it?

Agentic cyber defense engineering is an approach where autonomous, goal-driven agents continuously assess exposure, prioritize findings, recommend remediation, and validate mitigation in dynamic environments. Cymulate applies this model through features like Vero AI and Mitigation Hub, enabling security teams to move from static assessments to adaptive, outcome-focused defense cycles. Note: Agentic capabilities require integration with organizational workflows; effectiveness may vary based on environment complexity.

What is Cymulate Vero AI and how does it support security operations?

Cymulate Vero AI is a domain-specific agentic AI system designed to interpret exposure data in context, identify actionable risks, coordinate remediation, and validate mitigation through re-testing. Unlike generic AI chatbots, Vero AI is integrated with Cymulate's platform data and workflows, supporting the operational cycle of defense engineering. Note: Vero AI's effectiveness depends on the quality of integrated data and organizational adoption of agentic workflows.

What is the Mitigation Hub and how does it help security teams?

The Mitigation Hub is a Cymulate capability that consolidates and organizes remediation work, prioritizes actions based on impact and feasibility, and provides a workflow from issue identification to resolution. It enables teams to verify whether mitigation actions actually reduce risk, closing the loop between findings and fixes. Note: The Mitigation Hub's value depends on stakeholder alignment and integration with existing remediation processes.

Features & Capabilities

What are the key features and benefits of Cymulate?

Cymulate offers continuous threat validation, exposure validation, AI-powered context mapping, a comprehensive threat library, automated mitigation, detection engineering, and attack surface management. Customers report a 30% increase in threat prevention, 50%-90% improvement in detection, 52% reduction in critical exposures, and 60% boost in operational efficiency. Note: Effectiveness may vary based on deployment scope and integration with existing tools.

What integrations does Cymulate support?

Cymulate supports over 50 integrations across SIEM (e.g., CrowdStrike Falcon LogScale), EDR and anti-malware (CrowdStrike Falcon, Carbon Black EDR, Cisco Secure Endpoint), cloud security (AWS GuardDuty, Check Point CloudGuard), web gateways (Cisco Umbrella), vulnerability management (Rapid7 InsightVM), SOAR, Active Directory, and ticketing systems. For a full list, visit Cymulate's technology alliances page. Note: Integration availability may depend on your package and environment.

What security and compliance certifications does Cymulate have?

Cymulate holds SOC2 Type II, ISO 27001:2013, ISO 27701, ISO 27017, and CSA STAR Level 1 certifications. The platform leverages AWS data centers certified for ISO 27001:2022, PCI DSS Service Provider Level 1, and SOC 2/3 Type II. Note: Certification scope may vary; review Cymulate's security overview for details.

Pain Points & Use Cases

What problems does Cymulate solve for security teams?

Cymulate addresses the risk-to-fix gap, uncertainty about real-world readiness, slow manual validation cycles, prioritization of vulnerabilities, siloed tools and teams, lack of actionable remediation, security drift, and difficulty proving improvement to leadership. For example, Hertz Israel achieved an 81% reduction in cyber risk within four months using Cymulate (case study). Note: Results depend on organizational maturity and adoption of continuous validation practices.

Who can benefit from using Cymulate?

Cymulate is designed for organizations of all sizes and industries, especially CISOs, SecOps leaders, detection engineers, red teams, vulnerability management teams, GRC/compliance teams, and IT/cloud teams. It is best suited for teams seeking measurable risk reduction, continuous validation, and actionable remediation. Note: Teams with highly specialized or legacy environments may require additional customization.

What business impact can customers expect from Cymulate?

Customers report a 30% increase in threat prevention, 50%-90% improvement in detection, 52% reduction in critical exposures, 60% boost in operational efficiency, and 40X faster threat validation. Hertz Israel achieved an 81% reduction in cyber risk in four months. Note: Actual results may vary based on deployment scope and organizational readiness.

Implementation & Ease of Use

How long does it take to implement Cymulate and how easy is it to start?

Cymulate is built for quick deployment, with an agentless mode that requires no additional hardware or complex configuration. Customers can start running simulations almost immediately after setup. The platform features a user-friendly interface and provides extensive support resources, including email/chat support, webinars, and technical documentation. Note: Implementation time may increase for highly customized environments.

What feedback have customers given about Cymulate's ease of use?

Customers consistently highlight Cymulate's quick implementation, intuitive dashboard, and actionable insights. For example, Raphael Ferreira, Cybersecurity Manager, stated: "Cymulate is easy to implement and use—all you need to do is click a few buttons, and you receive a lot of practical insights into how you can improve your security posture." Note: User experience may vary based on organizational processes and technical expertise.

Pricing & Plans

What is Cymulate's pricing model?

Cymulate operates on a subscription-based pricing model tailored to each organization's needs. Pricing is determined by the package selected, number of assets, and scenarios chosen. For a detailed quote, schedule a demo at Cymulate's demo page. Note: Exact pricing is not publicly listed and requires direct consultation.

Competition & Comparison

How does Cymulate compare to AttackIQ?

Cymulate offers AI-driven remediation guidance, a broader and continuously updated attack scenario library, and an AI Copilot for automated test generation. Cymulate is noted for faster and easier deployment compared to AttackIQ. AttackIQ may be preferred by organizations seeking a different approach to adversary simulation. Note: Cymulate's advanced automation and library depth are differentiators; AttackIQ may offer unique integrations or workflows not covered by Cymulate.

How does Cymulate compare to Mandiant Security Validation?

Cymulate is recognized for continuous innovation, AI and automation, and a broader approach to exposure validation. Mandiant Security Validation has seen less innovation in recent years but may be preferred by organizations with existing Mandiant workflows. Note: Cymulate's AI-driven features and exposure management focus are differentiators; Mandiant may offer unique threat intelligence sources.

How does Cymulate compare to Pentera?

Cymulate provides deeper assessment, full-kill chain coverage (including cloud control validation), and actionable remediation guidance. Pentera focuses on attack path validation but lacks comprehensive capabilities and production-ready remediation outputs. Pentera may be suitable for organizations prioritizing attack path validation over full exposure management. Note: Cymulate's breadth of coverage is a differentiator; Pentera may offer specialized attack path analysis features.

How does Cymulate compare to Picus Security?

Cymulate covers the full kill chain and cloud control validation, while Picus Security focuses on breach and attack simulation (BAS) with on-prem options. Cymulate offers a more complete exposure validation platform. Picus may be preferred by organizations seeking on-prem BAS solutions. Note: Cymulate's cloud and kill chain coverage are differentiators; Picus may offer unique BAS features for on-prem environments.

How does Cymulate compare to SafeBreach?

Cymulate is noted for innovation, automation, the largest attack library, and a full CTEM solution. SafeBreach focuses on breach and attack simulation but may not offer the same breadth of exposure validation or automation. SafeBreach may be suitable for organizations seeking a BAS-focused approach. Note: Cymulate's CTEM and automation are differentiators; SafeBreach may offer unique BAS scenarios.

Resources & Further Reading

Where can I find technical documentation and resources about Cymulate?

Access Cymulate's Resource Hub for industry reports, whitepapers, case studies, and technical guides at Cymulate's Resource Hub. For specific product data sheets, see the Threat Studio Data Sheet and Detection Engineering Automation Guide. Note: Some resources may require registration.

Cymulate named a Customers' Choice in 2026 Gartner® Peer Insights™
Learn More
New: Cymulate Cowork for Agentic Cyber Defense Engineering
Learn More
New Bitsight Integration: Turn Threat Intelligence into Validated Security
Learn More
Introducing Cymulate Vero AI for Agentic Cyber Defense Engineering
Learn More

Preparing for the AI Onslaught at Black Hat 
By: Brian Moran, VP of Product Marketing

July 28, 2026

AI will be everywhere at Black Hat 2026. Again. 

Thankfully, the conversation is finally moving past booth signage, dashboard sparkle and “ask me anything” copilots toward something more useful: AI embedded into how security teams prioritize, investigate, remediate and prove outcomes.  

As attackers use AI to move faster and scale broader, defenders need more than another chat window. They need acceleration without more headcount, more tool sprawl or more brittle automation. 

At Cymulate, we see this as a turning point. AI in cybersecurity can’t stop at chat interfaces or isolated “copilots.” It needs to become operational: taking action, orchestrating workflows and continuously improving security posture based on real-world evidence. That’s why we’ve been investing in agentic cyber defense engineering -- a practical approach that uses autonomous, goal-driven agents to help security teams measure exposure, prioritize what matters and drive mitigation from findings to fixes. 

And at Black Hat, we’ll be sharing more about what’s next. If you are in Las Vegas for the conference, please make sure you stop by booth 1369 or schedule a meeting. 

From AI assistants to agentic cyber defense engineering 

Security teams have experimented with automation for years: playbooks, scripts, SOAR and rule-based workflows. Those tools can be effective, but they often require constant tuning and assume that the environment is static. Reality is the opposite -- modern environments change daily and the threat landscape changes hourly. 

Agentic systems are designed for that reality. Instead of executing a rigid sequence of steps, they pursue an objective, adapt to constraints and collaborate with people and other systems. Applied to cyber defense engineering, this means moving beyond “tell me what’s wrong” toward “help me fix what’s wrong, validate it and keep it fixed.” 

We introduced this approach in our post on agentic cyber defense engineering, outlining how agentic capabilities can continuously translate security intent into measurable outcomes across environments and controls. (Read more at Introducing Agentic Cyber Defense Engineering.) 

In practical terms, an agentic defense engineering model can: 

  • Continuously assess exposure (not just compliance) 
  • Turn raw findings into prioritized, context-rich tasks 
  • Recommend and guide remediation actions 
  • Validate whether mitigation works—then re-test as conditions change 

That loop -- test, learn, mitigate, verify -- is where AI delivers real value. 

Meet Cymulate Vero AI: purpose-built for agentic defense engineering 

One of the biggest challenges with “AI everywhere” is separating signal from noise. Generic AI models can summarize, generate and chat -- but effective cyber defense requires domain-specific reasoning, knowledge of the environment and a tight feedback loop with validation. 

That’s where Cymulate Vero AI comes in. In our post on Vero AI and agentic cyber defense engineering, we described how Vero AI is designed to bring agentic capabilities into security operations in a way that is grounded in the Cymulate platform data, exposure context and mitigation workflows.
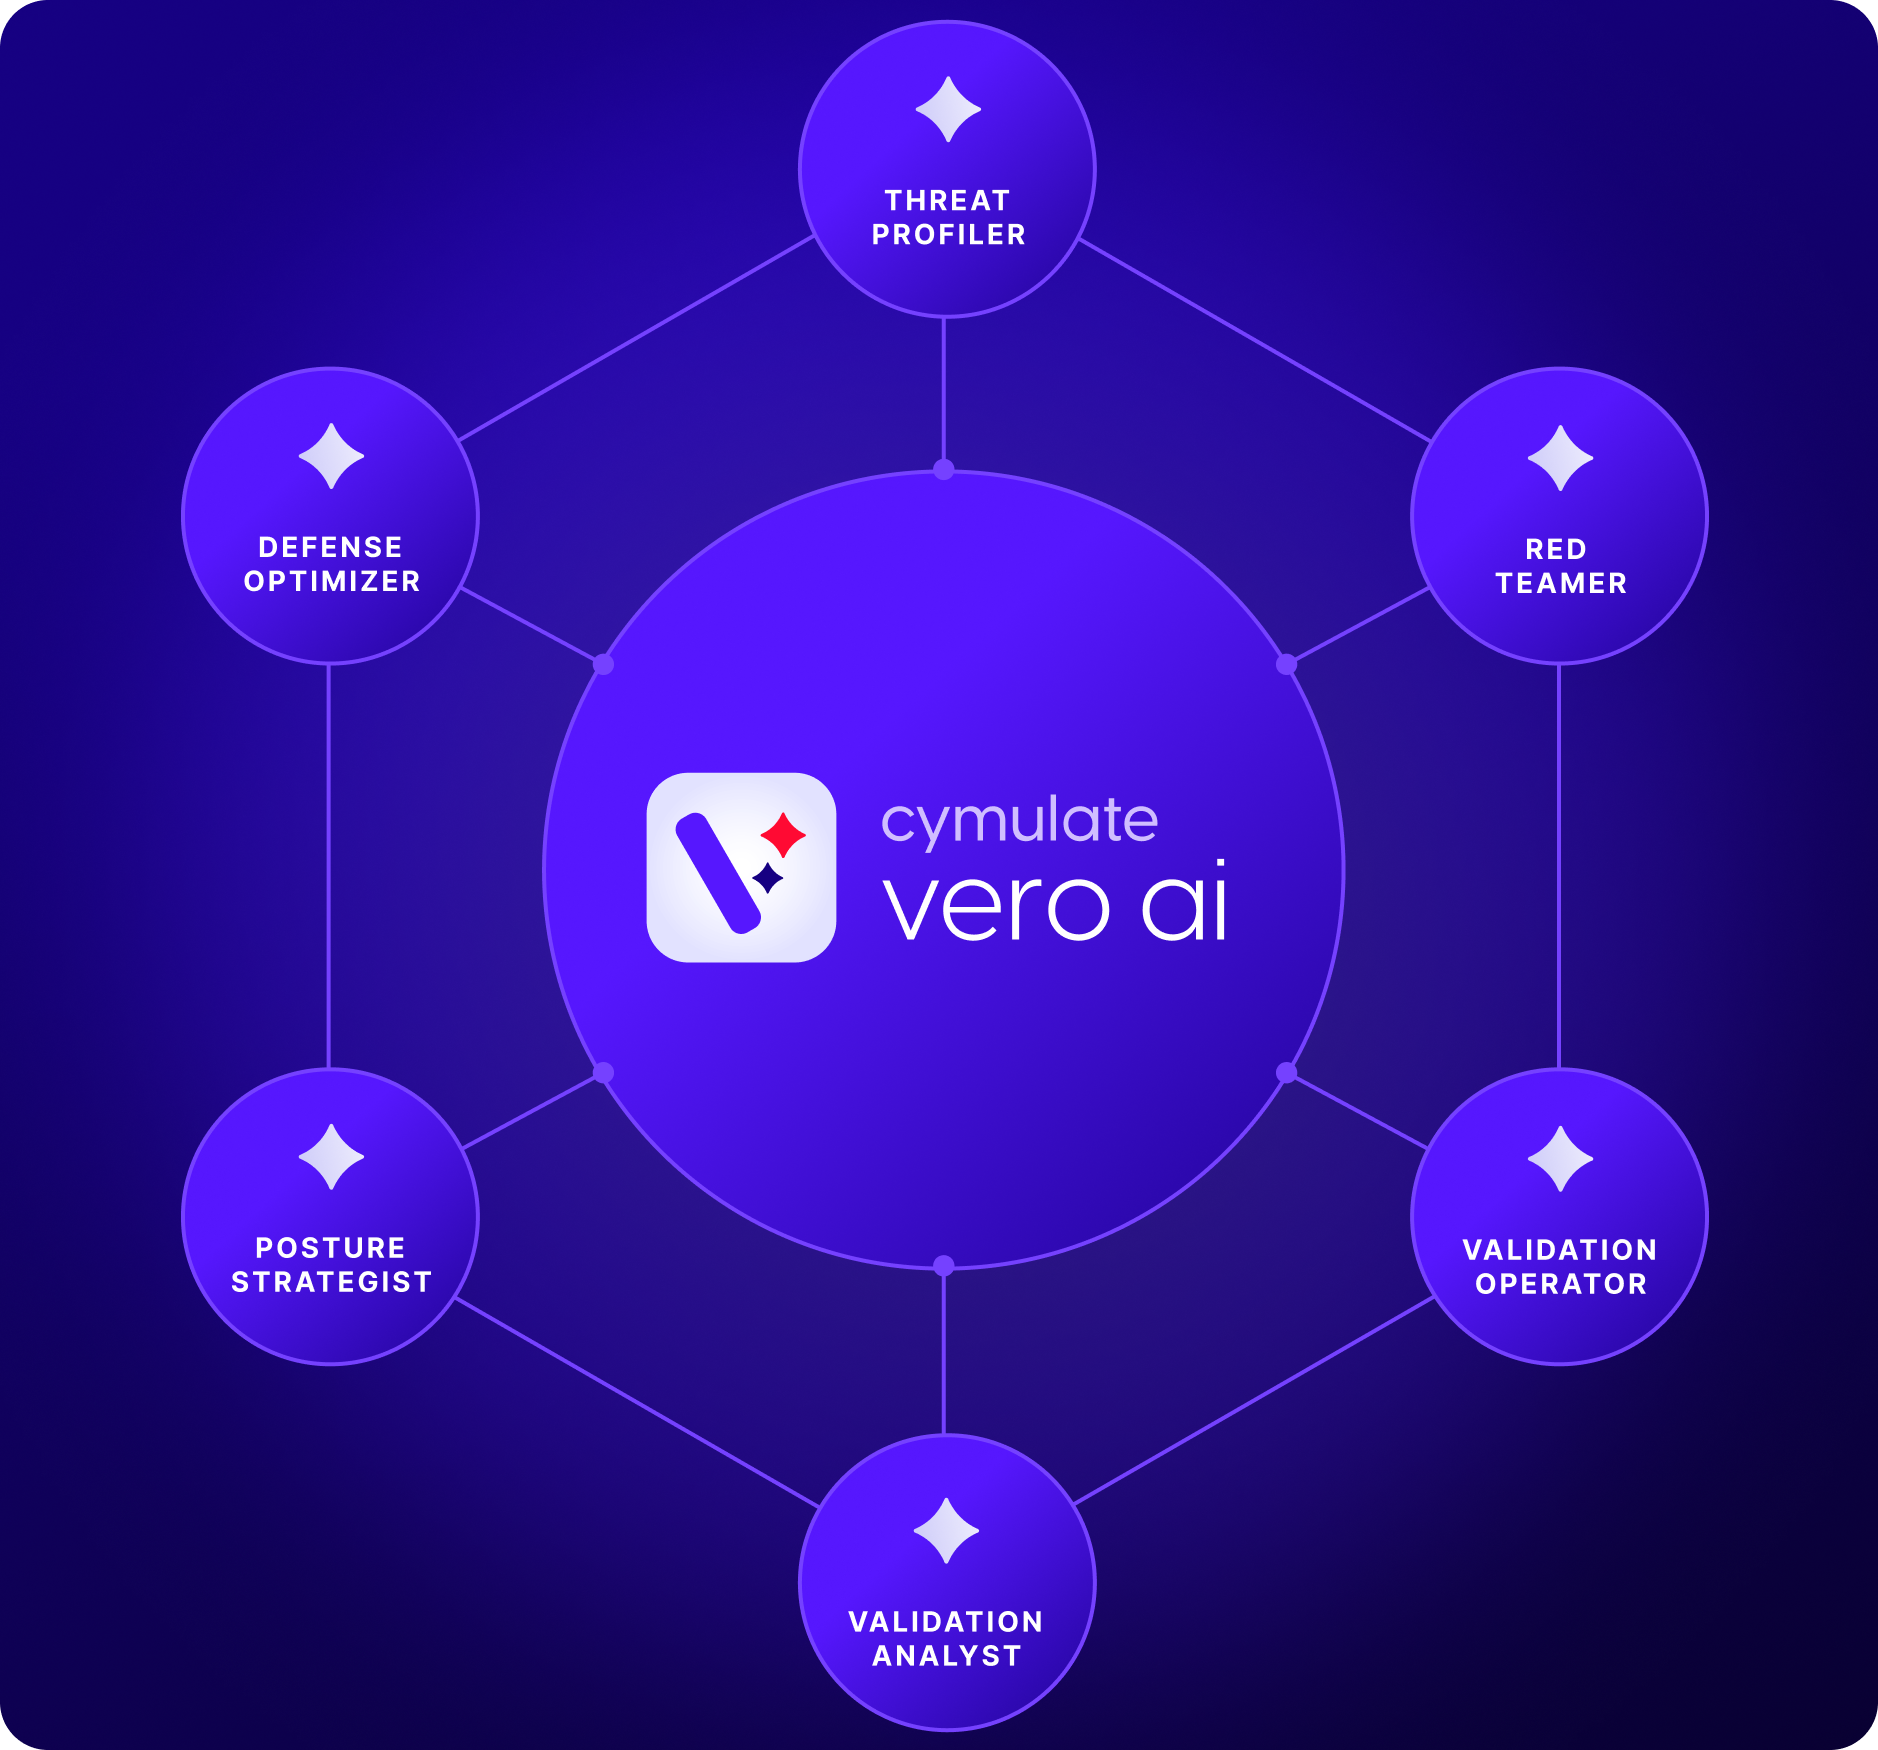
Think of Vero AI as more than a conversational layer. It’s a system that can: 

  1. Interpret exposure data in context (assets, controls, configurations, attack paths, and business risk) 
  2. Identify what’s actionable -- and what’s merely interesting 
  3. Help coordinate remediation by turning insights into concrete steps 
  4. Close the loop with validation by re-testing and measuring progress 

In other words, Vero AI is designed to support the operational cycle of defense engineering—not just the presentation of information. 
image
Further reading
The Truth About Your Security: Why We Built Cymulate Vero AI

Meet Cymulate Vero AI: the agentic AI system that validates threats, proves defenses and drives action.

Read More

Every security leader knows the pain: assessments generate findings, findings generate tickets and tickets generate… delay. Even organizations with mature processes struggle to connect discovery to remediation at the pace the business demands. 

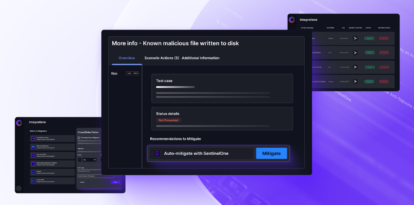
That’s why Cymulate launched Mitigation Hub, a capability that focuses specifically on driving remediation outcomes, helping teams go from “we found issues” to “we fixed issues” and “we verified the fixes.” Our post on Mitigation Hub details how it brings structure and prioritization to the remediation process, aligning stakeholders and making it easier to track mitigation progress over time.
image
Further reading
Mitigation Hub Turns Findings into Fixes

Turn validated security findings into prioritized remediation tasks that accelerate risk reduction.

Read More

In an AI-enabled world, the goal isn’t to produce more findings faster. The goal is to reduce exposure faster. Mitigation Hub supports that goal by: 

  • Consolidating and organizing remediation work 
  • Helping prioritize based on impact and feasibility 
  • Providing a clear workflow from issue identification to resolution 
  • Enabling teams to verify whether mitigation actions actually reduce risk 

This is where agentic capabilities become especially powerful. An agent can help identify the most impactful fixes, suggest remediation steps, coordinate stakeholders and continuously validate the results -- reducing back-and-forth and speeding up the path to measurable risk reduction.

What we’re excited to share at Black Hat 

At Black Hat, Cymulate will continue the conversation about AI by focusing on what matters most: turning AI into measurable security outcomes. 

We’ll be discussing how agentic cyber defense engineering can help organizations: 

  • Move from periodic assessments to continuous exposure validation 
  • Translate technical signals into prioritized, actionable work 
  • Accelerate mitigation across teams and tools 
  • Establish an evidence-based feedback loop that proves progress 

And yes -- we’ll have more to announce at Black Hat about how Cymulate is expanding what’s possible with agentic capabilities across the platform. 

The road ahead: outcomes over hype 

AI will be everywhere at Black Hat. The organizations that get the most value won’t be the ones that simply “add AI” to their stack. They’ll be the ones who use AI to tighten the cycle between discovery, decision, action and verification. 

That’s the promise of agentic cyber defense engineering -- and the direction Cymulate is building toward. 

We look forward to connecting at Black Hat and sharing what’s next. Come see us at booth 1639.
Cymulate Exposure Validation makes advanced security testing fast and easy. When it comes to building custom attack chains, it's all right in front of you in one place.
Mike Humbert, Cybersecurity Engineer
DARLING INGREDIENTS INC.
Learn More
GET A PERSONALIZED DEMO

Ready to see Cymulate in action?