

Endpoint Security Validation
Continuously test and optimize endpoint defenses against the latest threats.
Sophisticated phishing and ransomware attacks continue to rise as adversaries target endpoint devices.
75%
Cyber attacks
are malware free
Source: crowdstrike
30%
Attacks bypass
AV and EDR controls
Source: Morphisec
$4.88M
Average cost of an
endpoint data breach
Source: IBM
Agentic Cyber Defense Engineering for Endpoint Security
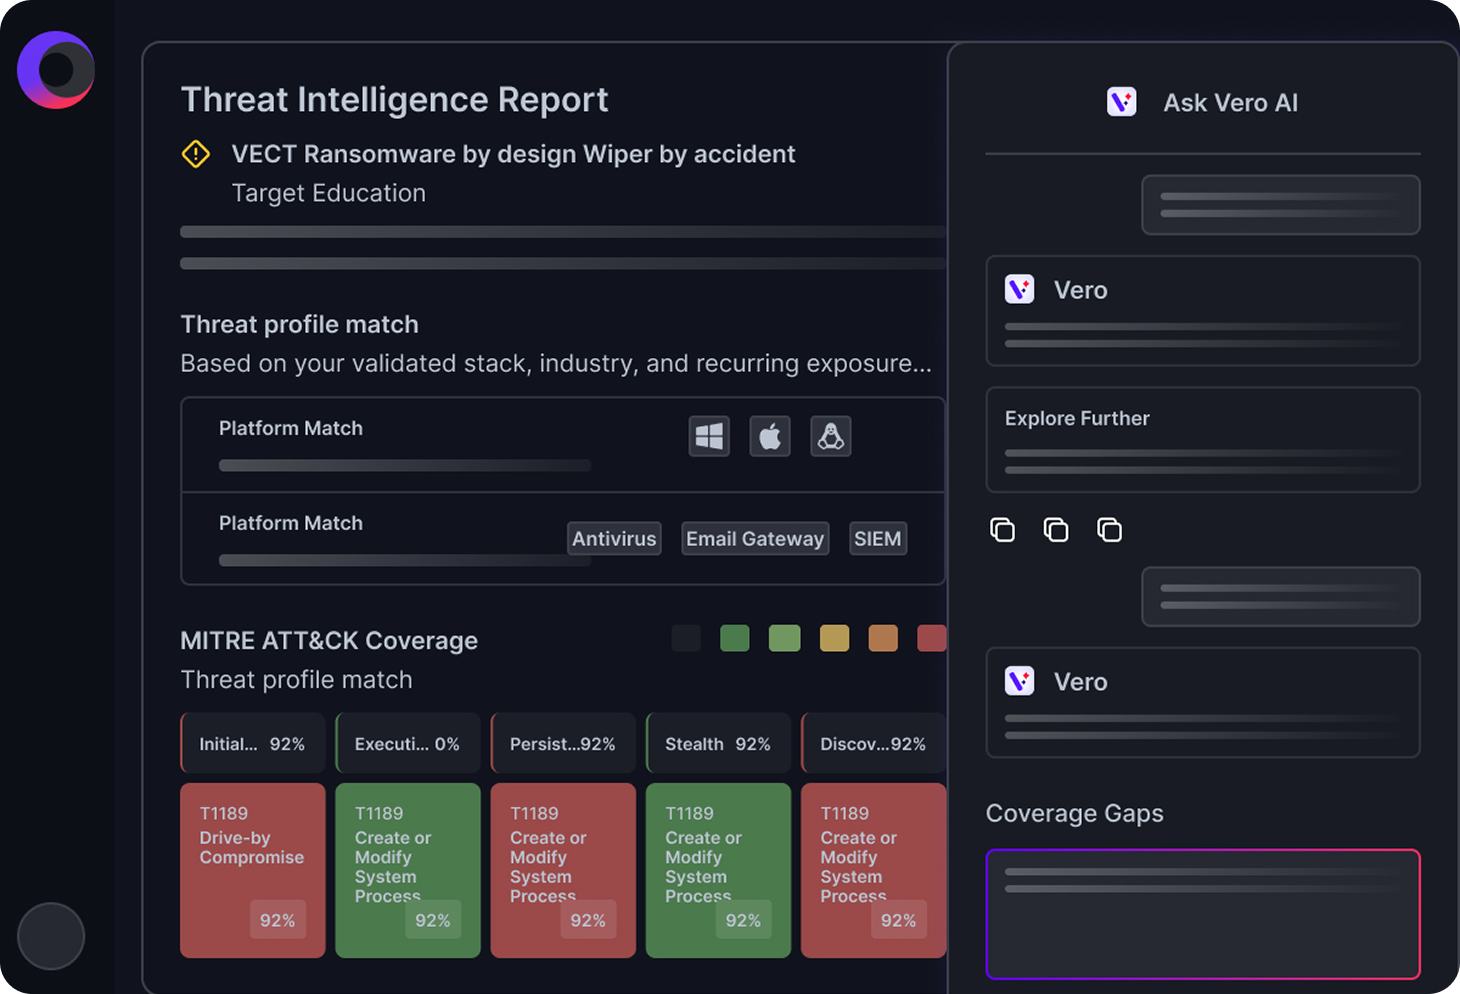
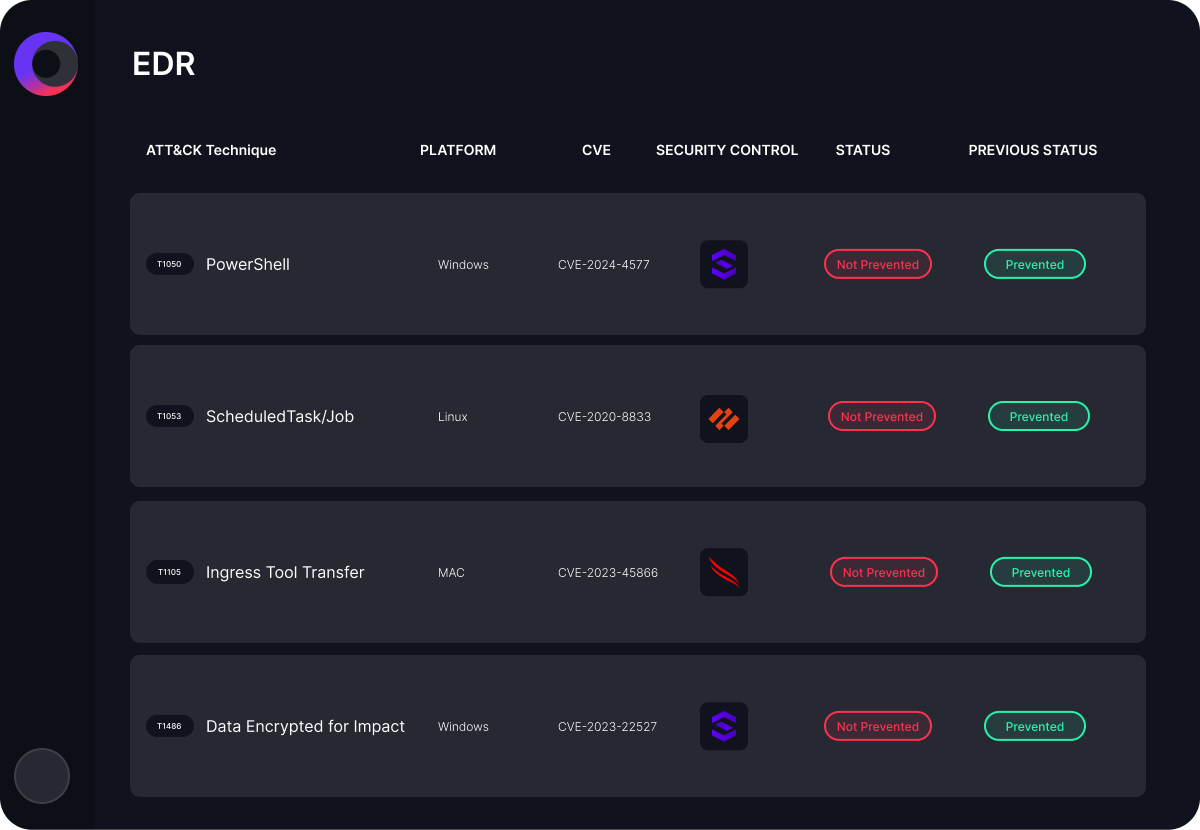
Today’s AI-powered threats demand a new approach to prove, prioritize and adapt your cybersecurity at machine speed. Cymulate integrates with your EDR (endpoint detection and response) to go beyond validation and deliver agentic cyber defense engineering.
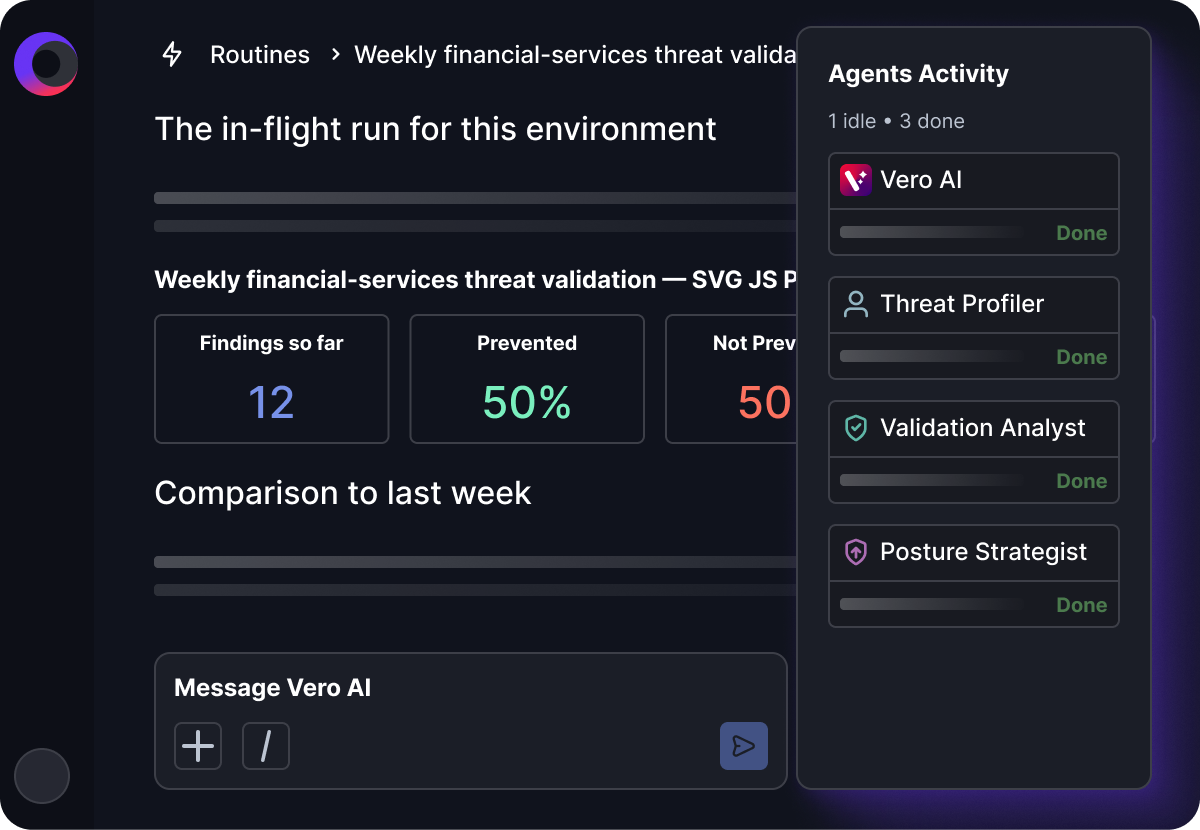
Powered by Vero AI, Cymulate proves endpoint control effectiveness through production-safe attack simulation, prioritizes gaps with real-world impact and adapts your defenses by pushing vendor-specific control updates.
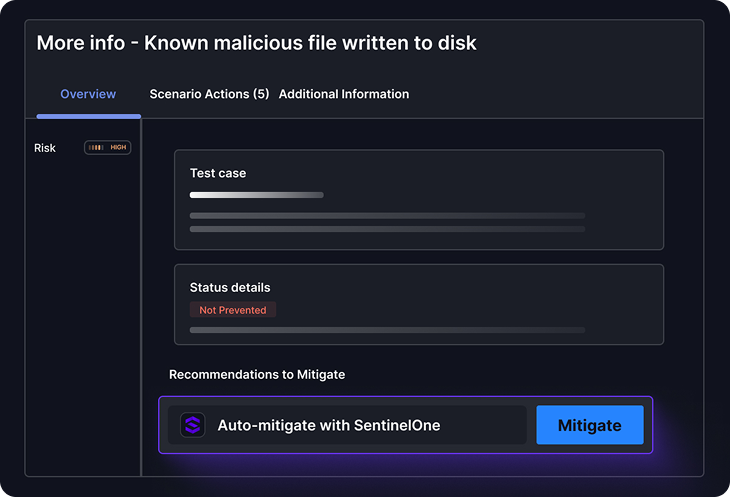
When Cymulate identifies a missed detection, a misconfigured control or a gap in endpoint protection, it quickly closes it by generating and deploying targeted detection rules and IoCs directly to your EDR. Every update is revalidated against the original attack scenario, so stronger endpoint protection is proven, not assumed.
Instead of one more list of findings, Cymulate closes the risk-to-fix gap and continuously proves, prioritizes and adapts your EDR against the threats targeting your environment.
EDR Validation and Optimization

Results & Outcomes

90%
Threat prevention
AVG. of CYMULATE CUSTOMERS
60%
Boost in team efficiency
FINANCE CUSTOMER
50%
Better threat detection
AVG. of CYMULATE CUSTOMERS
Solution Benefits
Accelerate remediation
Reduce manual SecOps effort
Prove improved protection
Continuously optimize endpoint security

Integrate with your EDR to Tune and Optimize Endpoint Security
Cymulate connects with your EDR and endpoint security to analyze its response to attack simulations, understand why an attack was missed and push updates for both IoCs and behavioral detection rules.
What Our Customers Say About Us
Featured Resources
View More Resources
Control Validation and Optimization
Continuously validate and optimize security controls to improve prevention, detection and response effectiveness.
Cymulate Auto Mitigation
Go beyond validation with automated threat mitigation. Test, detect, and block threats daily to optimize prevention and harden defenses.
Self-Healing Endpoint Security
Validate and optimize SentinelOne endpoint security with Cymulate to uncover gaps and improve threat detection.
FAQs
Endpoint security validation is the practice of testing whether your EDR and anti-malware controls actually detect and stop real attacker behavior, rather than assuming they do based on vendor claims or default configurations. Cymulate does this by running attack simulations mapped to MITRE ATT&CK against your endpoints and comparing what the attack did against what your EDR logged, alerted on, or blocked. The result is evidence of where your endpoint controls hold up and where they don’t.
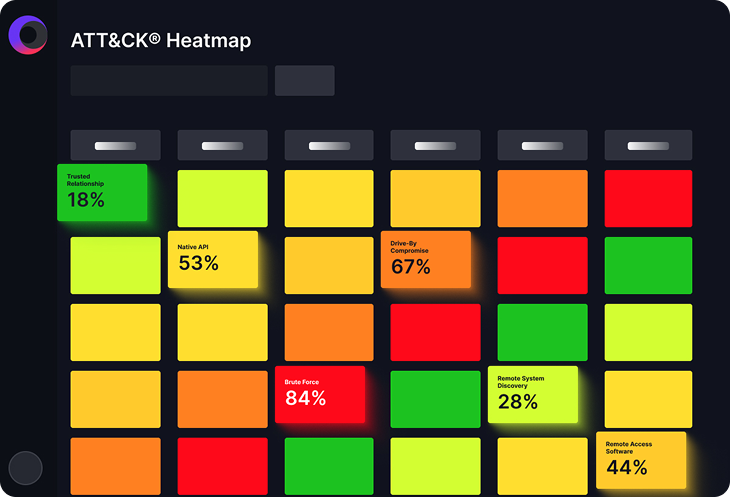
Cymulate runs attacker techniques and full attack chains against your endpoints using the deepest attack library available, tailored to your environment. It then correlates the simulation with your EDR’s logs and alerts to determine whether each technique was detected, blocked, or missed entirely. Findings map directly to MITRE ATT&CK, so you can see coverage gaps by technique rather than a single pass/fail score, and each finding shows the exact detection logic needed to close the gap.
Yes. Cymulate simulations are production-safe: they reproduce the techniques and behavior of real attacks without executing actual malicious payloads or causing damage to systems or data. This is what allows validation to run continuously in live environments rather than being confined to a test lab or a scheduled maintenance window.
Yes, through Cymulate Auto Mitigation. For missed attacker behaviors, Cymulate generates and deploys vendor-specific EDR detection rules directly to your console. For indicators of compromise that surface during validation, you can push them individually, in bulk, or via automated policies. Every pushed rule, or IoC, can be reviewed before deployment, removed or undone from Cymulate and is automatically retested to confirm it improved detection.
Penetration testing is point-in-time and manual: a skilled tester runs a defined engagement, usually annually or quarterly and hands back a report of what they found. Endpoint security validation with Cymulate runs continuously and safely in production, requires no pentester expertise to operate and covers the full breadth of MITRE ATT&CK rather than the subset of techniques a single engagement can reach in its allotted time. It also goes a step further than reporting: when Cymulate finds a gap, it can generate the fix, deploy it to your EDR and retest automatically to prove the gap is closed.