

Web Gateway Validation
Continuously test and optimize your secure web gateway against the latest threats.
Most malware is delivered via the web and email, making secure gateways essential protection.
1 in 100
Web URLs link to malicious sites
Source: Cloudflare
31%
Web traffic originates from bots
Source: Cloudflare
32%
Malware distributed via the web
Source: Expert Insights
Agentic Cyber Defense Engineering for SWG
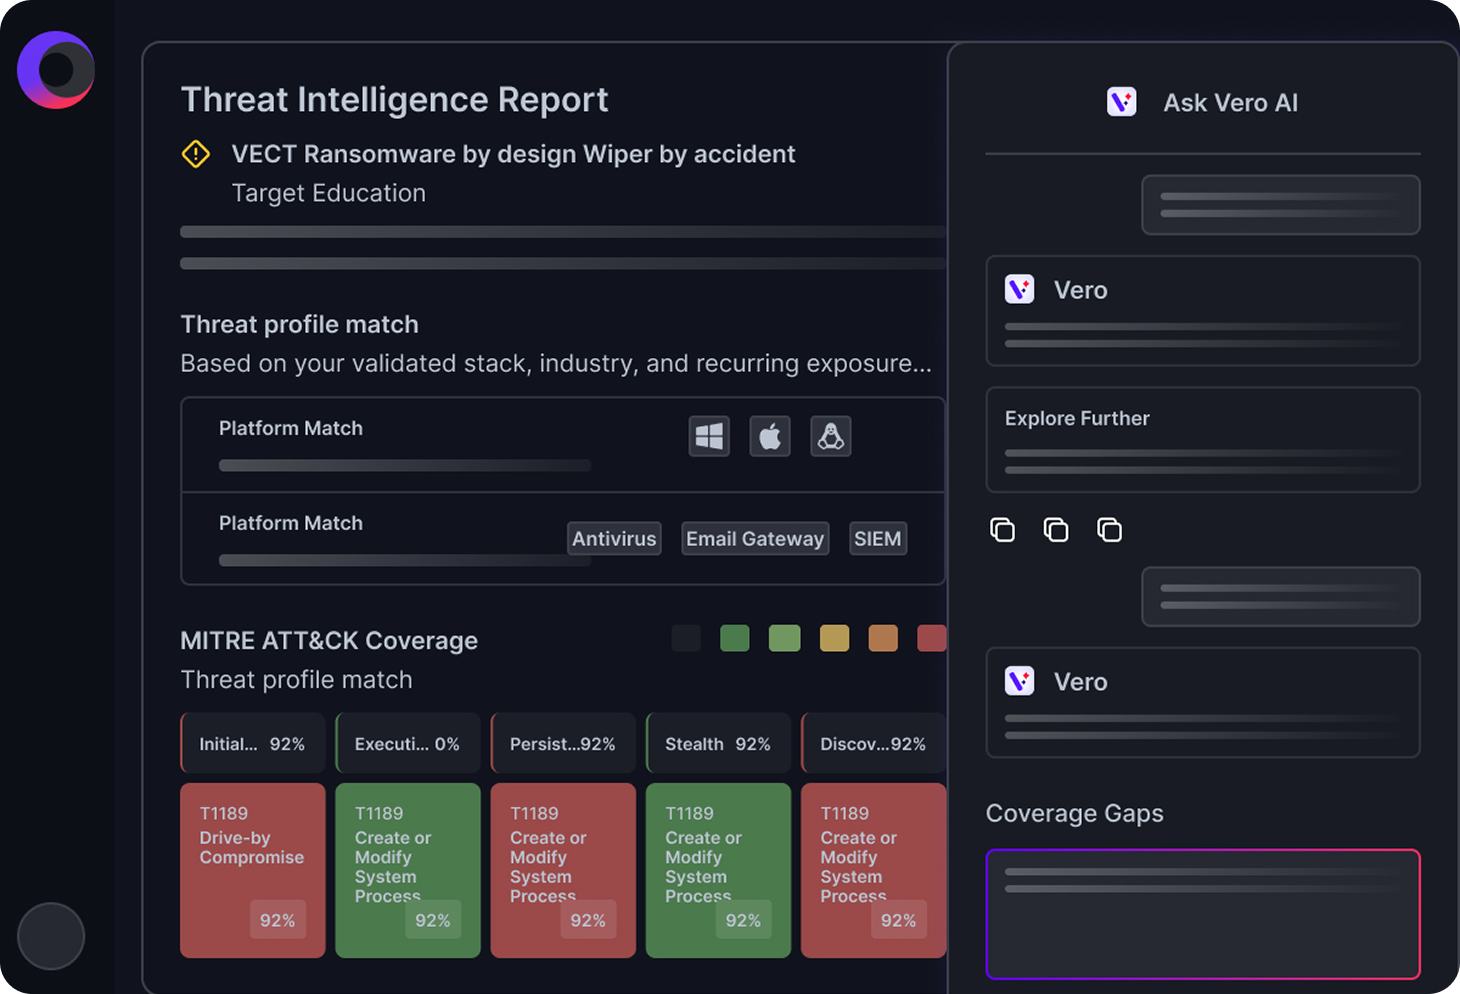
AI-generated phishing, malware and payload evasion now reach users through the browser at machine speed and proving your gateway still stops them demands a new approach. Cymulate integrates with your SWG (secure web gateway) and other security controls to go beyond validation and deliver agentic cyber defense engineering.
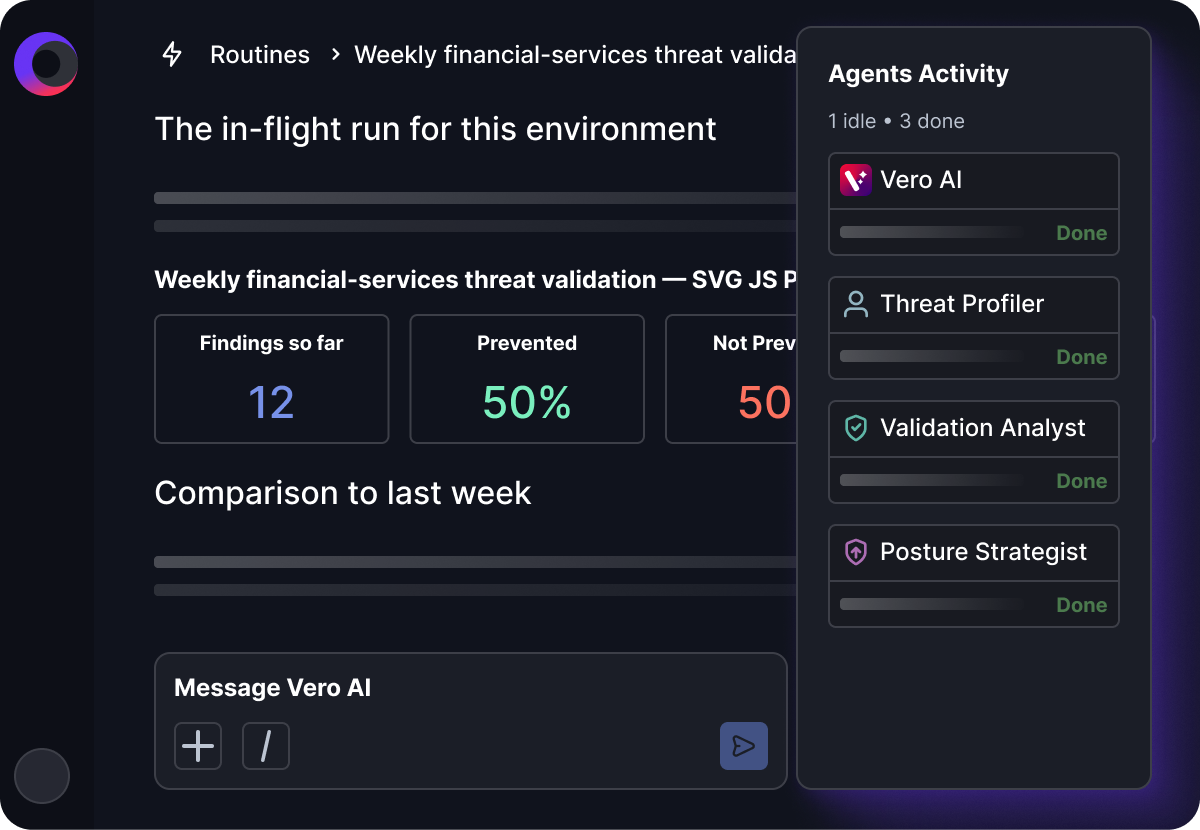
Powered by Vero AI, Cymulate proves web control effectiveness through production-safe attack simulation, prioritizes gaps with real-world impact and adapts your defenses with remediation guidance and streamlined mitigation workflows.
When Cymulate identifies a malicious site or download that reached the endpoint, a misconfigured policy or a gap in URL filtering, it provides guidance so you can close it. Every update is revalidated against the original attack scenario, so stronger web protection is proven, not assumed.
Instead of one more list of findings, Cymulate closes the risk-to-fix gap and continuously proves, prioritizes and adapts your web gateway against the threats targeting your users.
SWG Validation and Optimization
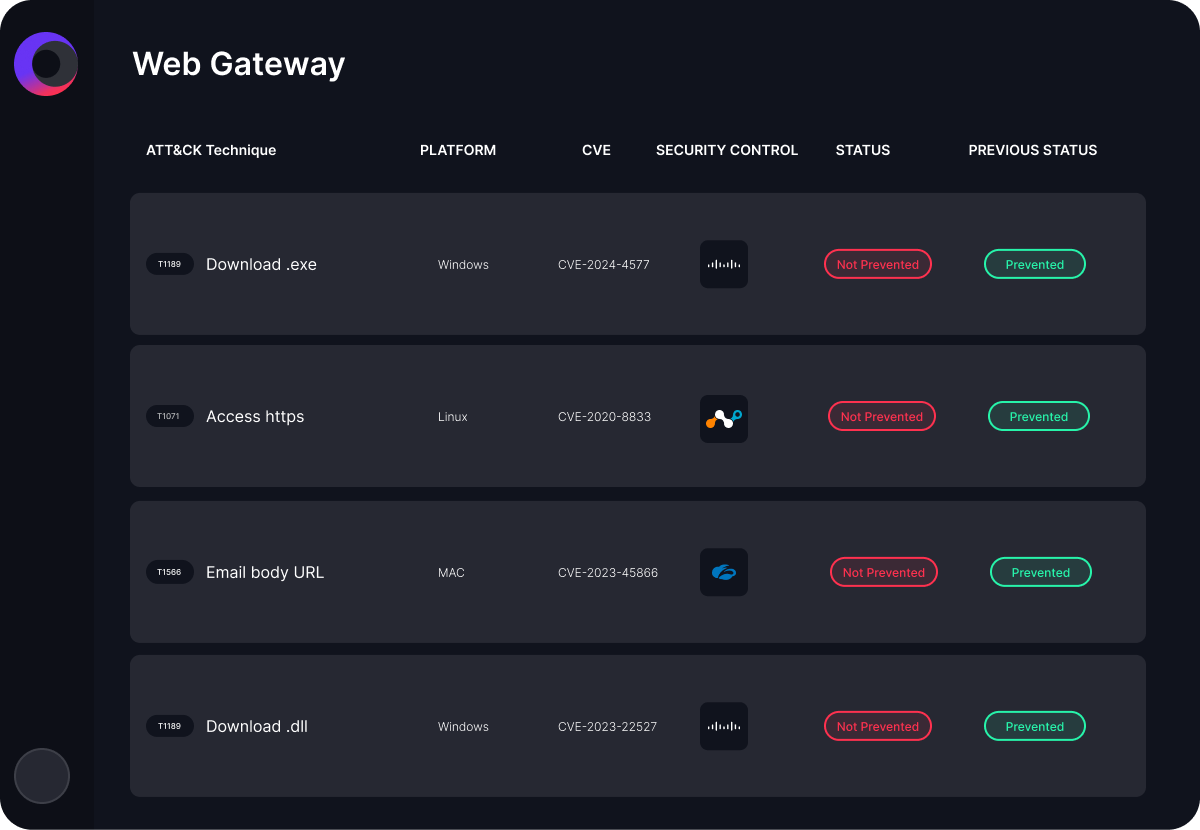
Results & Outcomes

90%
Threat prevention
CYMULATE CUSTOMER AVERAGE

50%
Better threat detection
CYMULATE CUSTOMER AVERAGE
60%
Boost to team efficiency
IT SOLUTIONS CUSTOMER
Solution Benefits
Automated security validation
Identify gaps and weaknesses
Optimize security controls
Reduce exposure risk

Integrate with Your SWG to
Tune and Optimize Web Security
Cymulate connects with your secure web gateway and other security controls to analyze how it handled each simulated web attack, show which malicious URLs, files and exploit payloads reached the endpoint and provide the mitigation guidance to tune gateway controls and policies.
What Our Customers Say
Featured Resources
View More Resources
Bank Increases In-House Security Testing without a Red Team
This Singapore bank needed to improve its security posture without investing in an in-house red team.
Civil Engineering Organization
Read how this organization goes beyond security control validation with the Cymulate platform.
Security Validation Best Practices
Explore the principles and best practices of security validation.
FAQs
Secure web gateway (SWG) validation is the practice of testing your web gateway with real, production-safe web attack scenarios to prove what it actually blocks. Rather than relying on vendor claims or policy configuration reviews, validation sends malicious URLs, drive-by downloads and exploit payloads through the gateway over HTTP and HTTPS and measures which ones were blocked, which were allowed and why — turning assumed web protection into evidence.
Cymulate integrates with your SWG and other security controls and runs production-safe web attack simulations from inside your environment. It attempts to resolve phishing, ransomware and command-and-control (C&C) URLs, download malicious files and exploit proof-of-concepts, and then correlates the results with your gateway telemetry to show exactly which URL categories, policies or filtering rules let content through. Vero AI tailors each assessment to your industry and environment and draws on a daily updated attack library mapped to MITRE ATT&CK.
Web threats and gateway configurations both change constantly. Attackers rotate domains and generate new AI-assisted phishing and payload variants daily, while policy edits, exceptions and product updates quietly erode coverage. Continuous testing surfaces configuration drift and unexpected drops in threat coverage as they happen, so a control that was effective last quarter is proven effective today rather than assumed to be.
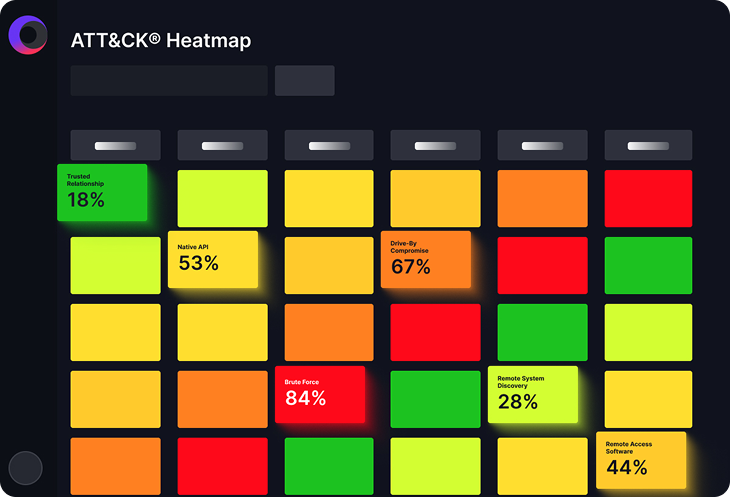
Cymulate tests the full range of web-borne attack techniques: phishing and credential-harvesting sites, malicious and newly registered domains, C&C and exfiltration channels, ransomware and malware downloads, drive-by downloads, exploit proof-of-concepts, risky file types and URL-category and content-filtering policy bypasses — all mapped to MITRE ATT&CK and refreshed daily.
Yes. Cymulate simulations are production-safe: they reproduce the techniques and behavior of real attacks without executing actual malicious payloads or causing damage to systems or data. Web scenarios exercise the gateway’s decision path — URL resolution, category enforcement, inspection and download control — without putting users or endpoints at risk. This is what allows validation to run continuously in live environments rather than being confined to a test lab or a scheduled maintenance window.
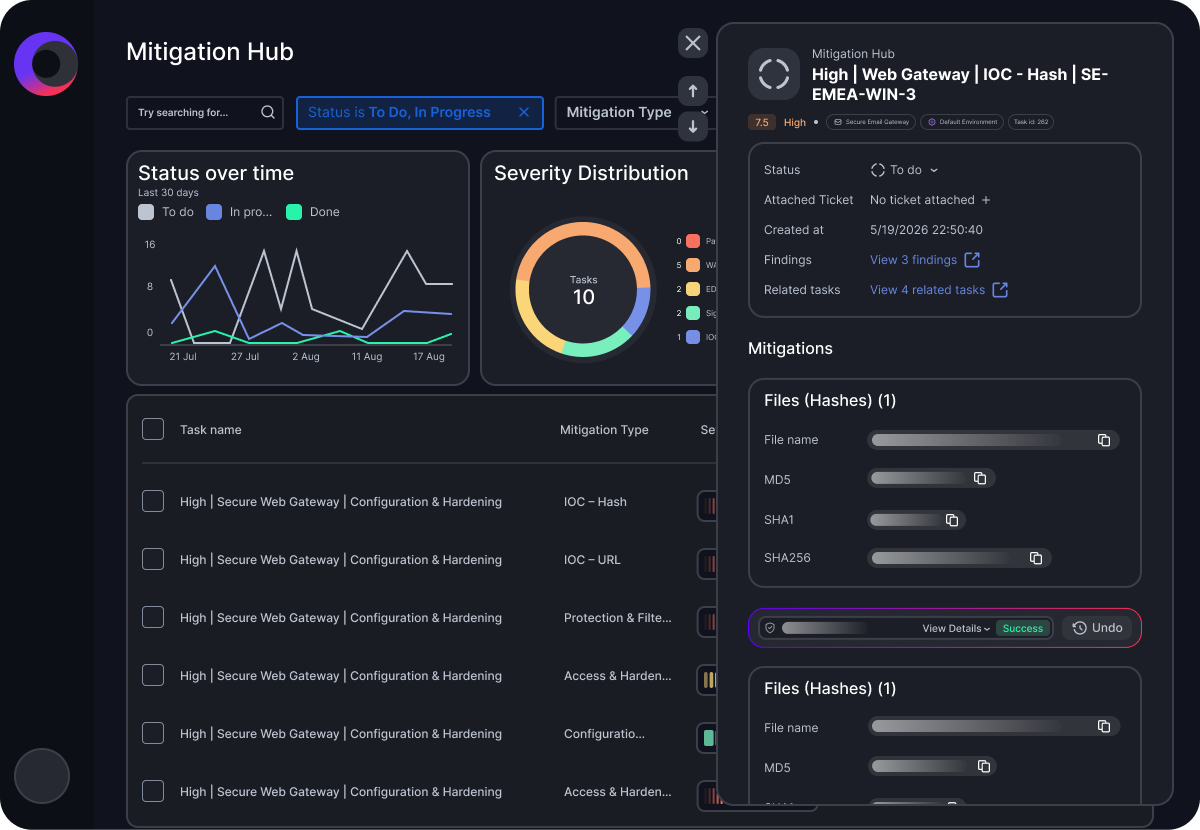
When Cymulate finds a malicious site or download that reached the endpoint, a misconfigured policy or a gap in URL filtering, it provides specific mitigation guidance — recommended indicators of compromise (IoCs) to block, policy and category tuning, and other control updates. With Auto Mitigation, you don’t have to apply those changes by hand: Cymulate pushes the recommended IoCs straight to your integrated controls, so a validated gap can be closed in minutes instead of waiting on a ticket. The mitigation hub mobilizes and tracks that work, and every applied change is revalidated against the original attack scenario, so findings become proven fixes instead of another backlog list.
Re-run the original attack scenario. Cymulate revalidates each change against the same simulation that exposed the gap, so you get direct before-and-after evidence that the policy edit or IoC block worked. Scheduling that scenario for ongoing execution then confirms the fix holds over time and alerts you if coverage regresses.