

Threat Adaptation: Your Future SOC Metric
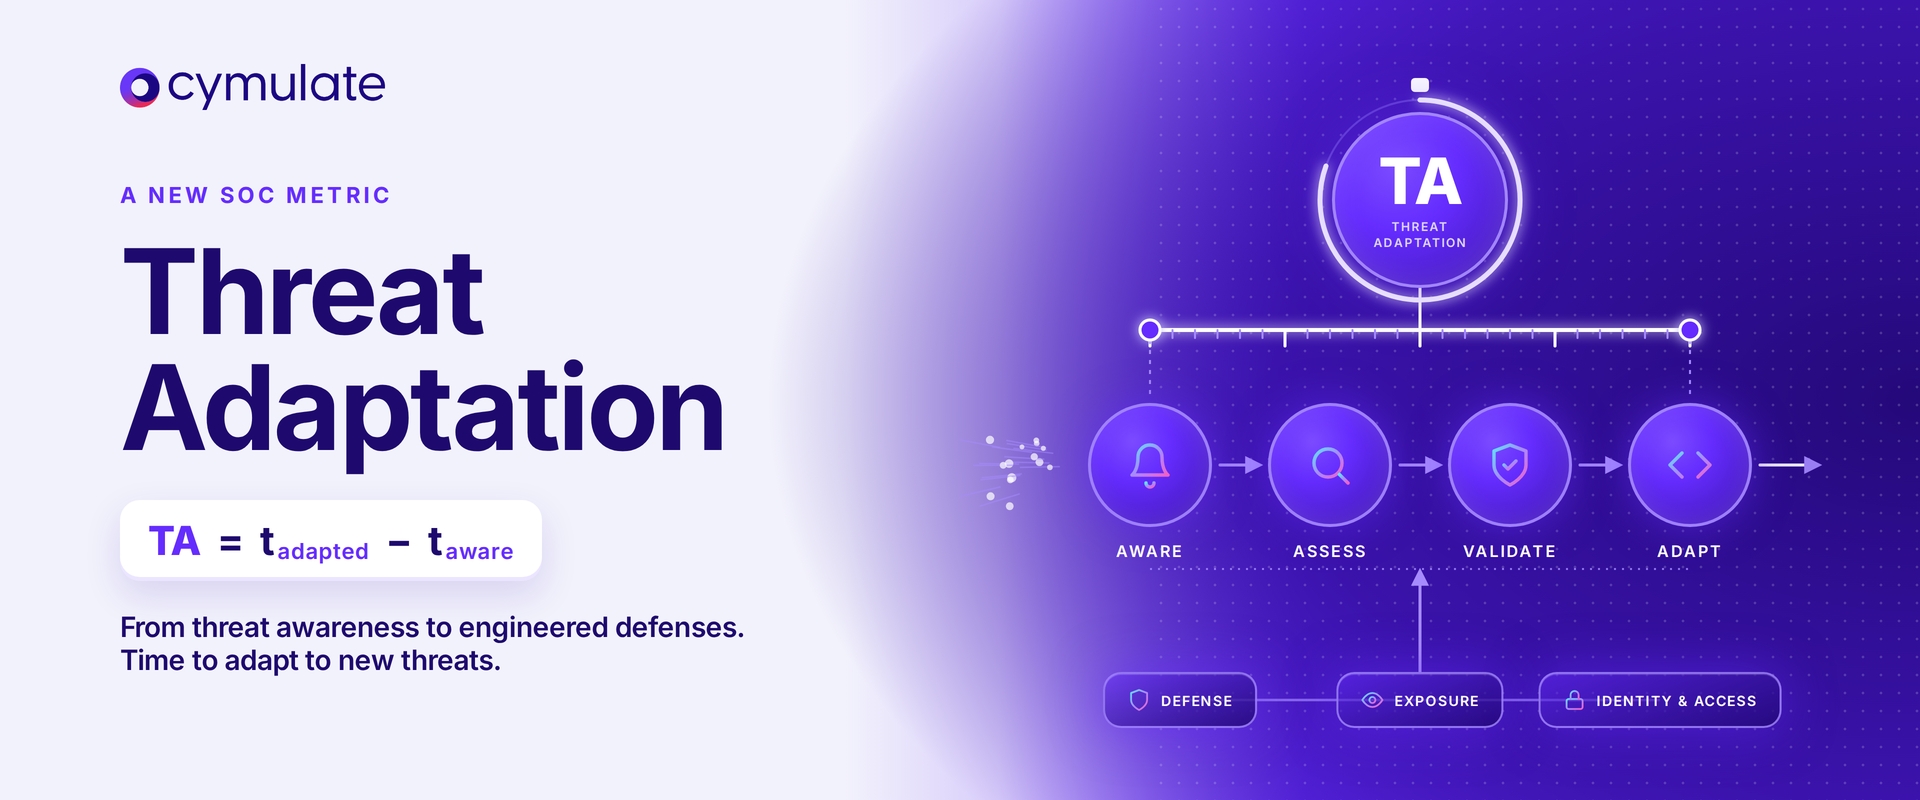
For years your security operations center kept score with two core numbers: mean time to detect and mean time to respond. AI-powered threats require a more proactive and preemptive metric: “threat adaptation.”
A recent Gartner® report introduced threat adaptation as a new metric in its guidance toward building the SOC of the future.
Threat adaptation (TA): The time it takes from when your organization is aware of a new threat until the environment is assessed, validated (including defensive posture) and an automated stopgap adaptation is made (such as implementing new detection code, limiting access, throttling, etc). This measure should be taken at the most advantageous position (such as defensive team, exposure team, or identity and access team) and seen as a unified collaborative response.
Gartner, The Security Operations Roadmap to 2030, Kevin Schmidt, Alex Tytarenko, Steve Santos, Eric Ahlm, Pete Shoard, October 4, 2026
Why Existing Metrics Fail
In my time running product management for managed detection and response, I’ve seen the value of mean time to detect (MTTD) and mean time to respond (MTTR) in measuring SOC performance on its original core duty: reactive security.
But both measure how quickly a team handles an attack once it reaches the environment. Neither tells security leaders how quickly their organization can prepare for a newly discovered threat, test its defenses and close the gaps before an attacker exploits them.
AI increases both the scale and speed of new threats. We’ve seen the evidence and power of frontier AI to:
- Discover new exposures
- Turn vulnerabilities into usable attack techniques
- Breakout from an initial foothold to achieve attack objectives
- Coordinated agents that work in parallel to achieve attack objectives
Faster detection and response alone leave an important question unanswered: How long are we exposed after we learn about a threat?
The Building Blocks of Threat Adaptation
Know your attack surface. Maintain a current view of assets and exposures as your environment changes. When a new threat emerges, this context helps teams identify which systems may be affected and where to focus testing.
Threat awareness. Track active campaigns and emerging attacker techniques to understand which threats are relevant to your organization. Translate that intelligence into specific attack behaviors your teams can test against the environment.
Security controls. Maintain visibility into the configuration and changes of the controls that protect your environment. This gives teams the context to assess existing defenses and identify where prevention or detection may need to be updated.
Validate threats and controls. Use automated attack simulations to prove whether security controls can prevent and detect the attacks associated with each exposure. Test the SOC response as well to establish whether teams can investigate and contain the activity that gets through.
Virtual patch. Apply threat-specific prevention updates to security controls to reduce exposure while a permanent fix is prepared. These stopgap measures can block an attack technique or restrict the access it needs to succeed.
Detection engineering. Build, test and deploy detection logic for relevant attacker behaviors that existing rules miss. Validate that the new logic produces actionable alerts with enough context for the SOC to investigate and respond.
Validate updated defenses. Re-test the environment after prevention and detection changes to confirm they address the demonstrated gaps. Use the results to verify effective mitigation and identify any remaining work.
Adapt at Machine Speed with Agentic Cyber Defense Engineering
Many mature security operations teams already have these building blocks in place. The challenge is to make them work together in an automated and near-autonomous process that adapts security controls to new threats at machine speed.
At Cymulate, we call this agentic cyber defense engineering – a closed-loop system to prove, prioritize and adapt. Agentic cyber defense engineering optimizes your existing security to stay ahead of the threats targeting your environment and shorten your threat adaptation time.
This approach applies AI to execute repeatable and continuous routines that test threats, validate exposures, push control updates for immediate prevention and build new detection logic – all to engineer defenses that adapt to current threats.
With a 10-year history of advanced offensive security, the Cymulate platform delivers agentic cyber defense engineering that:
- Profiles relevant attacker behavior
- Tailors testing to your environment, assets, industry, exposures and controls
- Executes safe, realistic attack simulations
- Validates prevention and detection of existing security controls
- Prioritizes fixes by real-world impact
- Optimizes security controls with prevention and detection updates that mitigate exposures and threats
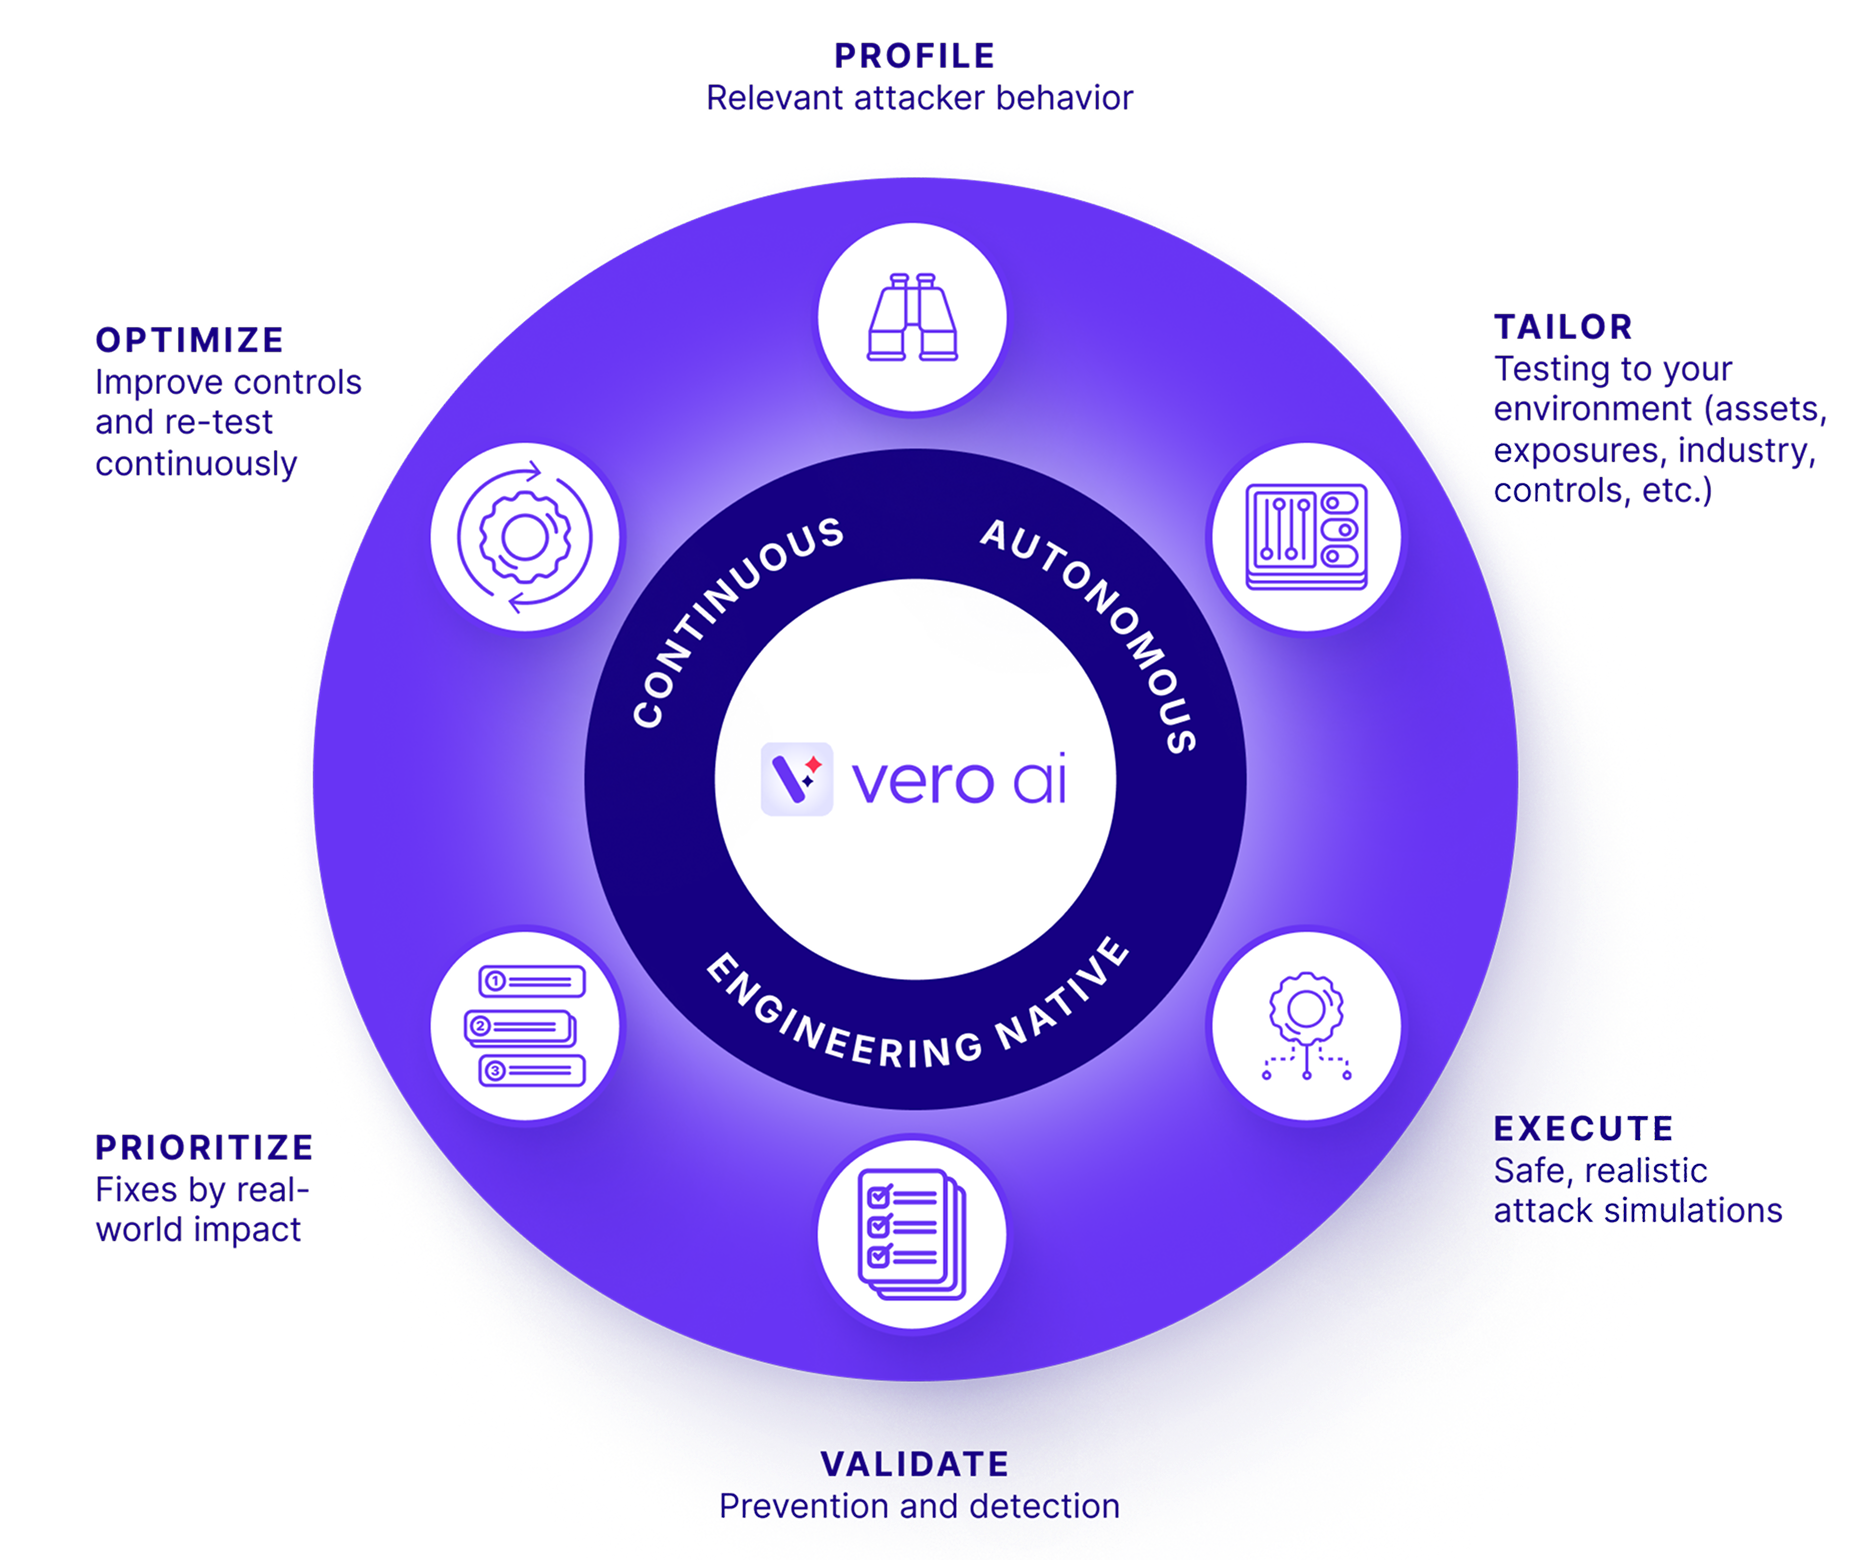
Agentic Cyber Defense Engineering at a Glance
| Requirement | Required Inputs | Expected Outcome |
| 1. Profile — Integrate and maintain a living contextual model | Asset discovery, exposure management, threat intelligence, security control and telemetry feeds | A continuously current model of assets, exposures, architecture, controls and relevant attacker behavior that automatically advances the closed loop |
| 2. Tailor — Configure organization-specific assessments | Maintain current environment/threat profile and configure test points, environments and tool integrations | An attack assessment scoped and configured to the organization's specific environment, without manual setup |
| 3. Execute — Safely run realistic attacks | Tailored attack scenarios, defined scope and safety boundaries, approval and escalation policies | Controlled, repeatable execution of realistic attacks with no disruption to business operations |
| 4. Validate — Measure prevention and detection | Attack execution results with integrated security control and telemetry data | Measurable evidence of what was prevented, detected or missed |
| 5. Prioritize — Analyze gaps by demonstrated risk | True risk scores by correlating validation evidence, threat intelligence, exploitability, attack-path reachability and business impact data | A stacked ranked list of exposures based on demonstrated impact rather than static severity scores |
| 6. Optimize — Configure controls and improve security | Mitigate priority exposures with vendor specific prevention and detection improvements | Auto-deployed, governed mitigations with automatic re-validation to ensure the mitigation was successful |
Learn More about How Cymulate Drives Threat Adaptation
To plan a future SOC built for threat adaptation, read the Cymulate e-book Agentic Cyber Defense Engineering.
Featured Resources
View More Resources
From AI Hype to AI Risk: A New Security Reality
Cymulate CTO Avihai Ben-Yossef explains AI-driven attacks and how continuous validation helps defenders prioritize.
Inside the Agentic Cyber Defense Engineering Architecture: How it Works
Understand the environment, coordinate specialized security work and act across the security stack.
Cymulate for Security Operations
Validate threats and understand gaps to build stronger defenses that protect your biggest sources of threat exposure.