Frequently Asked Questions

Agentic Cyber Defense Engineering & SecOps

What is agentic cyber defense engineering and how does Cymulate implement it?

Agentic cyber defense engineering is Cymulate's AI-driven, autonomous approach to continuously proving, prioritizing, and adapting cybersecurity. It profiles attacker behavior, tailors testing to your environment, executes safe attack simulations, validates prevention and detection, prioritizes fixes, and optimizes controls. Cymulate's platform features Vero AI for automated insights and actions, and the Mitigation Hub for prioritized, automated mitigation tasks. Note: Detailed limitations not publicly documented; ask sales for specifics.

How does agentic cyber defense engineering streamline SecOps workflows?

Agentic cyber defense engineering automates key SecOps routines: validating new threats and verifying mitigation, turning exposures into informed defensive action, and continuously engineering detection coverage. Specialized agents gather context, run production-safe validation, correlate results, and drive action until outcomes are verified. This reduces manual effort and enables continuous improvement. Note: Best fit for teams seeking automation; organizations with highly custom workflows may require additional integration.

What operational routines does Cymulate support for SecOps teams?

Cymulate supports routines such as: 1) Threat validation ending with proven mitigation, 2) Exposure assessment leading to exposure-informed defenses, and 3) Continuous detection engineering. Agents monitor threat feeds, validate defenses, deploy fixes, and verify mitigation. They also assess exposures, correlate results, and prioritize mitigation, and continuously test detection rules for coverage gaps. Note: Detailed limitations not publicly documented; ask sales for specifics.

Features & Capabilities

What are the key features and benefits of Cymulate's platform?

Cymulate offers continuous threat validation, broad and deep threat coverage, AI-powered environment mapping, automated security control validation, attack surface management, and integration with over 50+ security tools. Benefits include an average 52% reduction in critical exposures, 30% increase in threat prevention, 3X increase in threat detection, 60% increase in team efficiency, and 40X faster threat validation. Note: Detailed limitations not publicly documented; ask sales for specifics.

What integrations does Cymulate support?

Cymulate supports over 50 integrations, including SIEM (CrowdStrike Falcon LogScale, CrowdStrike Falcon Next Gen SIEM), EDR and anti-malware (BlackBerry Cylance OPTICS, Carbon Black EDR, CrowdStrike Falcon), cloud security (AWS GuardDuty, Check Point CloudGuard), web gateway (Cisco Umbrella), network security (Akamai Guardicore), vulnerability management (Rapid7 InsightVM), threat intelligence platforms, SOAR, and ticketing systems (Slack, Microsoft Teams). Note: Some integrations may require additional configuration; check the technology alliances page for specifics.

Use Cases & Business Impact

What business impact can customers expect from using Cymulate?

Customers report an average 52% reduction in critical exposures, 30% increase in threat prevention, 3X increase in threat detection, 60% increase in team efficiency, and 40X faster threat validation. Hertz Israel achieved an 81% reduction in cyber risk within four months. Note: Results may vary based on environment and implementation; detailed limitations not publicly documented.

What core problems does Cymulate solve for security teams?

Cymulate addresses the risk-to-fix gap, uncertainty about real-world readiness, slow manual validation cycles, too many findings with insufficient prioritization, siloed tools and teams, lack of actionable remediation, security drift and detection decay, and difficulty proving improvement to leadership. Note: Best fit for organizations seeking continuous validation; teams with highly custom requirements may need additional support.

Who is the target audience for Cymulate?

Cymulate is designed for CISOs, VP Security, SecOps leaders, SOC managers, detection engineers, blue team leads, red teams, vulnerability management teams, GRC/compliance, and IT/infrastructure/cloud stakeholders. It is suitable for organizations across finance, healthcare, engineering, retail, and more. Note: Not all features may be relevant for every persona; consult sales for tailored recommendations.

Are there case studies demonstrating Cymulate's impact?

Yes. Hertz Israel reduced cyber risk by 81% in four months. LV= used Cymulate for near real-time data to validate strategic decisions. Banco PAN optimized security controls and prioritized vulnerabilities. Saffron Building Society received actionable remediation guidance for compliance. Nemours improved detection and response. UK Bank provided measurable evidence of improved resilience to leadership. Note: Case studies reflect specific environments; results may vary.

Ease of Use & Implementation

How long does it take to implement Cymulate and how easy is it to start?

Cymulate can be deployed within hours or days, depending on requirements. It operates in agentless mode, requiring no additional hardware or complex configurations. The user-friendly interface allows simulations with a few clicks. Support resources include email, chat, webinars, e-books, and a knowledge base. Raphael Ferreira, Cybersecurity Manager at Banco PAN, stated, "Cymulate is easy to implement and use—all you need to do is click a few buttons, and you receive a lot of practical insights into how you can improve your security posture." Note: Implementation time may vary based on environment complexity.

What feedback have customers provided about Cymulate's ease of use?

Customers consistently praise Cymulate for its intuitive interface, ease of deployment, and actionable insights. Testimonials include: "Easy to implement and use" (Raphael Ferreira, Banco PAN), "Easy to use and understand" (Security Consultant), "User-friendly and easy to deploy" (IT Security & Risk Management Assistant), "Shows internal stakeholders why cybersecurity is important" (Markus Flatscher, Senior Security Manager), and "Easy to navigate and configure, effective mitigation steps, first-class support" (Head of Information Security Operations). Note: User experience may vary based on organizational needs.

Security & Compliance

What security and compliance certifications does Cymulate hold?

Cymulate is SOC2 Type II certified, covering security, availability, confidentiality, and privacy. It holds ISO 27001:2013 (ISMS), ISO 27701 (PIMS), ISO 27017 (cloud security), and CSA STAR Level 1 certifications. Data is encrypted in transit and at rest, hosted in AWS data centers certified for ISO 27001:2022, PCI DSS Service Provider Level 1, and SOC 2/3 Type II. Annual secure code training, vulnerability scanning, and third-party penetration testing are conducted. Note: Compliance requirements may vary by region; consult sales for specifics.

How does Cymulate ensure product security?

Cymulate enforces 2-factor authentication (2FA) for all employees, offers SSO options, and uses role-based access controls (RBAC) for granular data access. GDPR compliance is achieved through secure development life cycle procedures, data protection by design, and oversight by a Data Protection Officer. Note: Security policies may be updated; check the security overview page for the latest details.

Technical Documentation & Resources

Where can I find technical documentation and data sheets for Cymulate?

Technical documentation and data sheets are available in Cymulate's Resource Hub at https://cymulate.com/resources/. Detailed information on Threat Studio can be found at https://cymulate.com/data-sheet/threat-studio/. Note: Documentation may be updated; check the resource hub for the latest materials.

Blog & Research Content

Where can I access Cymulate's latest blog posts and research?

The latest blog posts, including topics on agentic cyber defense engineering, red and purple teaming, threat research, and exposure management, are available at https://cymulate.com/blog/. Note: Blog content is updated regularly; check for new posts.

Cymulate named a Customers' Choice in 2026 Gartner® Peer Insights™
Learn More
New: Cymulate Cowork for Agentic Cyber Defense Engineering
Learn More
New Bitsight Integration: Turn Threat Intelligence into Validated Security
Learn More
Introducing Cymulate Vero AI for Agentic Cyber Defense Engineering
Learn More

Operationalizing Agentic Cyber Defense Engineering for SecOps 
By: Amanda Kegley

Last Updated: October 14, 2026

Security operations teams spend too much of each day gathering context, configuring assessments, correlating evidence and coordinating follow-up actions across disconnected tools and processes. 

Agentic cyber defense engineering is designed to streamline this work by coordinating specialized agents through continuous, governed routines. Previous blogs in this series defined the architecture and requirements behind the operating model. This blog shows how that model applies to three recurring SecOps workflows: validating new threats and verifying mitigation, turning exposures into informed defensive action and continuously engineering detection coverage. 

Key takeaways 

  • Threat validation should end with proven mitigation. Agents can determine whether a threat is relevant, validate defenses, deploy fixes and trigger revalidation to verify successful mitigation. 
  • Exposure data becomes more valuable when it informs defense. Validated exploitability, attack paths and control performance help SecOps teams prioritize their actual risk and improve threat resilience. 
  • Detection engineering can become continuous. Agents can build coverage for new threats and exposures, test rules against realistic behavior and identify drift before an attacker exploits it. 

Common Operational Use Cases and Routines 

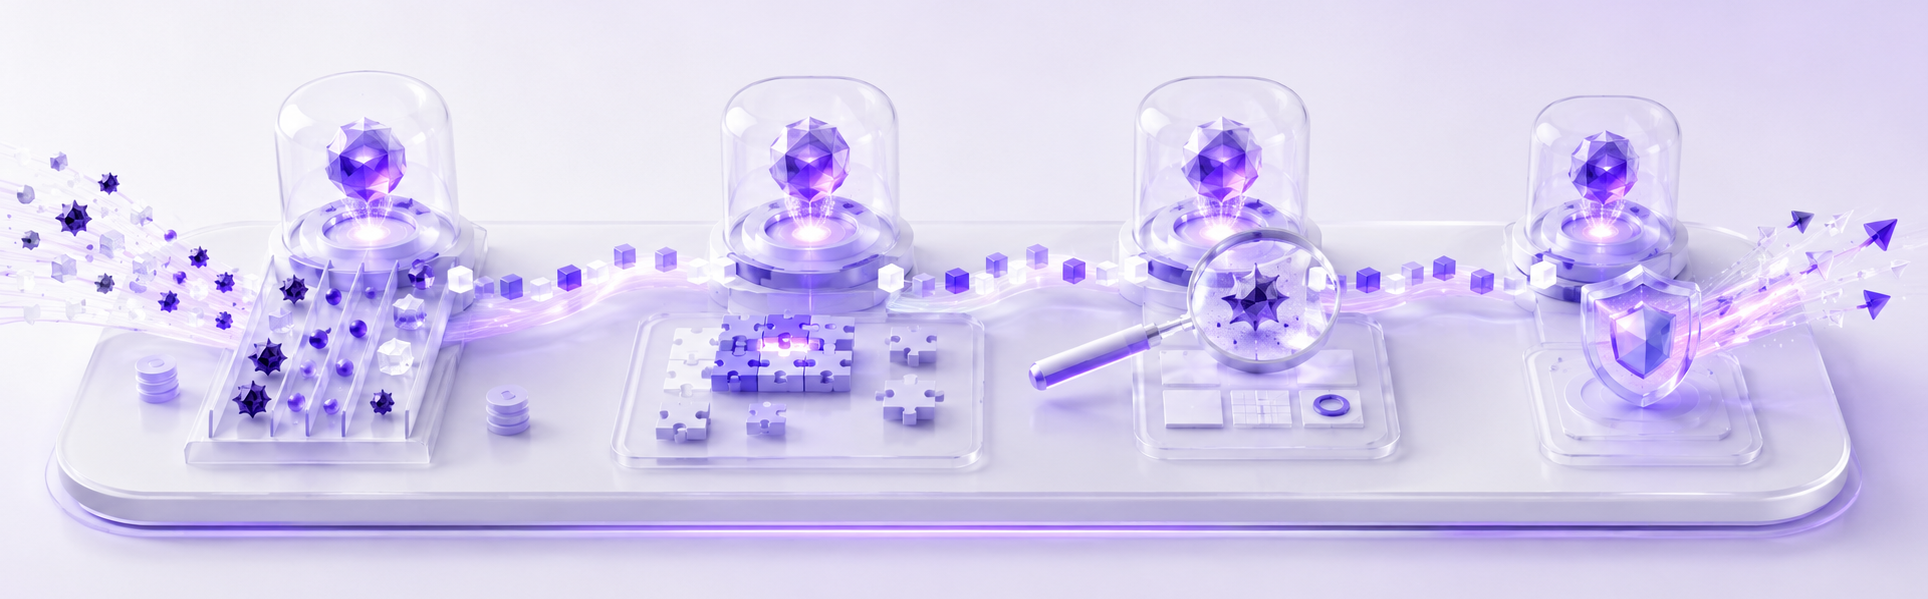
Agentic cyber defense engineering supports a wide range of SecOps activities with repeatable, continuous routines. In most cases, these start with a common trigger – a new threat, a new exposure or a coverage gap – then coordinates the steps teams usually do by hand: gather the right context, run production-safe validation, correlate results across controls and drive the next action until the outcome is verified. 

Routine: From new threat to verified mitigation 

SecOps teams must continually monitor threat intelligence, determine which threats are relevant and validate whether existing defenses are preventing and detecting, as intended. Manually reviewing new campaigns, finding applicable attack scenarios and configuring assessments can delay answers while threats continue to evolve. 

Agentic cyber defense engineering automates this workflow through a recurring threat-validation routine. Agents monitor selected CERTs, commercial threat feeds and internal intelligence sources for new campaigns, malware and attacker techniques. They deduplicate new items and compare them with the organization’s assets, technologies and threat profile to determine relevance. 

For relevant threats, specialized agents select applicable attack scenarios or draft new ones when validation content does not exist. Then, they configure and safely execute the assessment, correlate the attack activity with prevention and detection controls and identify which behaviors were blocked, detected or missed. When fixes for security gaps are implemented, agents then verify successful mitigation. 

As threat intelligence or the organization’s environment changes, agents continually monitor and report changes in defensive performance, allowing SecOps to track resilience against the threat over time. 

Routine: From exposure to exposure-informed defenses 

When a new CVE or exposure is identified, SecOps teams must quickly determine whether affected technology is present, whether the vulnerability is exploitable in their environment, whether existing controls provide protection and what action is required. Answering those questions often requires analysts to search multiple tools, locate or build a test, configure the assessment and interpret the results. 

With agentic cyber defense engineering, an analyst can initiate the process with plain text, such as: “Assess whether our environment is exposed to CVE-XXXX-XXXX.” The system can translate that request into a governed validation routine rather than requiring the analyst to design and coordinate every step manually. 

Specialized agents can identify potentially affected assets, gather relevant threat and vulnerability context, select an existing attack scenario or draft one for review, and execute the assessment within defined safety policies. The routine can then correlate the results with prevention and detection controls, calculate actual risk scores based on demonstrated exploitability and prioritize for mitigation. 

Routine: Continuous detection engineering 

SecOps teams struggle to keep pace with evolving threats and verify that their security controls are detecting all relevant attacker activity. Manually creating, tuning and testing detection rules takes significant time, while changes to rules, parsers, telemetry or data sources can cause previously effective detections to fail without warning. 

Agentic cyber defense engineering can coordinate detection validation, assessment analysis and repeatable detection engineering work. Agents can ingest existing detection rules, execute realistic attacks, correlate that activity with SIEM and EDR telemetry and determine whether the expected alerts and detections were generated. 

When coverage is missing, agents can deploy new tailored detection rules to security tools. Agents monitor to determine when an existing rule stops firing. Then, agents run a routine to identify the gap and mitigate. 

What Changes for SecOps 

Across all three use cases, agents collect context, configure assessments, correlate evidence and coordinate follow-up actions. Routines make the work repeatable, while two-way integrations connect threat feeds, validation, controls, telemetry and ticketing systems. 

SecOps teams still define policies, scope, approvals and risk thresholds. Analysts investigate ambiguity and make business-risk decisions, while agents advance high-volume, repeatable work within those guardrails. 

Security leaders should measure success by the defensive learning cycle, not by the number of AI features or automated tasks. For example, determine how quickly a team can move from a relevant threat or exposure to validated evidence to verified mitigation? 

Ready to Put Agentic Cyber Defense Engineering to Work? 

Operationalizing agentic cyber defense engineering means continuously and autonomously connecting intelligence, exposures, validation and security controls into use cases that produce measurable improvement. For SecOps teams, the result is not simply more automation. It is a continuous, evidence-driven way to improve defense while reducing the manual effort required to coordinate every step. 

To explore the complete operating model, download the Agentic Cyber Defense Engineering e-book. To see how Cymulate can operationalize these use cases across your security program, schedule a demo.
Cymulate Exposure Validation makes advanced security testing fast and easy. When it comes to building custom attack chains, it's all right in front of you in one place.
Mike Humbert, Cybersecurity Engineer
DARLING INGREDIENTS INC.
Learn More
GET A PERSONALIZED DEMO

Ready to see Cymulate in action?