

Cloud Security Validation
Validate and optimize your cloud security controls across AWS, Azure and Google Cloud with continuous attack simulation that builds resilience against cloud-based attacks.
Threat actors target dynamic cloud environments to exploit security weaknesses and misconfigurations.
75%
Increase in
cloud intrusion incidents
Source: crowdstrike
60%
Cloud containers
lack proper protection
Source: crowdstrike
82%
Data breaches
involving cloud platforms
Source: IBM
Agentic Cyber Defense Engineering for Cloud Security
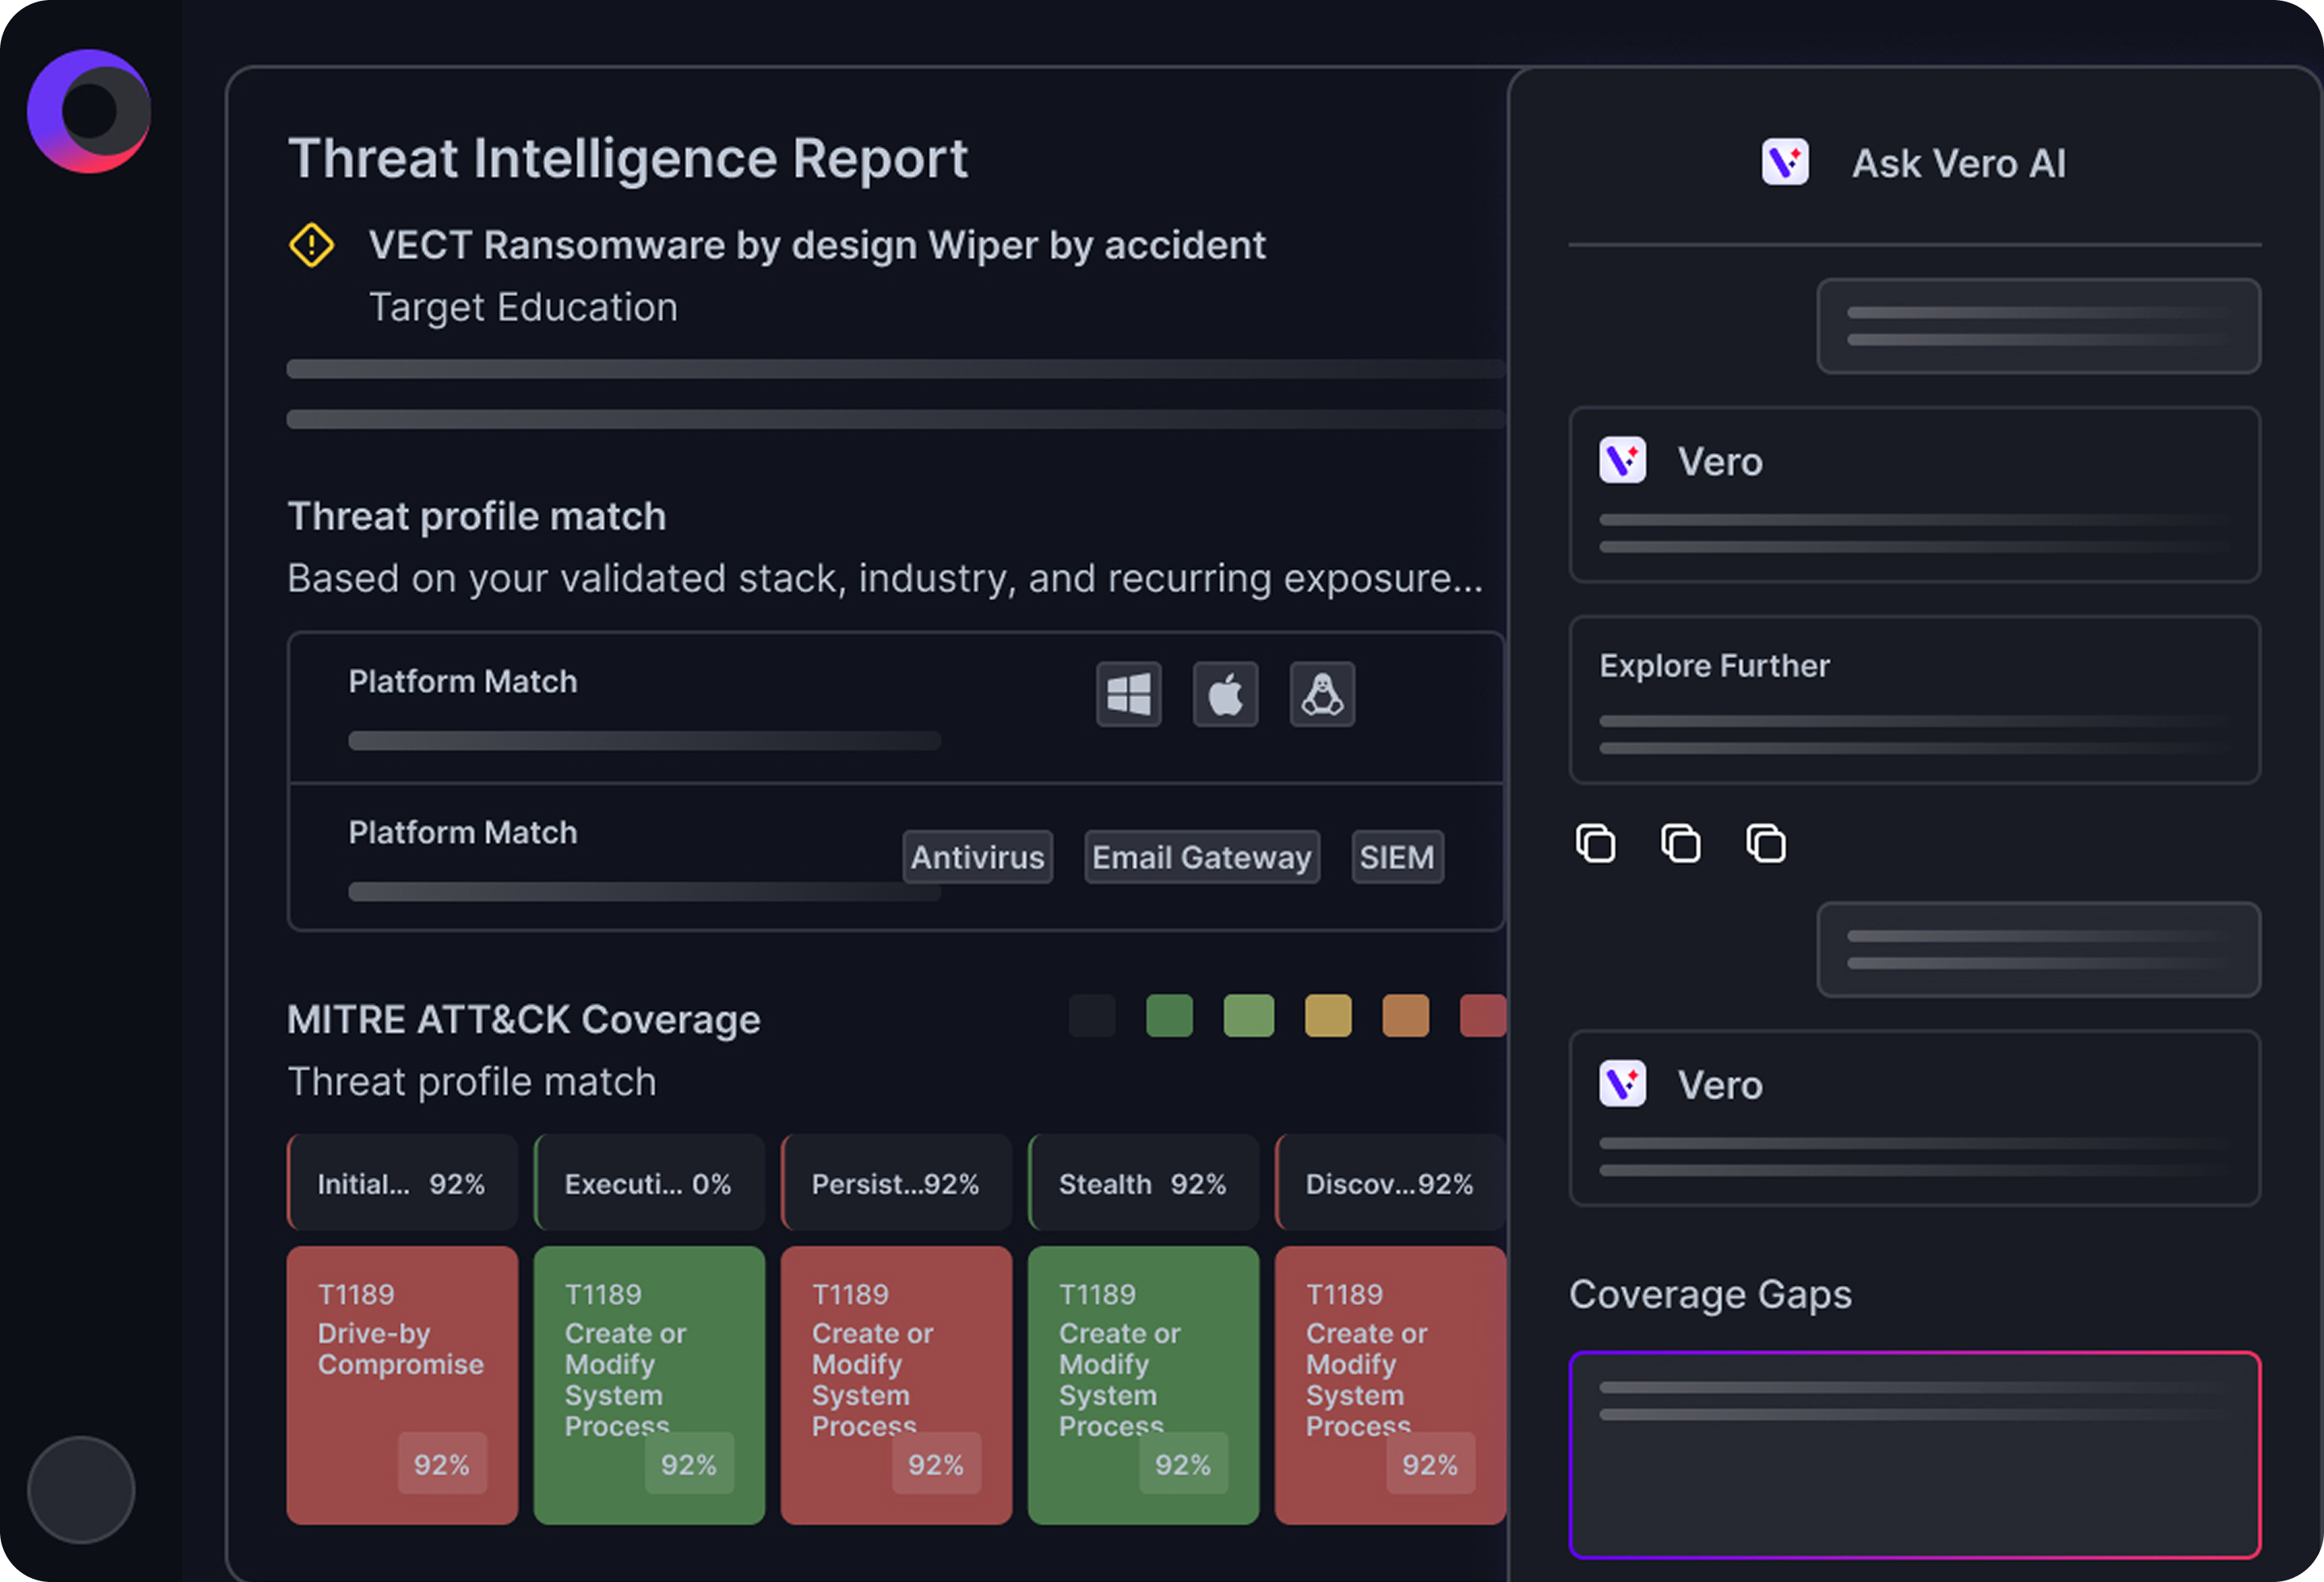
Today’s AI-powered threats demand a new approach to prove, prioritize and adapt your cybersecurity at machine speed. Cymulate integrates with your EDR (endpoint detection and response) to go beyond validation and deliver agentic cyber defense engineering.
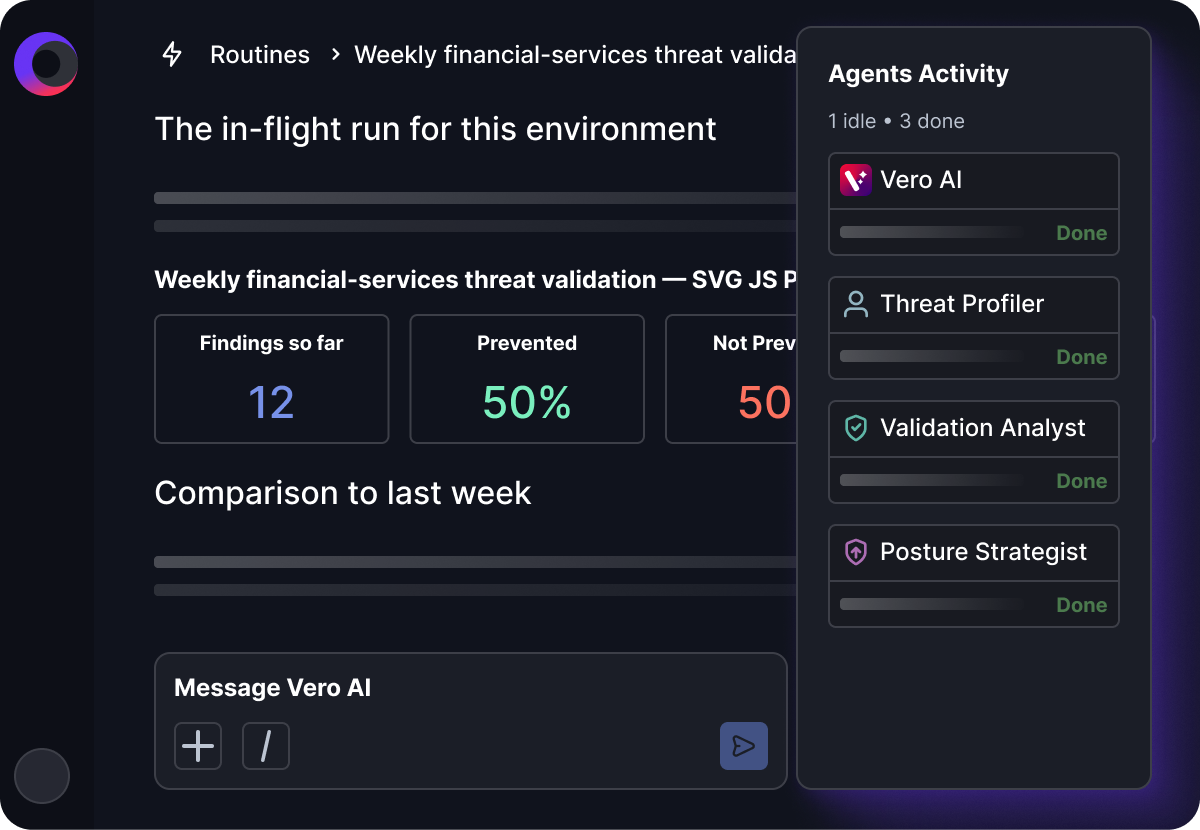
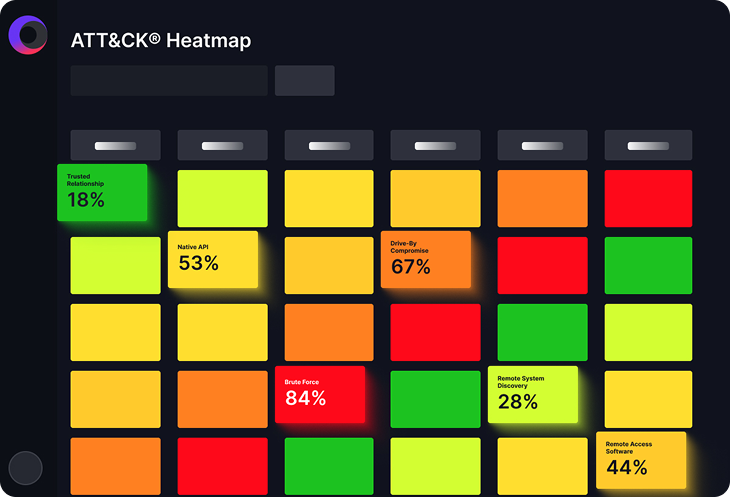
Powered by Vero AI, Cymulate proves cloud control effectiveness through production-safe simulation of high-privileged cloud activity, prioritizes gaps with real-world impact and adapts your defenses with vendor-specific detection logic and mitigation guidance.
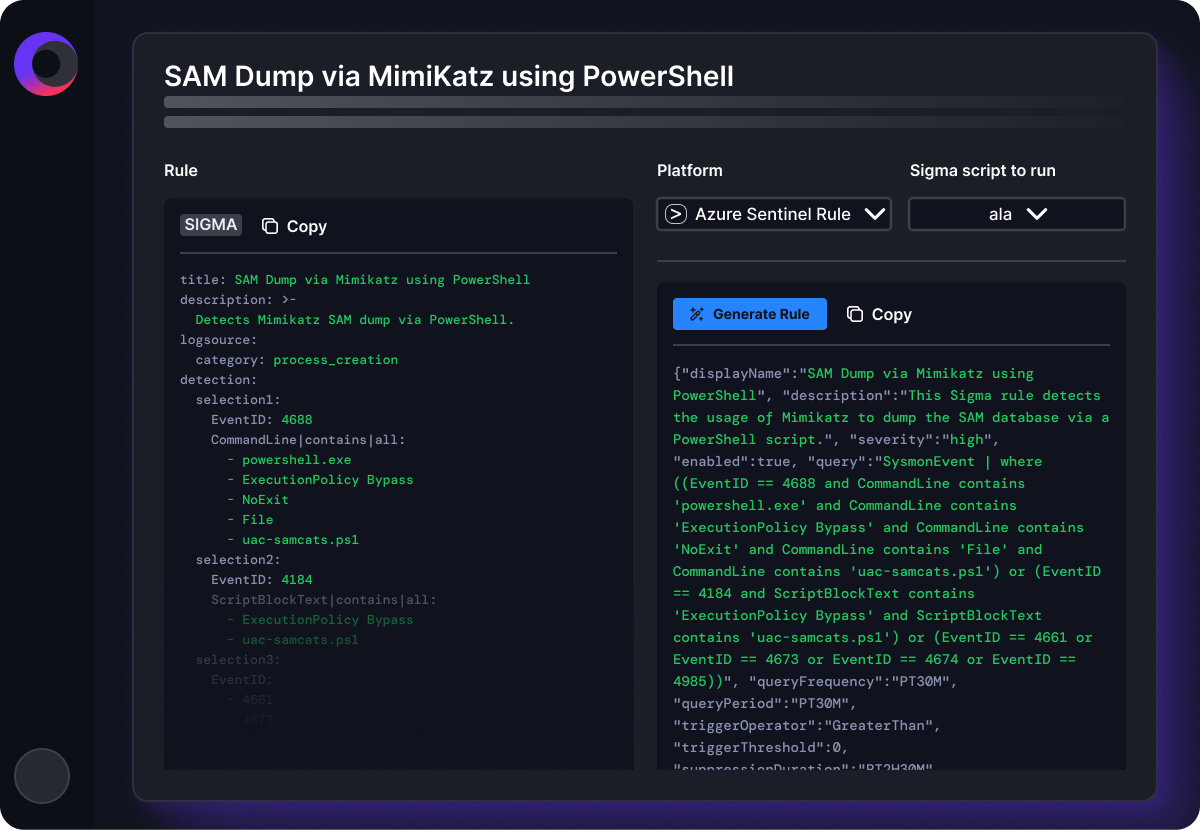
When Cymulate identifies a missed detection, a misconfigured control or a gap in cloud protection, it closes the loop by generating targeted detection logic and vendor-specific mitigation guidance for your SIEM and cloud-native controls. Every update is revalidated by rerunning the original attack scenario, so stronger cloud protection security is proven, not assumed.
Instead of one more list of findings, Cymulate closes the risk-to-fix gap and continuously proves, prioritizes and adapts your cloud defenses against the threats targeting your environment.
Cloud Security Validation and Optimization
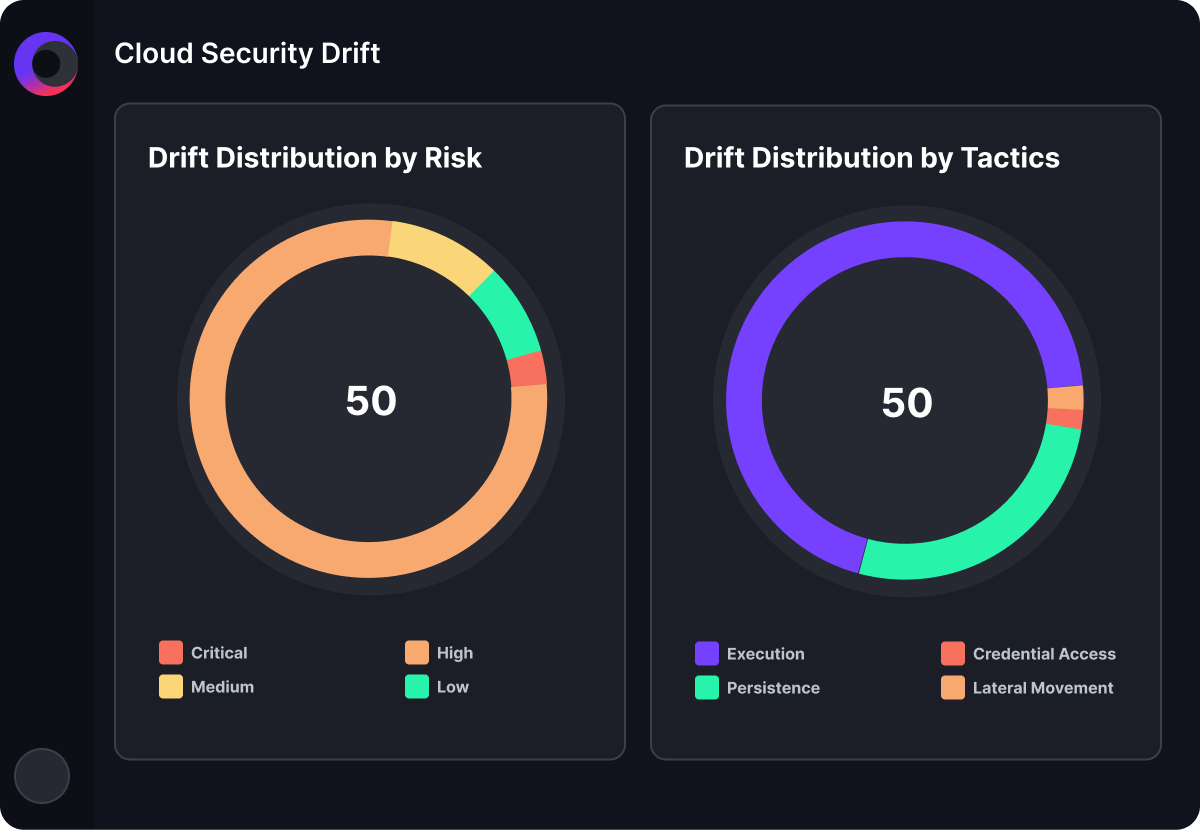
Solution Results

60%
Increase in team efficiency.
finance company
81%
Improvement in security risk score.
Global Transportation
168
Exploits prevented from a single policy change.
healthcare organization
Test and Prove Threat Resilience
in Leading Cloud Environments
Cymulate empowers security teams to safely test the latest cloud threats and close security gaps with actionable remediation to improve resilience.
 |  |  | |
| Virtual Servers | Elastic Cloud Computer | Virtual Machines | Google Compute Engine |
| Storage | Simple, Elastic Blob and Elastic Block Storage | Azure Blog, Files and Disk | Cloud Storage, Filestore and Persistent Disk |
| Database | DynamoDB | CosmoDB | Firestore |
| Identity | IAM | Azure AD | Cloud IAM |
| Key Management | KMS | Key Vault | KMS |
| Virtual Network | VPC | Azure VNet | VPN |
| Network Security | AWS WAF | Application Gateway | Cloud Armor |
| Log Analysis and Alerting | GuardDuty | Sentinel | Security Command Center |

Continuous Wiz Validation
and Optimization
Connect Cymulate with Wiz to validate and optimize threat detection for cloud and runtime attacks.
Cloud Security Validation Benefits
Validate cloud security
Identify cloud security gaps
Optimize cloud security controls
Reduce cloud exposure risk
What Our Customers Say About Us
Featured Resources
View More Resources
Defending Your Kubernetes Environment
Threat research uncovers low detection rates for native cloud security controls.
How to Perform a Cloud Risk Assessment: A Comprehensive Guide
A breakdown of cloud risk assessment practices for identifying and prioritizing cloud security risks.
Cloud Security Validation Best Practices
Discover the key practices for continuous cloud security validation and why it is essential.
FAQs
Cloud security validation is the practice of safely simulating real attacker activity in your cloud environment to prove which behaviors your security controls prevent, detect and alert on. Instead of inferring protection from configuration state, you measure prevention and detection coverage with evidence and use the findings to tune your controls.
Cymulate runs production-safe assessments built from AWS, Azure and Google Cloud templates that execute the high-privileged activities an attacker performs after gaining access — escalating user accounts, modifying security policies and reaching protected storage. Cymulate then correlates the results with your SIEM and cloud-native controls to show what was prevented, what was detected and what went unnoticed.
Cymulate supports AWS, Microsoft Azure and Google Cloud. Dedicated template groups cover each platform, alongside threat-behavior templates that replay known cloud attack campaigns from advanced persistent threat (APT) groups and named threat actors.
Cymulate validates cloud-native controls such as Microsoft Defender for Cloud, AWS GuardDuty and Google Cloud Security Command Center, cloud detection and response tools including Wiz Defend and the SIEM rules that correlate your cloud logs.
Yes. Cymulate cloud assessments are production-safe. They simulate attacker behavior without harming your cloud platforms or workloads, and they remove simulation artifacts when the run completes.
Cloud security posture management (CSPM) and cloud-native application protection platforms (CNAPP) tell you how your cloud is configured. Cloud security validation tells you what happens when an attacker acts on that configuration. Cymulate proves whether your controls stop and detect the activity, then delivers the detection logic and mitigation guidance to close each gap.
Continuously. Cloud environments change daily, so Cymulate supports one-time runs and daily, weekly or monthly schedules. Recurring assessments measure drift over time and let you rerun the same scenario after a change to prove the gap is closed.