

Network Security Validation
Simulate external and internal network traffic to validate and optimize security controls.
Threat actors use sophisticated tactics and techniques to intercept and exploit network traffic.
16%
Organizations encountered C2
traffic in their network
Source: Akamai
42%
Overall web traffic originates
from botnets
Source: Akamai
7%
All network traffic
is malicious
Source: Cloudflare
Agentic Cyber Defense Engineering for Network Security
Attackers use AI to probe, evade and move through networks at machine speed, weaponizing exploits and blending malicious traffic into normal activity faster than teams can tune controls. Proving that your firewalls, IDS/IPS and segmentation policies can stop these evolving threats demands a new approach.
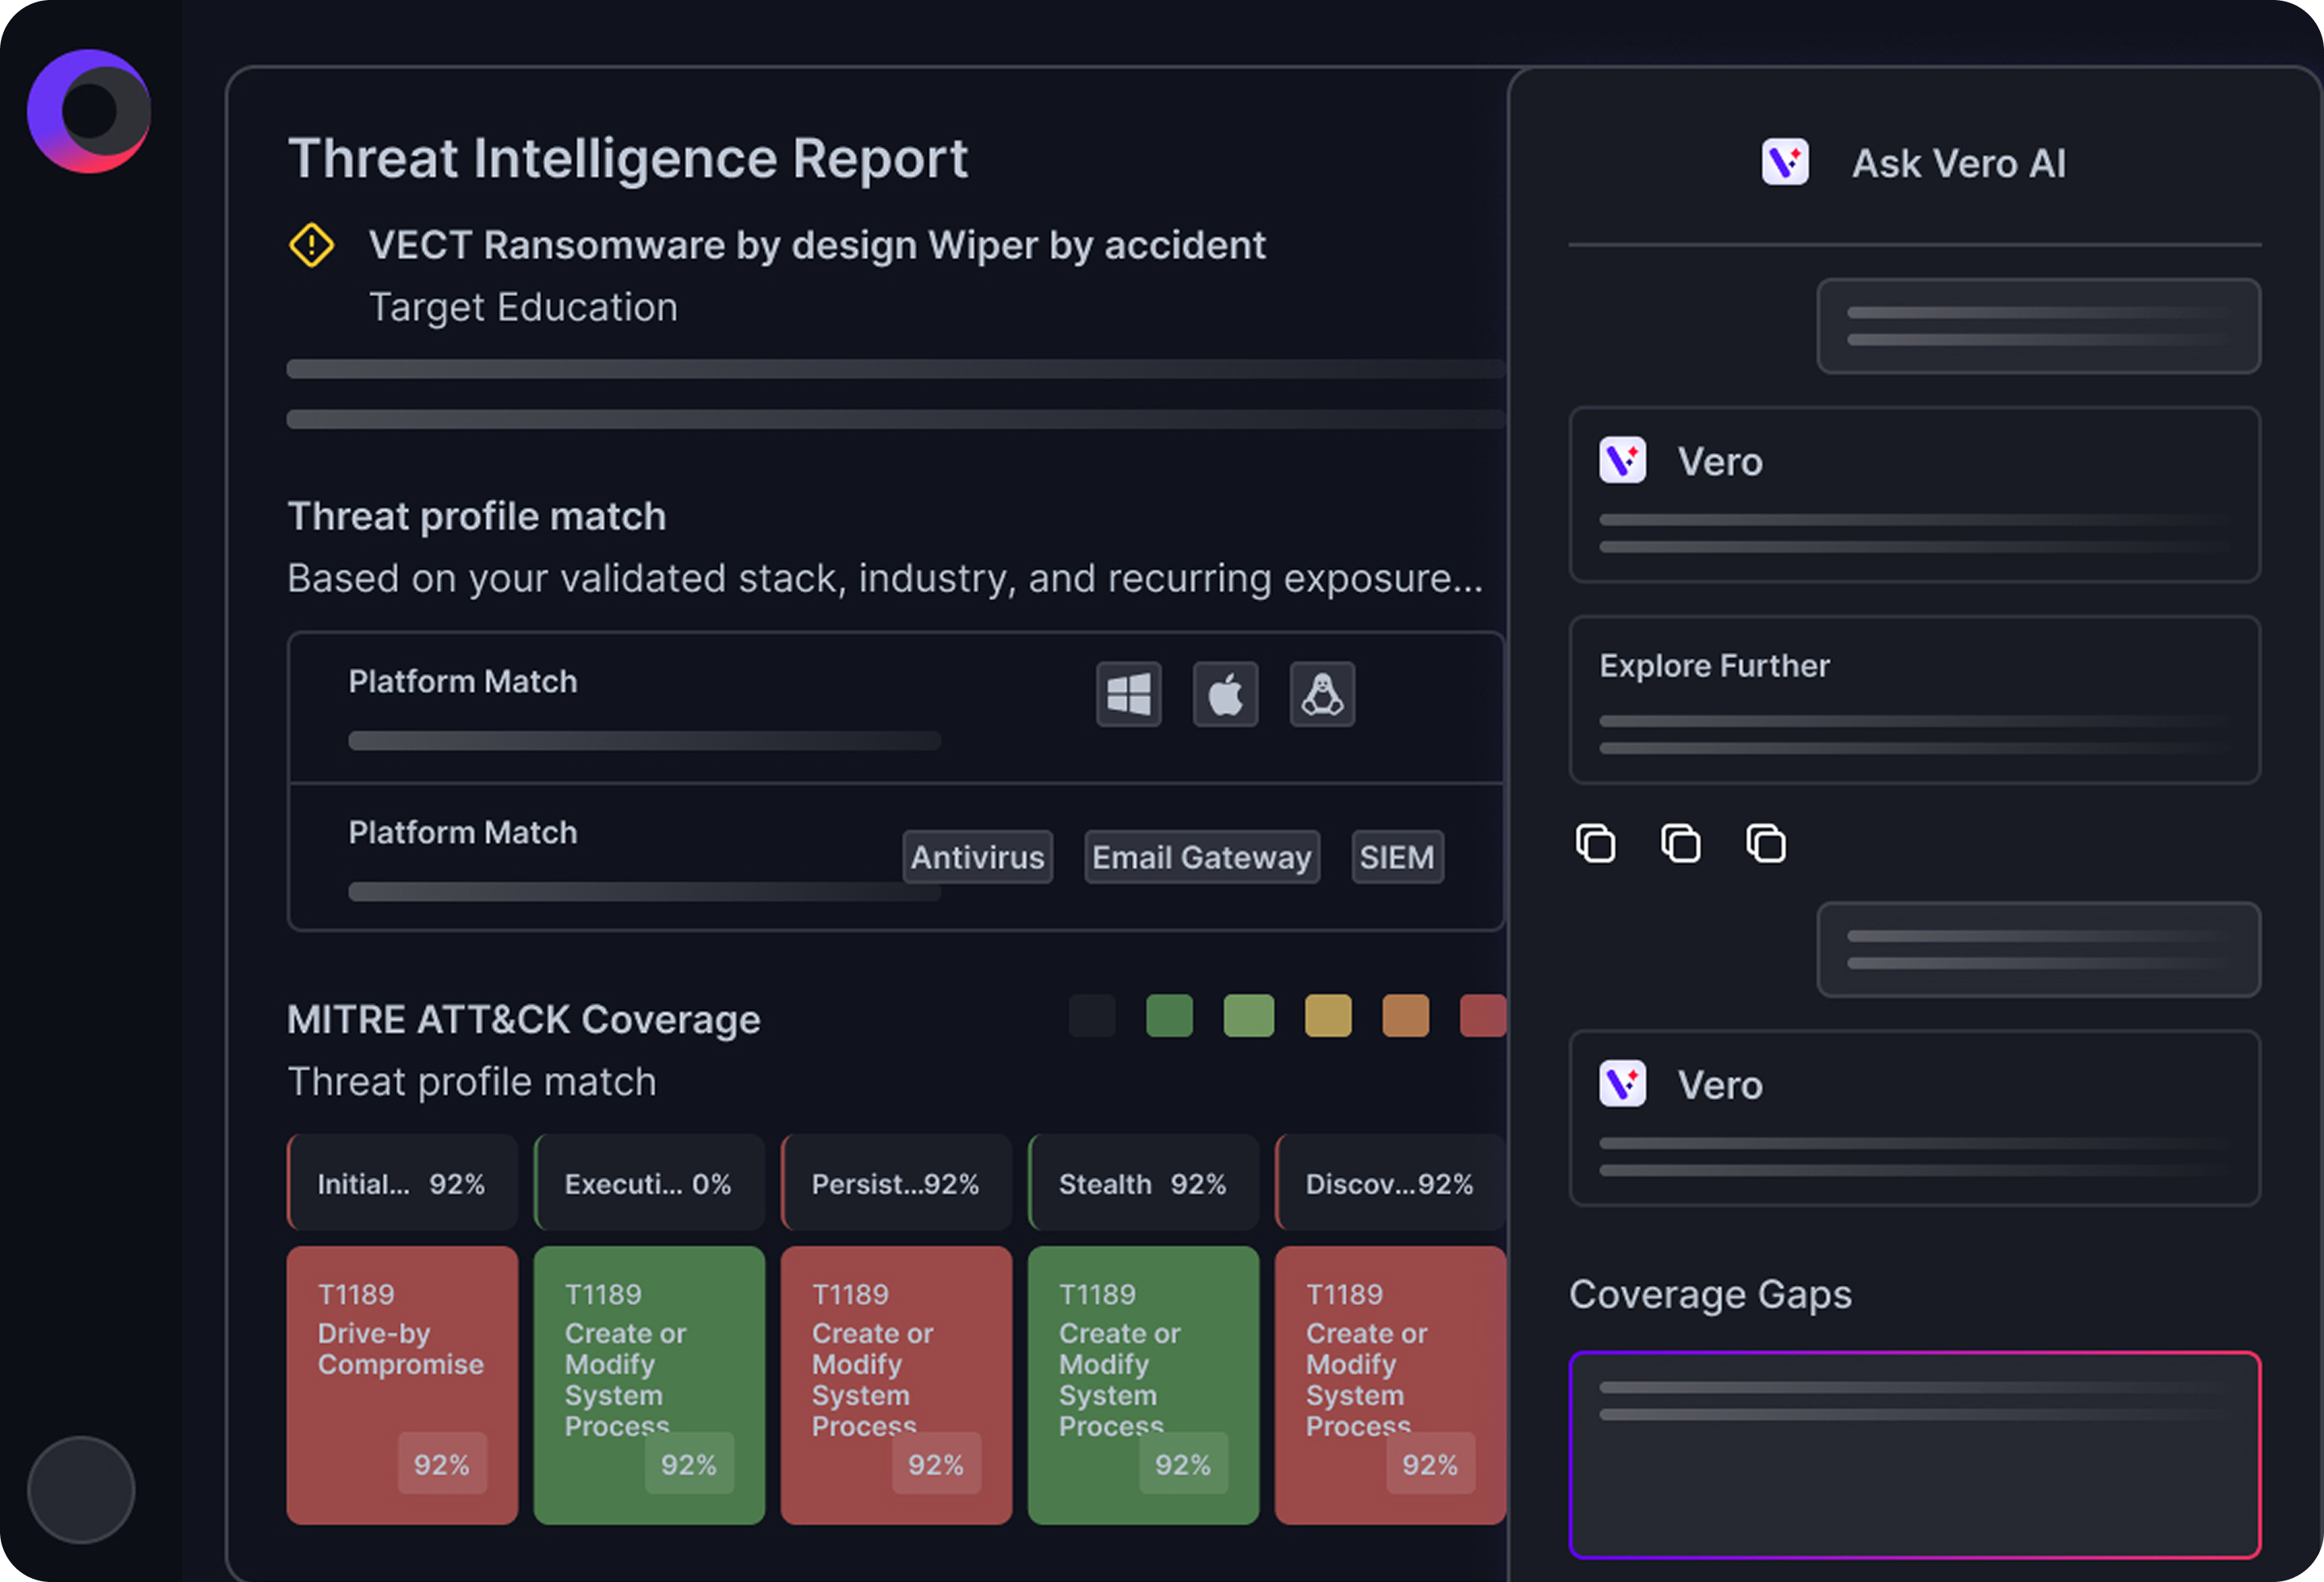
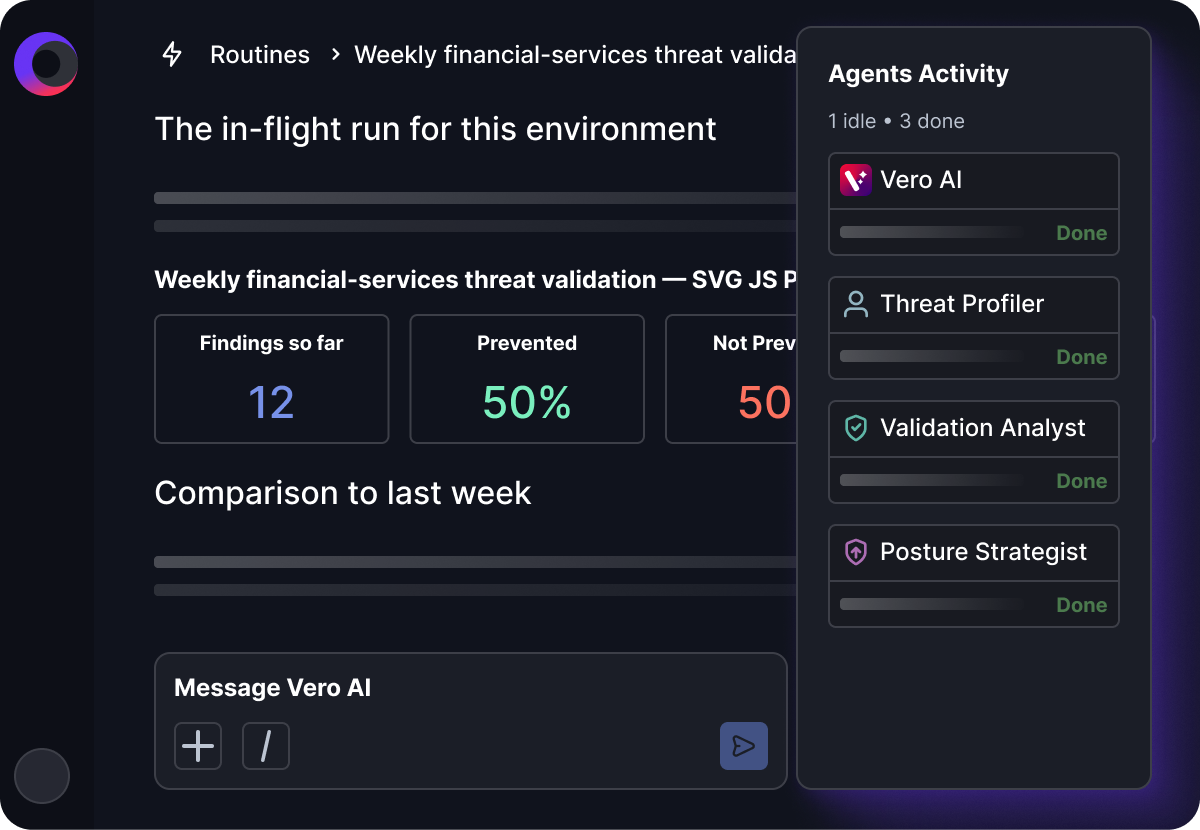
Powered by Vero AI, Cymulate replays real attack traffic across your own network paths to go beyond validation and deliver agentic cyber defense engineering. Cymulate proves network security effectiveness through production-safe attack simulation, prioritizing gaps with real-world impact and adapting your defenses with remediation guidance and streamlined mitigation workflows.
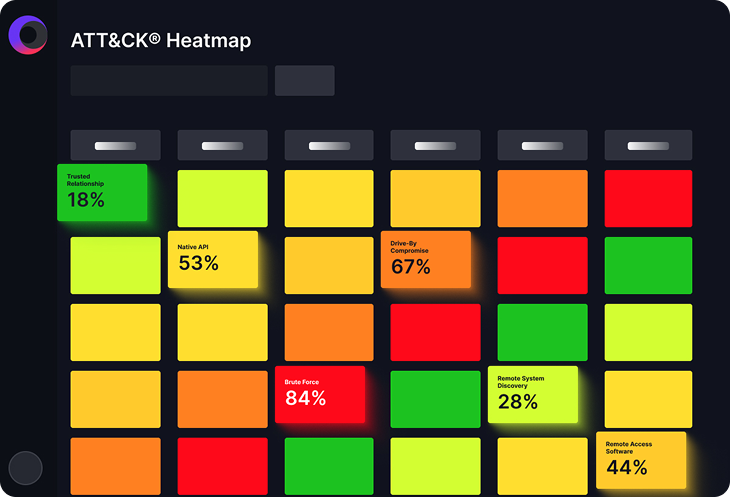
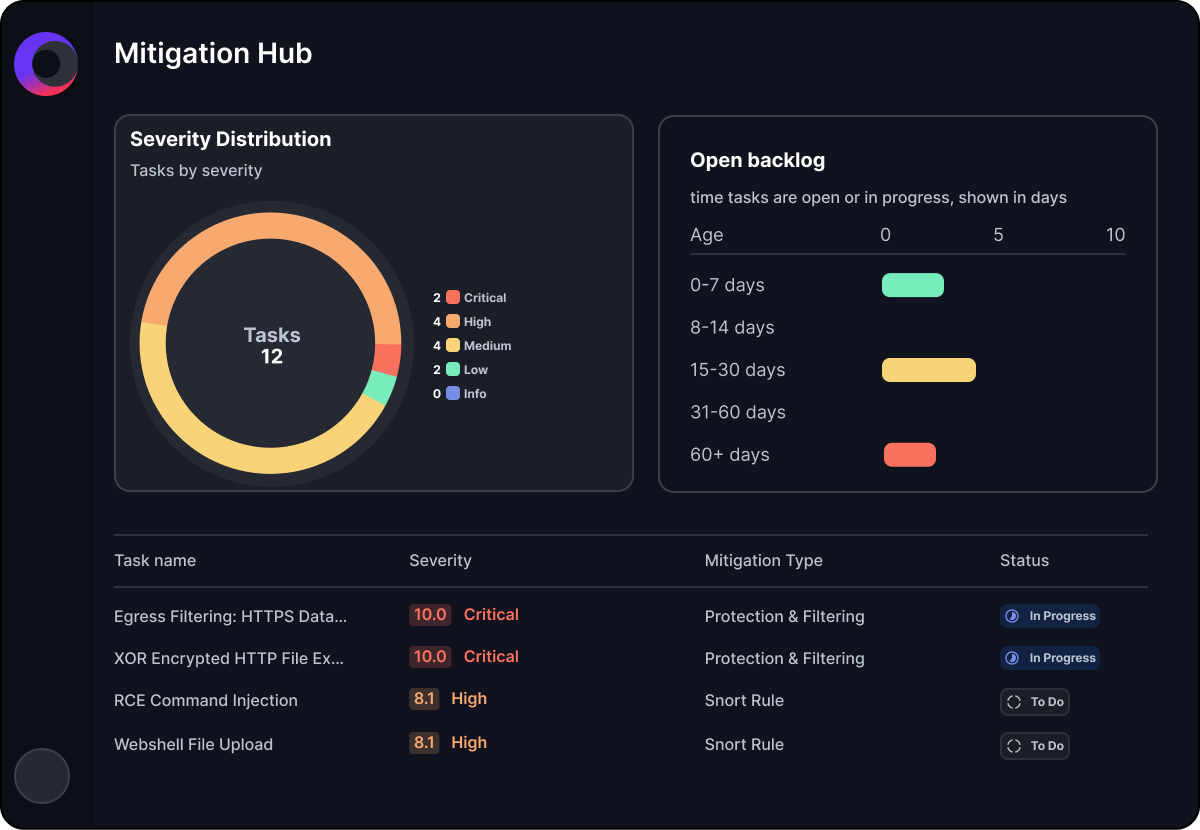
When Cymulate identifies malicious traffic that crossed your network undetected, a firewall or IDS/IPS rule that failed to block an exploit or a segmentation gap that allowed lateral movement, it provides guidance so you can close it, including ready-to-apply SNORT rules. Every update is revalidated against the original attack scenario, so stronger network protection is proven, not assumed.
Instead of one more list of findings, Cymulate closes the risk-to-fix gap and continuously proves, prioritizes and adapts your network defenses against the threats targeting them.
Network Validation and Optimization
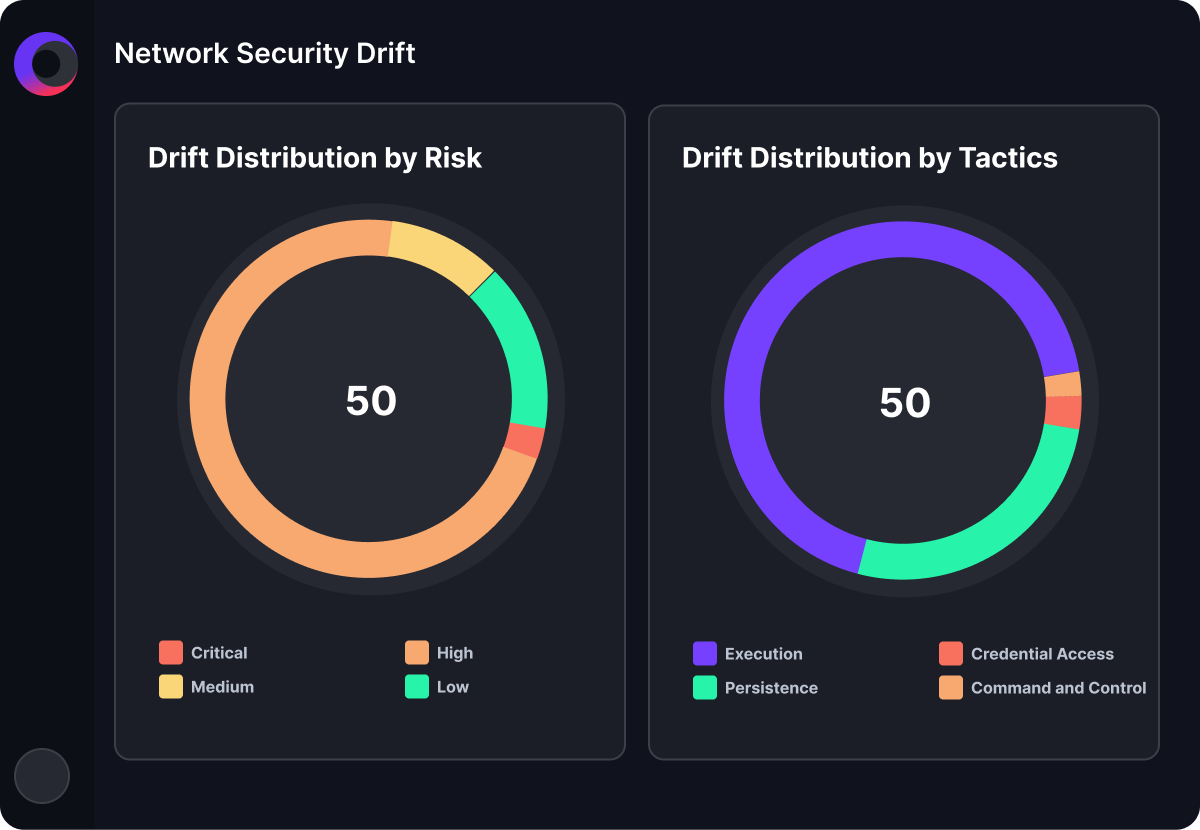
Solution Results

91%
Improvement in malicious file detection post mitigation.
50%
Improvement in the prevention of known exploit techniques.
168
Exploits prevented
from a single policy change.
Solution Benefits
Automated security validation
Identify gaps and weaknesses
Optimize security controls
Reduce exposure risk
What Our Customers Say
Featured Resources
View More Resources
Cymulate Exposure Validation
Prove security readiness with AI-powered exposure validation that continuously tests threats and strengthens defenses.
Control Validation and Optimization
Continuously validate and optimize security controls to improve prevention, detection and response effectiveness.
Network Attacks: Common Threats and How to Prevent Them
Learn how attackers exploit network weaknesses and how continuous security validation helps identify gaps before they are exploited.
FAQs
Network security validation is the practice of testing whether your network controls actually detect and block intrusion, exploitation and lateral movement, instead of assuming they do based on configuration or vendor claims. Cymulate does this by replaying malicious and non-malicious traffic across your live environment, north-south through the perimeter and east-west between internal segments, and checking what each control detected, logged or blocked. The result is evidence of how your firewalls, IDS/IPS, web gateways and segmentation policies perform against current attacker tactics, not just their published detection rates.
Cymulate replays PCAP-based attack traffic between two agents, a source and a destination, to reproduce authentic communication patterns across the network path you want to test. The two agents are the test point, so Cymulate shows whether the simulated traffic was prevented with no integration required. Where an integration with the network control is configured, Cymulate also queries the control for detection evidence, showing whether each technique was detected and acted on and where logging or blocking fell short. Because tests run against your live configuration and traffic paths, results reflect your actual environment and policy setup, not a generic lab environment.
Cymulate simulates the full range of network attack techniques, including exploitation of known CVEs such as PrintNightmare, SIGRed and Log4j, command-and-control traffic, worm propagation, lateral movement across protocols and data exfiltration over common transport channels. Simulations reproduce the traffic and behavior attackers use without carrying an actual malicious payload, so you can test detection, prevention and DLP effectiveness against realistic tactics without risking a real infection or compromise.
Yes. Cymulate’s network simulations are production-safe: they replay the same traffic patterns as real attacks without executing actual malicious code or putting hosts, network availability or data at risk. That safety is what allows testing to run continuously against your live firewalls, IDS/IPS and segmentation policies, rather than being limited to a lab environment or a periodic penetration test.
When simulated attack traffic crosses the network without being blocked or logged, Cymulate flags it as a gap, showing exactly which technique got through and which control missed it. Cymulate then provides prioritized, actionable tuning guidance, including ready-to-apply SNORT rules, firewall policy changes and IoCs that can be pushed to the network control automatically where an integration and the Auto Mitigation add-on are configured, and lets teams retest the same scenario after the change to confirm the gap is closed. Findings route to the right owners through Cymulate’s workflow and ticketing integrations, so a gap becomes a tracked fix rather than a one-off alert.
Continuously, or at a minimum, weekly: exploit code and evasion techniques change faster than the annual or quarterly cycle most organizations use for network testing today. Cymulate’s threat library updates daily, so new exploits and traffic-based techniques can be tested against your controls as they emerge rather than waiting for the next scheduled review. Continuous validation also catches configuration drift, such as a firewall rule or segmentation change that quietly opens a path between test cycles.