

What Is Enumeration in Cyber Security?
Enumeration in cybersecurity is the process of actively extracting detailed information from a target system, network or application. That information includes valid usernames, group memberships, hostnames, open ports, running services, software versions and security policies.
Attackers use enumeration to map an environment and choose the easiest path to their objective. Security teams and penetration testers use the same techniques to find those paths first and close them. Because enumeration usually happens early in an attack, it is also one of the best places to catch an attacker before real damage occurs.
Automation and AI have made enumeration faster and cheaper to run at scale. That shifts the advantage to security teams that can prove their controls detect enumeration activity and adapt quickly wherever gaps appear.
Enumeration vs. Reconnaissance vs. Scanning
These terms often get used interchangeably, but each describes a different stage of information gathering.
| Stage | What happens | Interaction with the target | Example |
| Reconnaissance (footprinting) | Collecting publicly available information about an organization | Passive or minimal | Searching LinkedIn, WHOIS and DNS records for employee names and domains |
| Scanning | Identifying live hosts and open ports | Active, broad | Running a port scan across a subnet |
| Enumeration | Querying specific systems and services to pull detailed data | Active, targeted | Querying a domain controller for every member of the Domain Admins group |
In short, reconnaissance and scanning tell an attacker what exists. Enumeration tells them what they can use.
How an Enumeration Attack Works
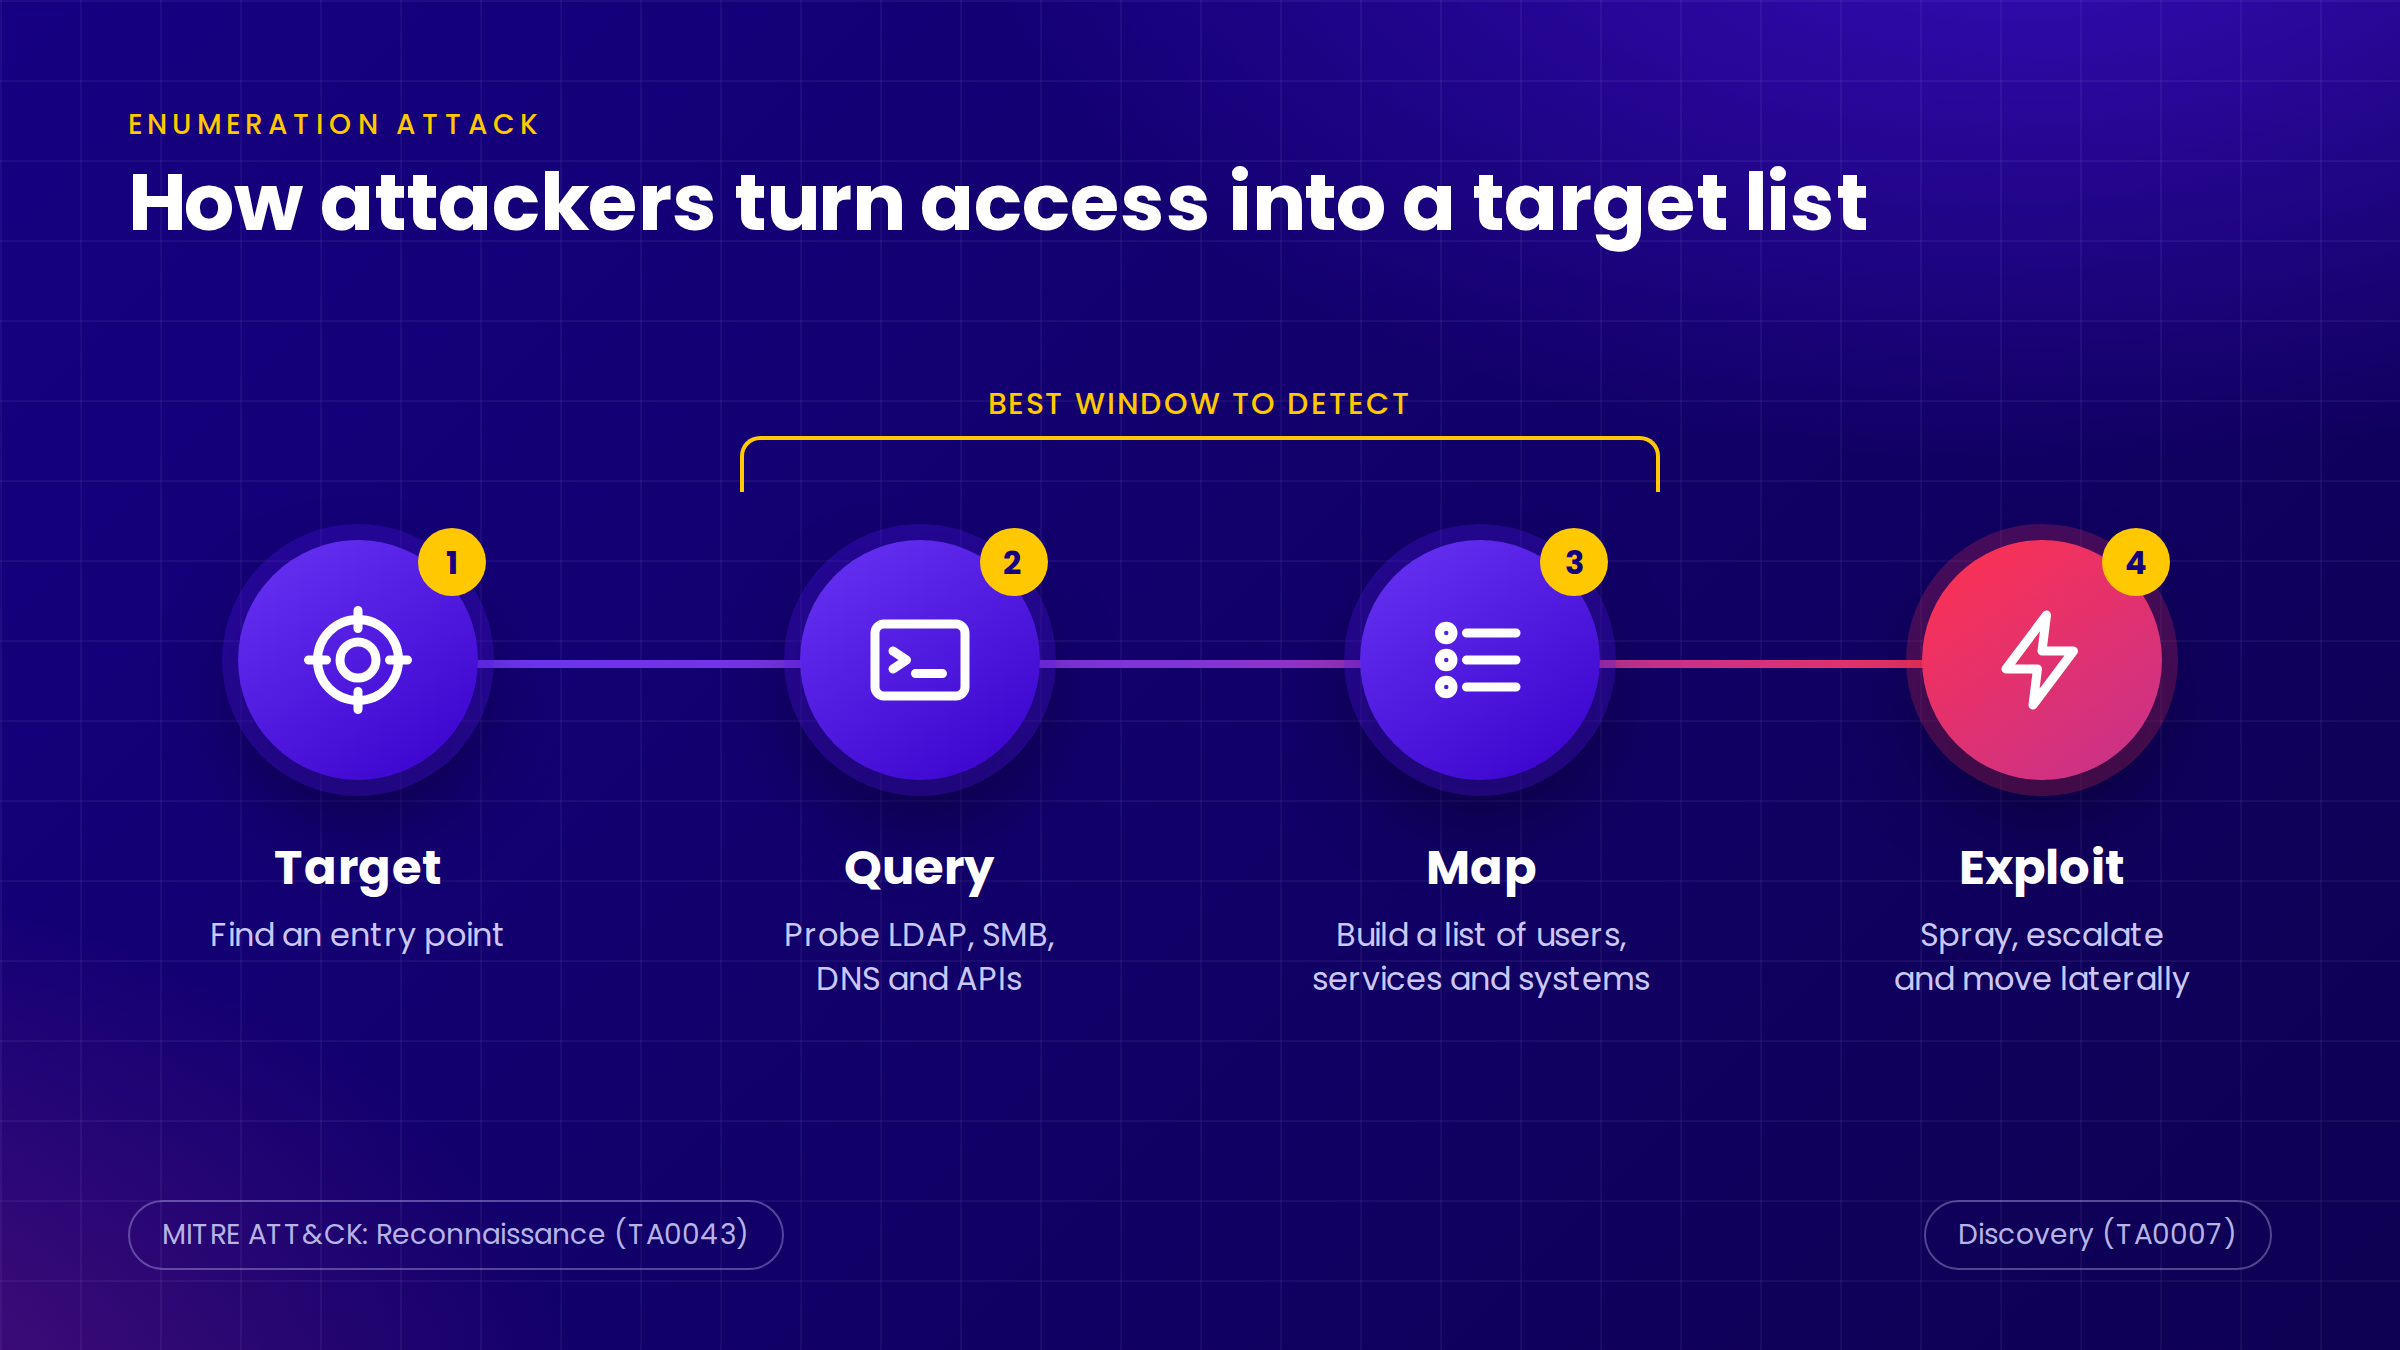
An enumeration attack is any attempt to systematically extract information from a target so it can be used in a follow-on attack. In the MITRE ATT&CK framework, most enumeration activity falls under the Reconnaissance (TA0043) and Discovery (TA0007) tactics.
A typical enumeration attack follows four steps:
- Establish access or a target. Enumeration can start externally, against a login page, API or exposed service, or internally, from a compromised endpoint.
- Query services directly. The attacker sends targeted requests to protocols such as LDAP, SMB, DNS, SNMP and Kerberos, or to application endpoints that respond differently to valid and invalid input.
- Build a target list. The results become an inventory of valid accounts, privileged groups, vulnerable software versions and reachable systems.
- Launch the next stage. The attacker uses that inventory for password spraying, credential stuffing, privilege escalation, lateral movement or exploitation of a known CVE.
For example, an attacker with access to a single workstation can query Active Directory over LDAP to list every account in the Domain Admins group. With that list, the attacker knows exactly which credentials to target next.
Types of Enumeration
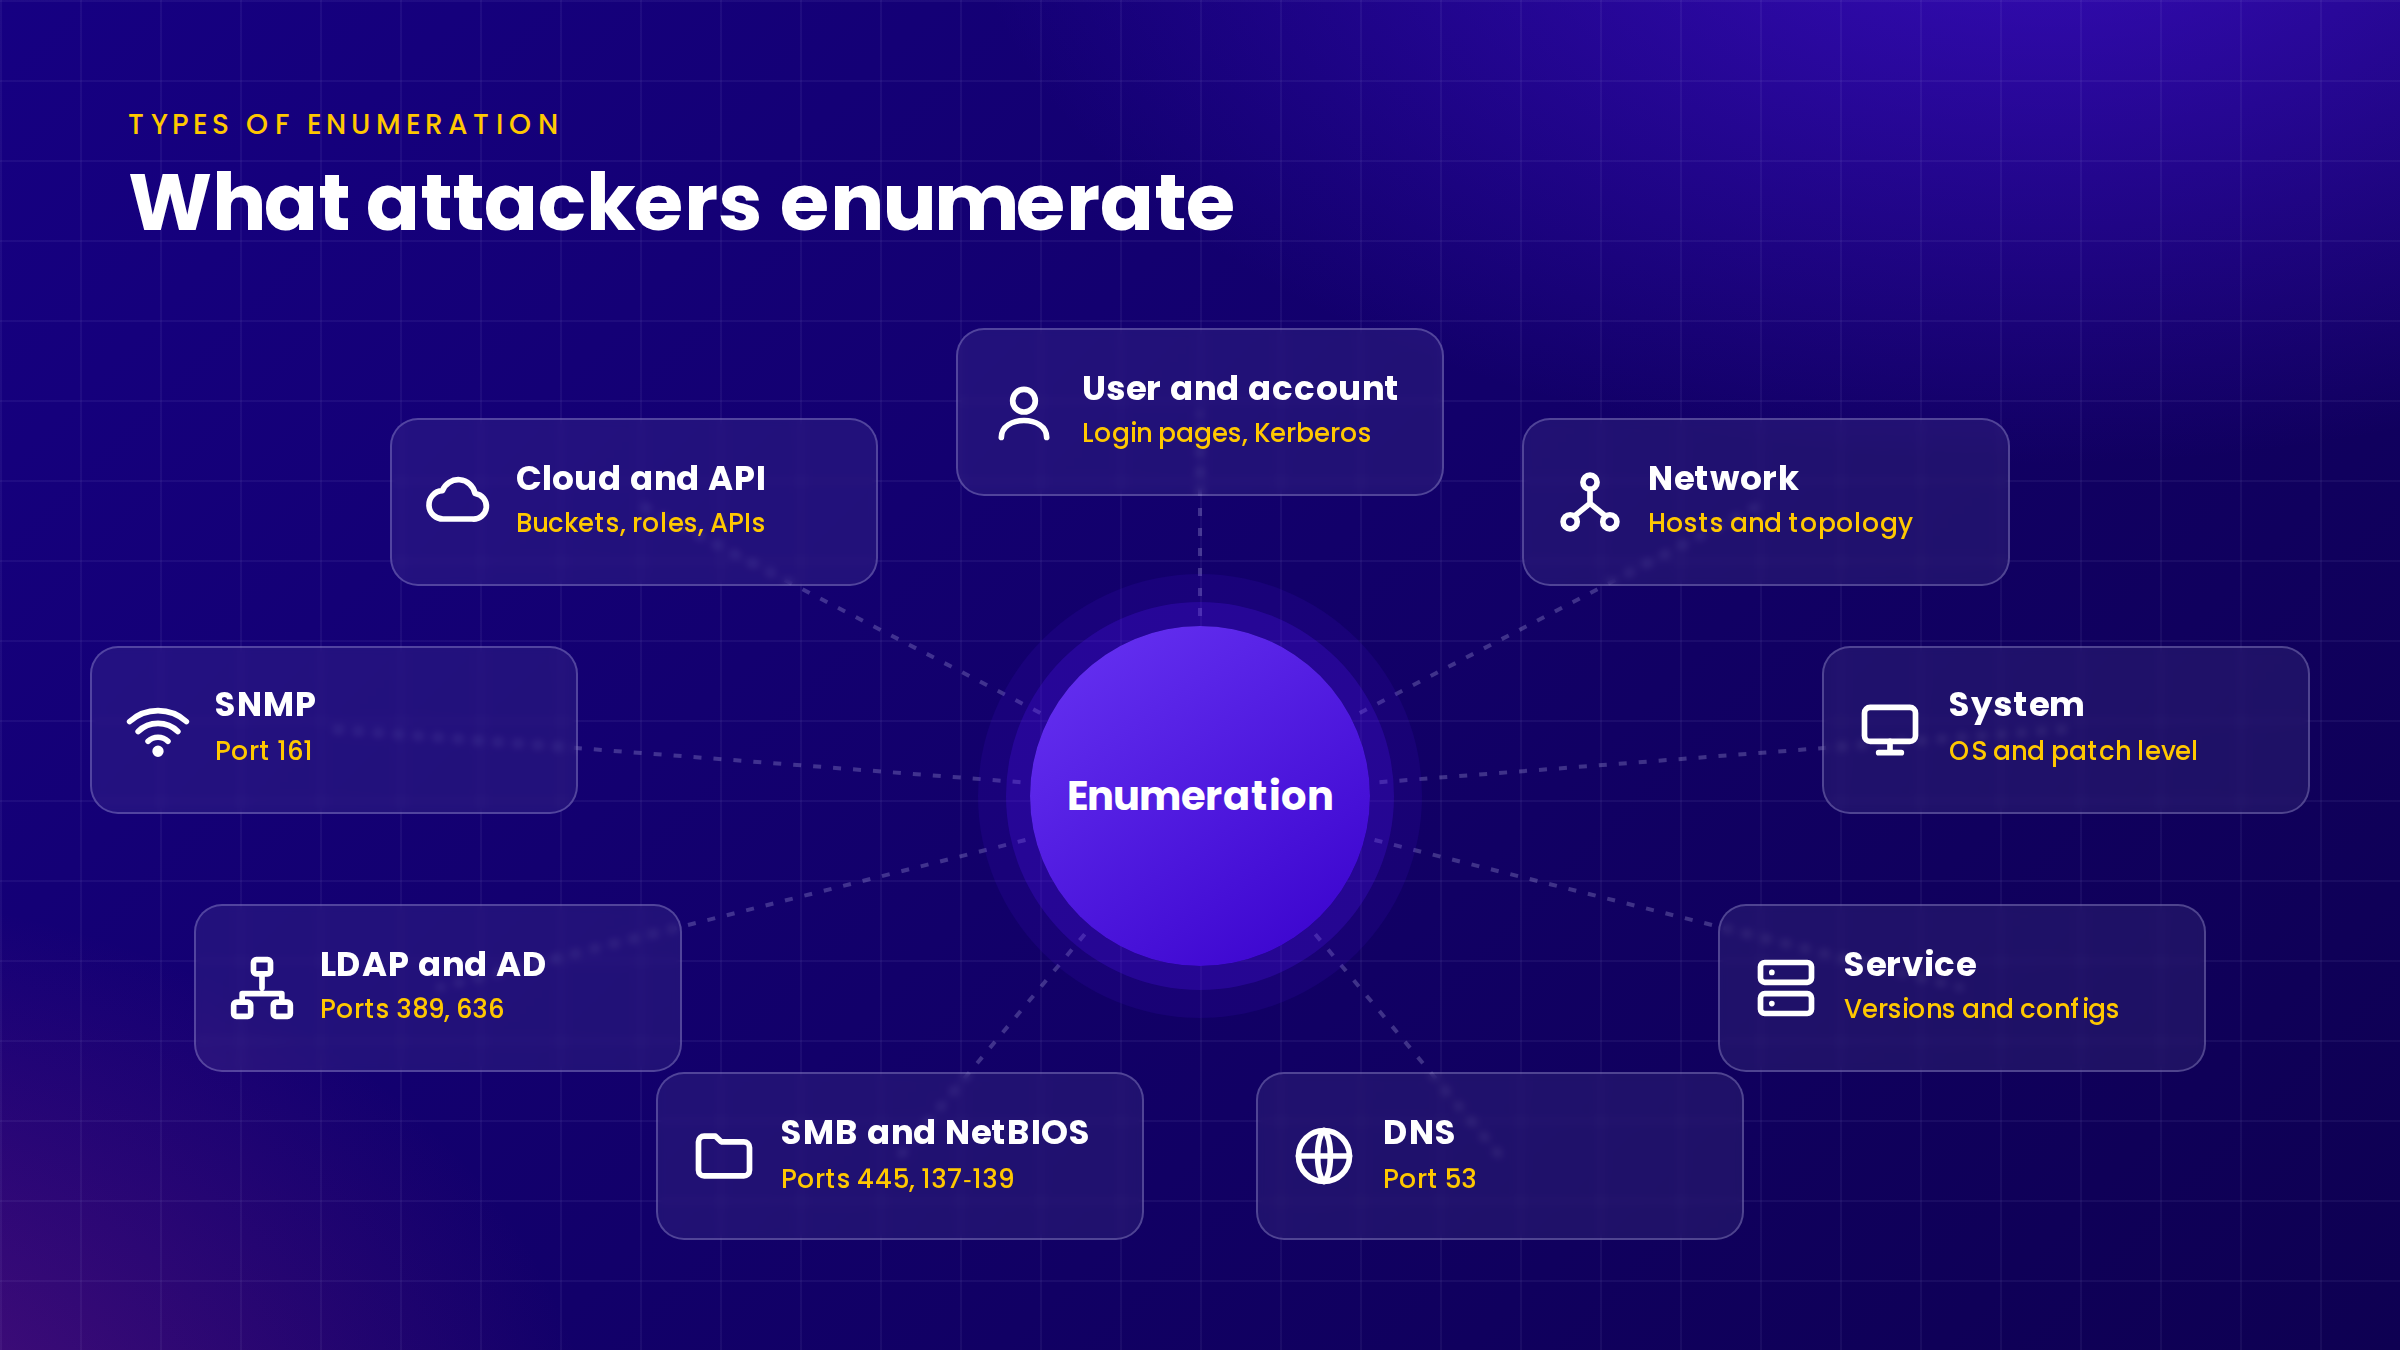
User and account enumeration
User enumeration identifies valid usernames and accounts (MITRE ATT&CK T1087, Account Discovery). It often happens through login portals, password reset forms, email systems or APIs that return different responses for valid and invalid usernames. A login page that says "Username not found" confirms to an attacker which usernames exist. Kerberos is another common source: tools like Kerbrute can validate usernames based on the error codes a domain controller returns.
Network enumeration
Network enumeration maps network topology and discovers connected devices, IP addresses and active protocols (T1018, Remote System Discovery). Attackers use it to find entry points and high-value assets. Tools like Nmap make this fast, so reducing network exposure, such as closing unnecessary ports, is an important first defense.
System enumeration
System enumeration uncovers operating system details, including versions, patch levels, installed software and configuration (T1082, System Information Discovery). Identifying an outdated Windows Server version, for instance, tells an attacker which known vulnerabilities to try. Consistent patching limits the value of this information.
Service enumeration
Service enumeration identifies active services, their versions and configurations (T1046, Network Service Discovery). An exposed MySQL database on port 3306 could signal a misconfiguration that allows unauthorized access. Hardening service configurations and restricting access reduces this risk.
DNS enumeration
DNS enumeration collects hostnames, subdomains and IP addresses from DNS servers. A misconfigured server that allows zone transfers (AXFR) can hand an attacker a complete map of internal hostnames in a single request. Restricting zone transfers to authorized secondary servers closes this gap.
SMB and NetBIOS enumeration
SMB (port 445) and NetBIOS (ports 137 to 139) can expose shared folders, user lists, group memberships and password policies (T1135, Network Share Discovery). Older or misconfigured systems that allow anonymous "null sessions" are especially easy to enumerate with tools like enum4linux.
LDAP and Active Directory enumeration
LDAP (ports 389 and 636) gives attackers a detailed view of Active Directory: users, groups, computers, trust relationships and permissions (T1069, Permission Groups Discovery). Tools like BloodHound turn this data into attack paths that show the shortest route to domain admin privileges.
SNMP enumeration
SNMP (port 161) can reveal device configurations, running processes, network interfaces and routing tables. Devices that still use default community strings, such as "public," make this information available to anyone who asks. Changing default strings and moving to SNMPv3 limits exposure.
Cloud and API enumeration
In cloud environments, attackers enumerate storage buckets, identities, roles and services (T1580, Cloud Infrastructure Discovery, and T1526, Cloud Service Discovery). APIs that return different errors or response times for valid and invalid resources also give attackers a reliable way to confirm what exists.
Common Enumeration Tools
Attackers and penetration testers rely on many of the same tools. Knowing what they do helps security teams build detections that match real activity:
- Nmap: Discovers hosts, open ports, services and operating system versions
- enum4linux: Enumerates users, shares and policies over SMB and NetBIOS
- BloodHound and SharpHound: Map Active Directory relationships and privilege escalation paths
- Kerbrute: Validates usernames and performs password spraying against Kerberos
- ldapsearch: Queries LDAP directories for users, groups and attributes
- snmpwalk: Pulls device information from SNMP-enabled systems
- dnsrecon and dig: Enumerate DNS records and test for zone transfers
How to Detect Enumeration Attacks
Enumeration generates signals across the network, identity systems and endpoints. The earlier security teams catch these signals, the less time attackers have to act on what they find.
Key indicators of enumeration:
- Unusual network traffic: Repeated scans, sequential connection attempts across ports or a sudden spike in traffic to specific services
- Failed login patterns: Many failed logins across different usernames from one source, which points to username enumeration or password spraying
- Kerberos errors: A high volume of authentication failures for unknown usernames (Windows Event ID 4768 with failure code 0x6)
- Group membership queries: Spikes in local or domain group enumeration (Windows Event IDs 4798 and 4799) or large LDAP query volumes from a single host
- Protocol probing: Zone transfer requests, SMB null session attempts or SNMP queries from unexpected sources
- Discovery commands on endpoints: Commands such as net user, net group or whoami /groups run in unusual contexts
Tools that support detection:
- Intrusion detection systems (IDS): Tools such as Snort and Suricata flag scanning patterns and suspicious traffic in real time.
- Security information and event management (SIEM): Platforms such as Splunk centralize logs and correlate indicators across network, identity and endpoint data.
- Endpoint detection and response (EDR): EDR tools spot discovery commands and enumeration tools running on hosts.
Monitoring best practices:
- Establish a baseline. Knowing what normal LDAP, DNS and authentication activity looks like makes anomalies easier to spot.
- Configure targeted alerts. Alert on repeated failed logins, Kerberos errors and high-volume directory queries.
- Test your detections. Run simulated enumeration techniques to confirm that alerts fire as expected and reach the right team.
How to Prevent Enumeration Attacks
Preventing enumeration means reducing what attackers can learn and making every query harder and noisier.
Secure login and authentication flows
Use generic error messages such as "Invalid credentials" instead of "User not found" on login and password reset pages. Add rate limiting and account lockout policies to slow automated attempts, and enforce multi-factor authentication (MFA) so a valid username alone gives an attacker little to work with.
Minimize public exposure
Remove unnecessary DNS records, keep WHOIS information private and limit publicly available employee directories and contact details. Less public information means fewer valid usernames and email addresses for attackers to test.
Lock down enumeration-prone protocols
Restrict DNS zone transfers, disable SMB null sessions, replace default SNMP community strings (or move to SNMPv3) and limit which accounts can query sensitive Active Directory attributes.
Apply firewalls and access controls
Block unnecessary ports and protocols and allow only required traffic. For example, a public web server needs only ports 80 (HTTP) and 443 (HTTPS) open to the internet.
Segment the network
Separate sensitive systems, such as payment processing, from the broader corporate network. Segmentation limits what an attacker can discover and reach from any single foothold.
Harden services
Disable unused services, change default configurations and patch regularly. Replacing Telnet with SSH for remote access is a simple example.
Train employees
Attackers often gather usernames and organizational details through social engineering before any technical enumeration begins. Training helps employees recognize phishing, pretexting and other information-gathering tactics.
Continuously validate your controls
Penetration testing, vulnerability scanning and security posture assessments all help identify weaknesses. Because environments and attacker techniques change daily, continuous exposure validation confirms whether your controls detect and stop enumeration today, not just at the last annual test.
Validate Your Defenses Against Enumeration with Cymulate
Most organizations already have controls that should detect or block enumeration: EDR, SIEM rules, firewalls and identity protections. The real question is whether those controls work against the techniques attackers use right now, and how quickly they can be updated when they fall short.
Cymulate answers that question with agentic cyber defense engineering, a closed-loop approach that continuously proves, prioritizes and adapts your defenses.
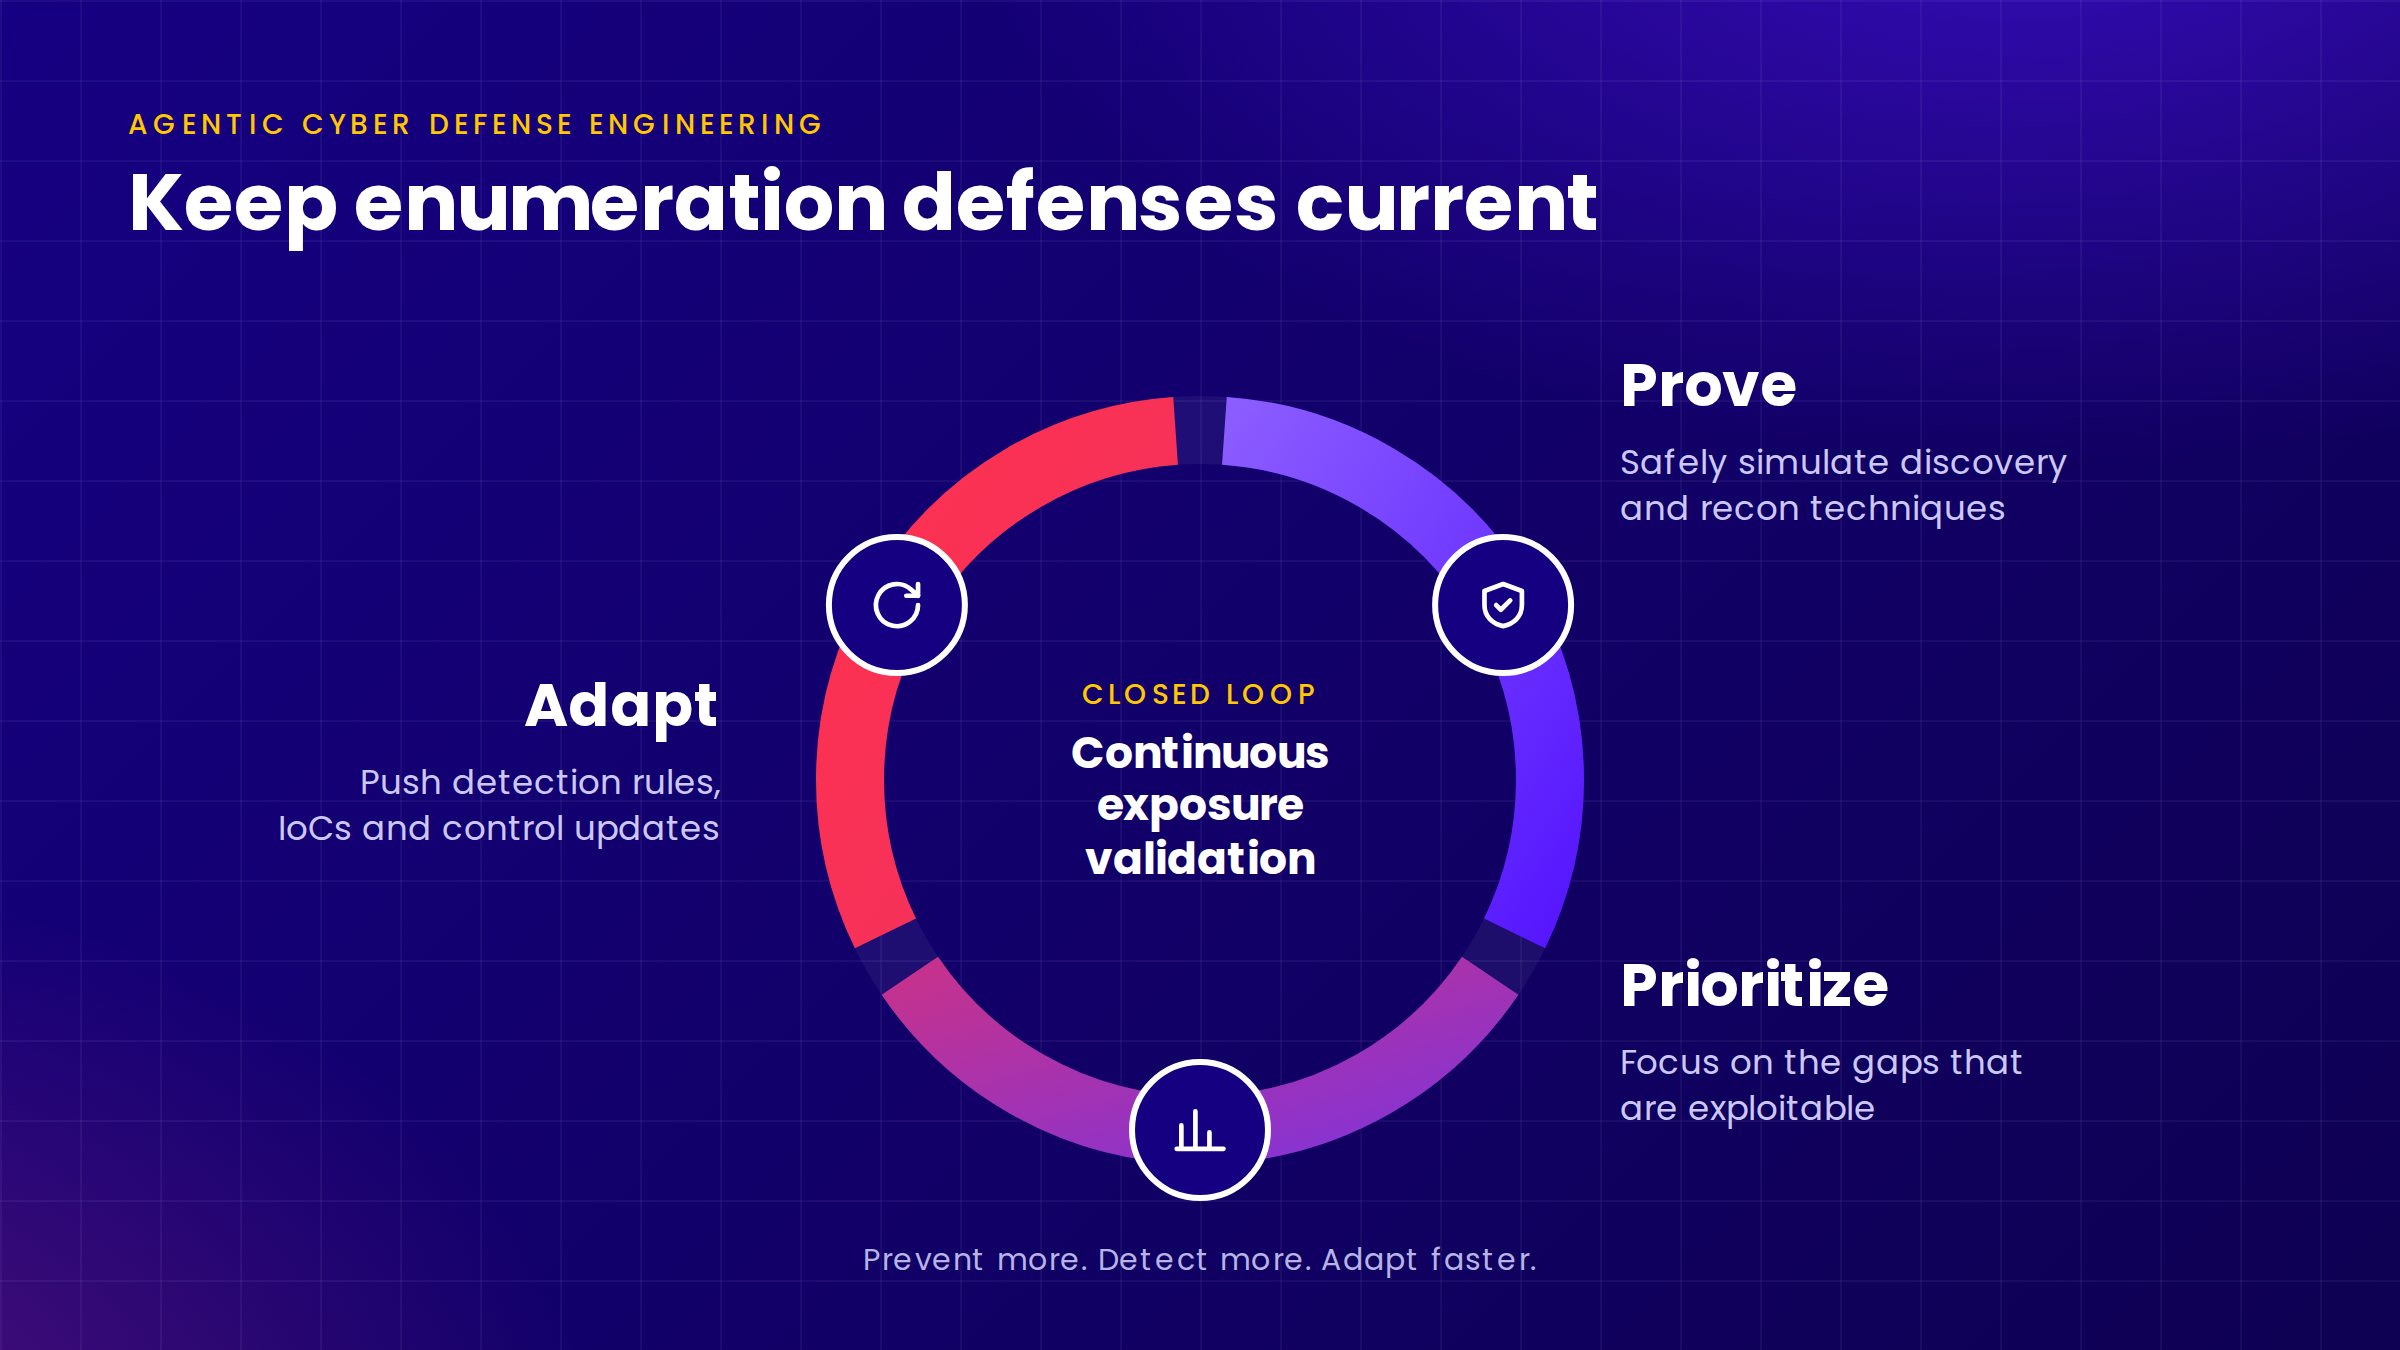
- Prove: Cymulate Exposure Validation safely simulates reconnaissance and discovery techniques mapped to MITRE ATT&CK, including account, network, service and cloud enumeration, to show which activity your controls prevent, detect or miss.
- Prioritize: Validation results show which enumeration gaps are exploitable in your environment, so teams focus on what matters most instead of chasing every alert.
- Adapt: Cymulate delivers vendor-specific mitigations, including detection rules, IoCs and recommended control updates. Cymulate Detection Studio validates SIEM rules against real attack scenarios to expose detection gaps, and Cymulate Auto Mitigation pushes updates directly to integrated security controls.
On average, Cymulate customers improve threat prevention from about 70% to more than 90% and improve threat detection by more than 50%, as measured by validated MITRE ATT&CK coverage.
Key Takeaways
- Enumeration is the active extraction of detailed information, such as usernames, services and system configurations, from a target environment.
- An enumeration attack uses that information to plan credential attacks, lateral movement and exploitation.
- Common types include user, network, system, service, DNS, SMB, LDAP, SNMP and cloud enumeration.
- Detection depends on monitoring authentication, directory, network and endpoint signals, and on testing that those detections fire.
- Prevention combines reduced exposure, hardened protocols, strong authentication and continuous validation that keeps defenses current as threats change.
Frequently Asked Questions
Enumeration in cyber security is the process of actively querying a system, network or application to extract detailed information such as usernames, group memberships, open ports, running services and software versions. Attackers use it to plan attacks, and security teams use it to find and fix weaknesses first.
An enumeration attack is an attempt to systematically extract information from a target, often by exploiting differences in how a system responds to valid and invalid input. A common example is username enumeration, where a login page or API reveals which accounts exist, giving attackers a list of targets for password attacks.
Scanning identifies live hosts and open ports across a network. Enumeration goes a step further by querying specific services on those hosts to extract detailed data, such as user accounts, shares or configuration settings.
The most common types are user enumeration, network enumeration, system enumeration, service enumeration, DNS enumeration, SMB and NetBIOS enumeration, LDAP enumeration, SNMP enumeration and cloud or API enumeration.
Use generic error messages for login and password reset flows, apply rate limiting and account lockout policies, enforce MFA and monitor for high volumes of failed logins across many usernames. Regularly test these controls to confirm they work as expected.
Featured Resources
View More Resources
Validate What Matters: Simulate Real-World Identity and Privilege Attacks in AD and Entra ID
Test AD and Entra ID defenses with real-world identity attack simulations that expose exploitable gaps.
Credit Union Boosts Threat Prevention & Detection with Cymulate
Learn how a credit union automated live-data exercises to validate exposure, improve threat readiness, and streamline SecOps.
Proactive, AI-Powered SIEM Rule Validation and Detection Engineering
Save time and resources by automating the most critical tasks in modern SecOps