Frequently Asked Questions
Product Information & Security Control Validation
What is security control validation and how does Cymulate support it?
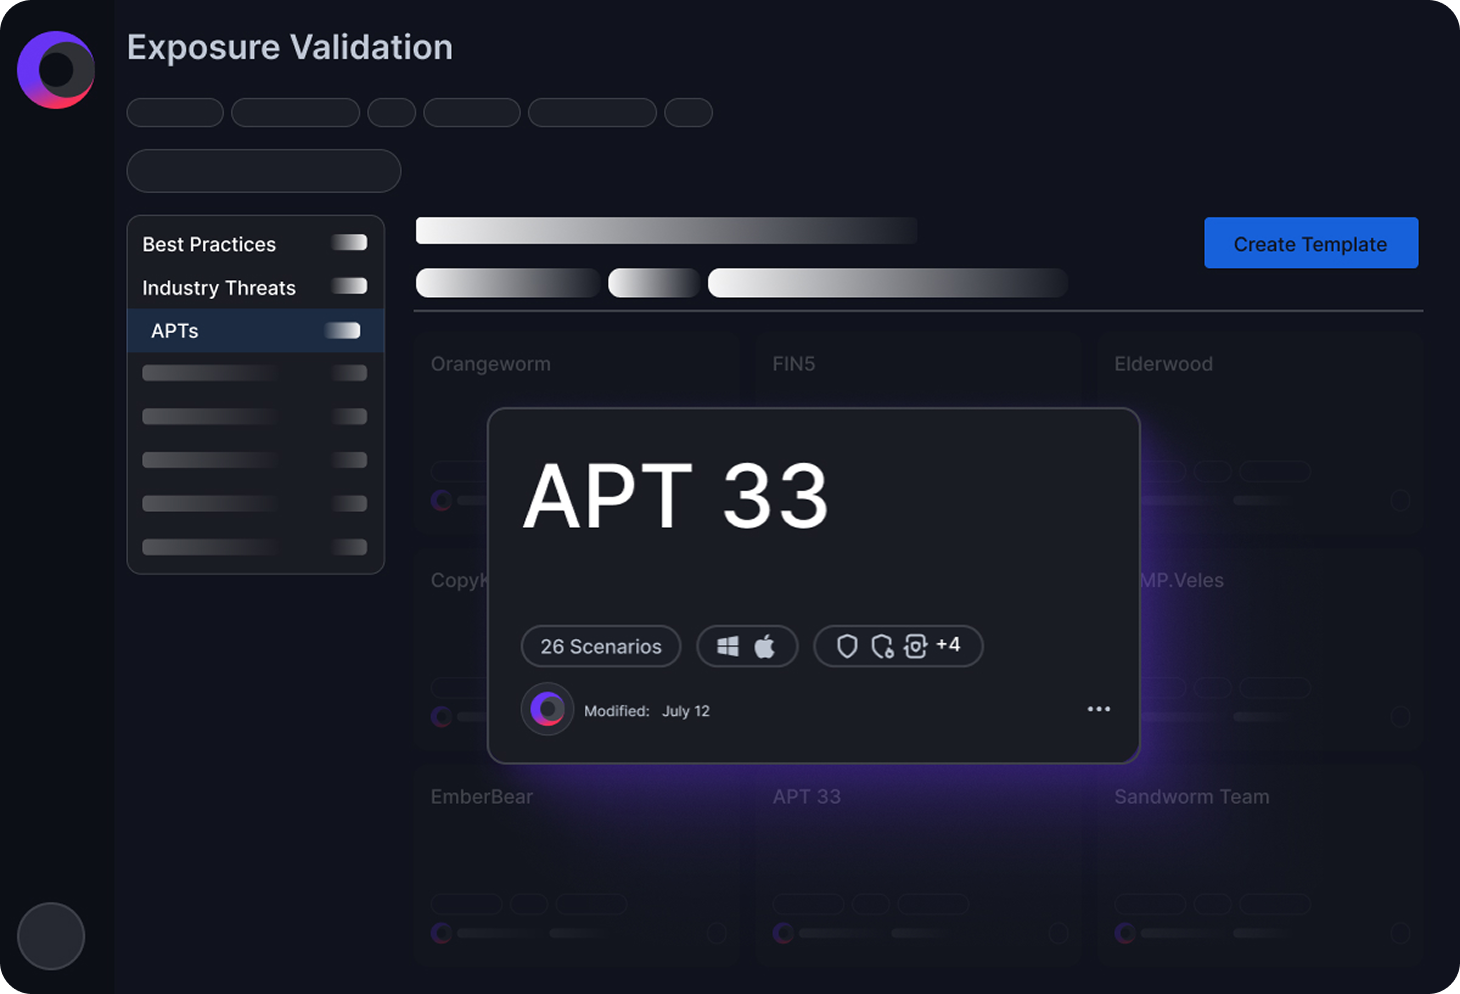
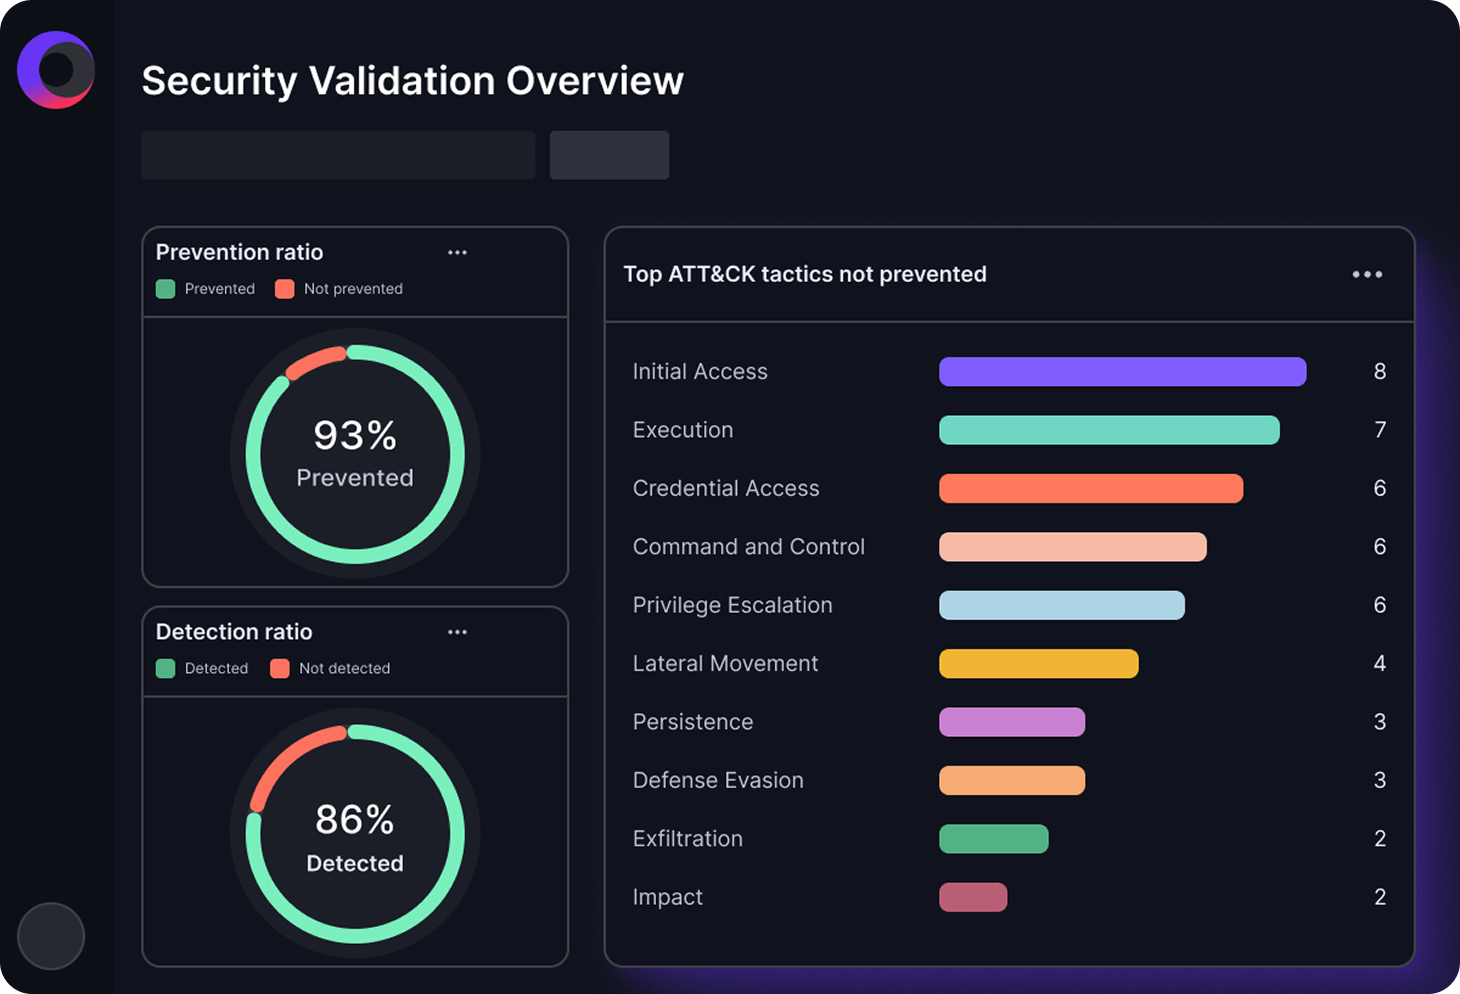
Security control validation is the process of continuously testing whether your organization’s security controls can effectively detect, prevent, and respond to real-world cyber threats. Cymulate automates production-safe testing across your control stack, simulating realistic attack behaviors to confirm if preventive controls block expected activity, detections are triggered correctly, and response workflows operate as intended. The platform turns validation results into prioritized remediation guidance, automated updates, and closed-loop retesting, helping organizations measure effectiveness, uncover gaps, and verify improvements over time. Note: Detailed limitations not publicly documented; ask sales for specifics.
Which types of security controls can Cymulate validate?
Cymulate validates the effectiveness of security controls across your entire security stack, including endpoint security (AV/EDR/XDR), email gateways, network security (firewalls, IDS/IPS, secure web gateways), identity and access controls, SIEM and SOAR platforms, cloud security controls, web application firewalls, and data loss prevention (DLP) solutions. The platform safely simulates attacker techniques to verify configuration, detection, and prevention capabilities. Note: Some legacy or highly customized controls may require additional integration work; contact Cymulate for compatibility details.
How does Cymulate tailor validation to my environment?
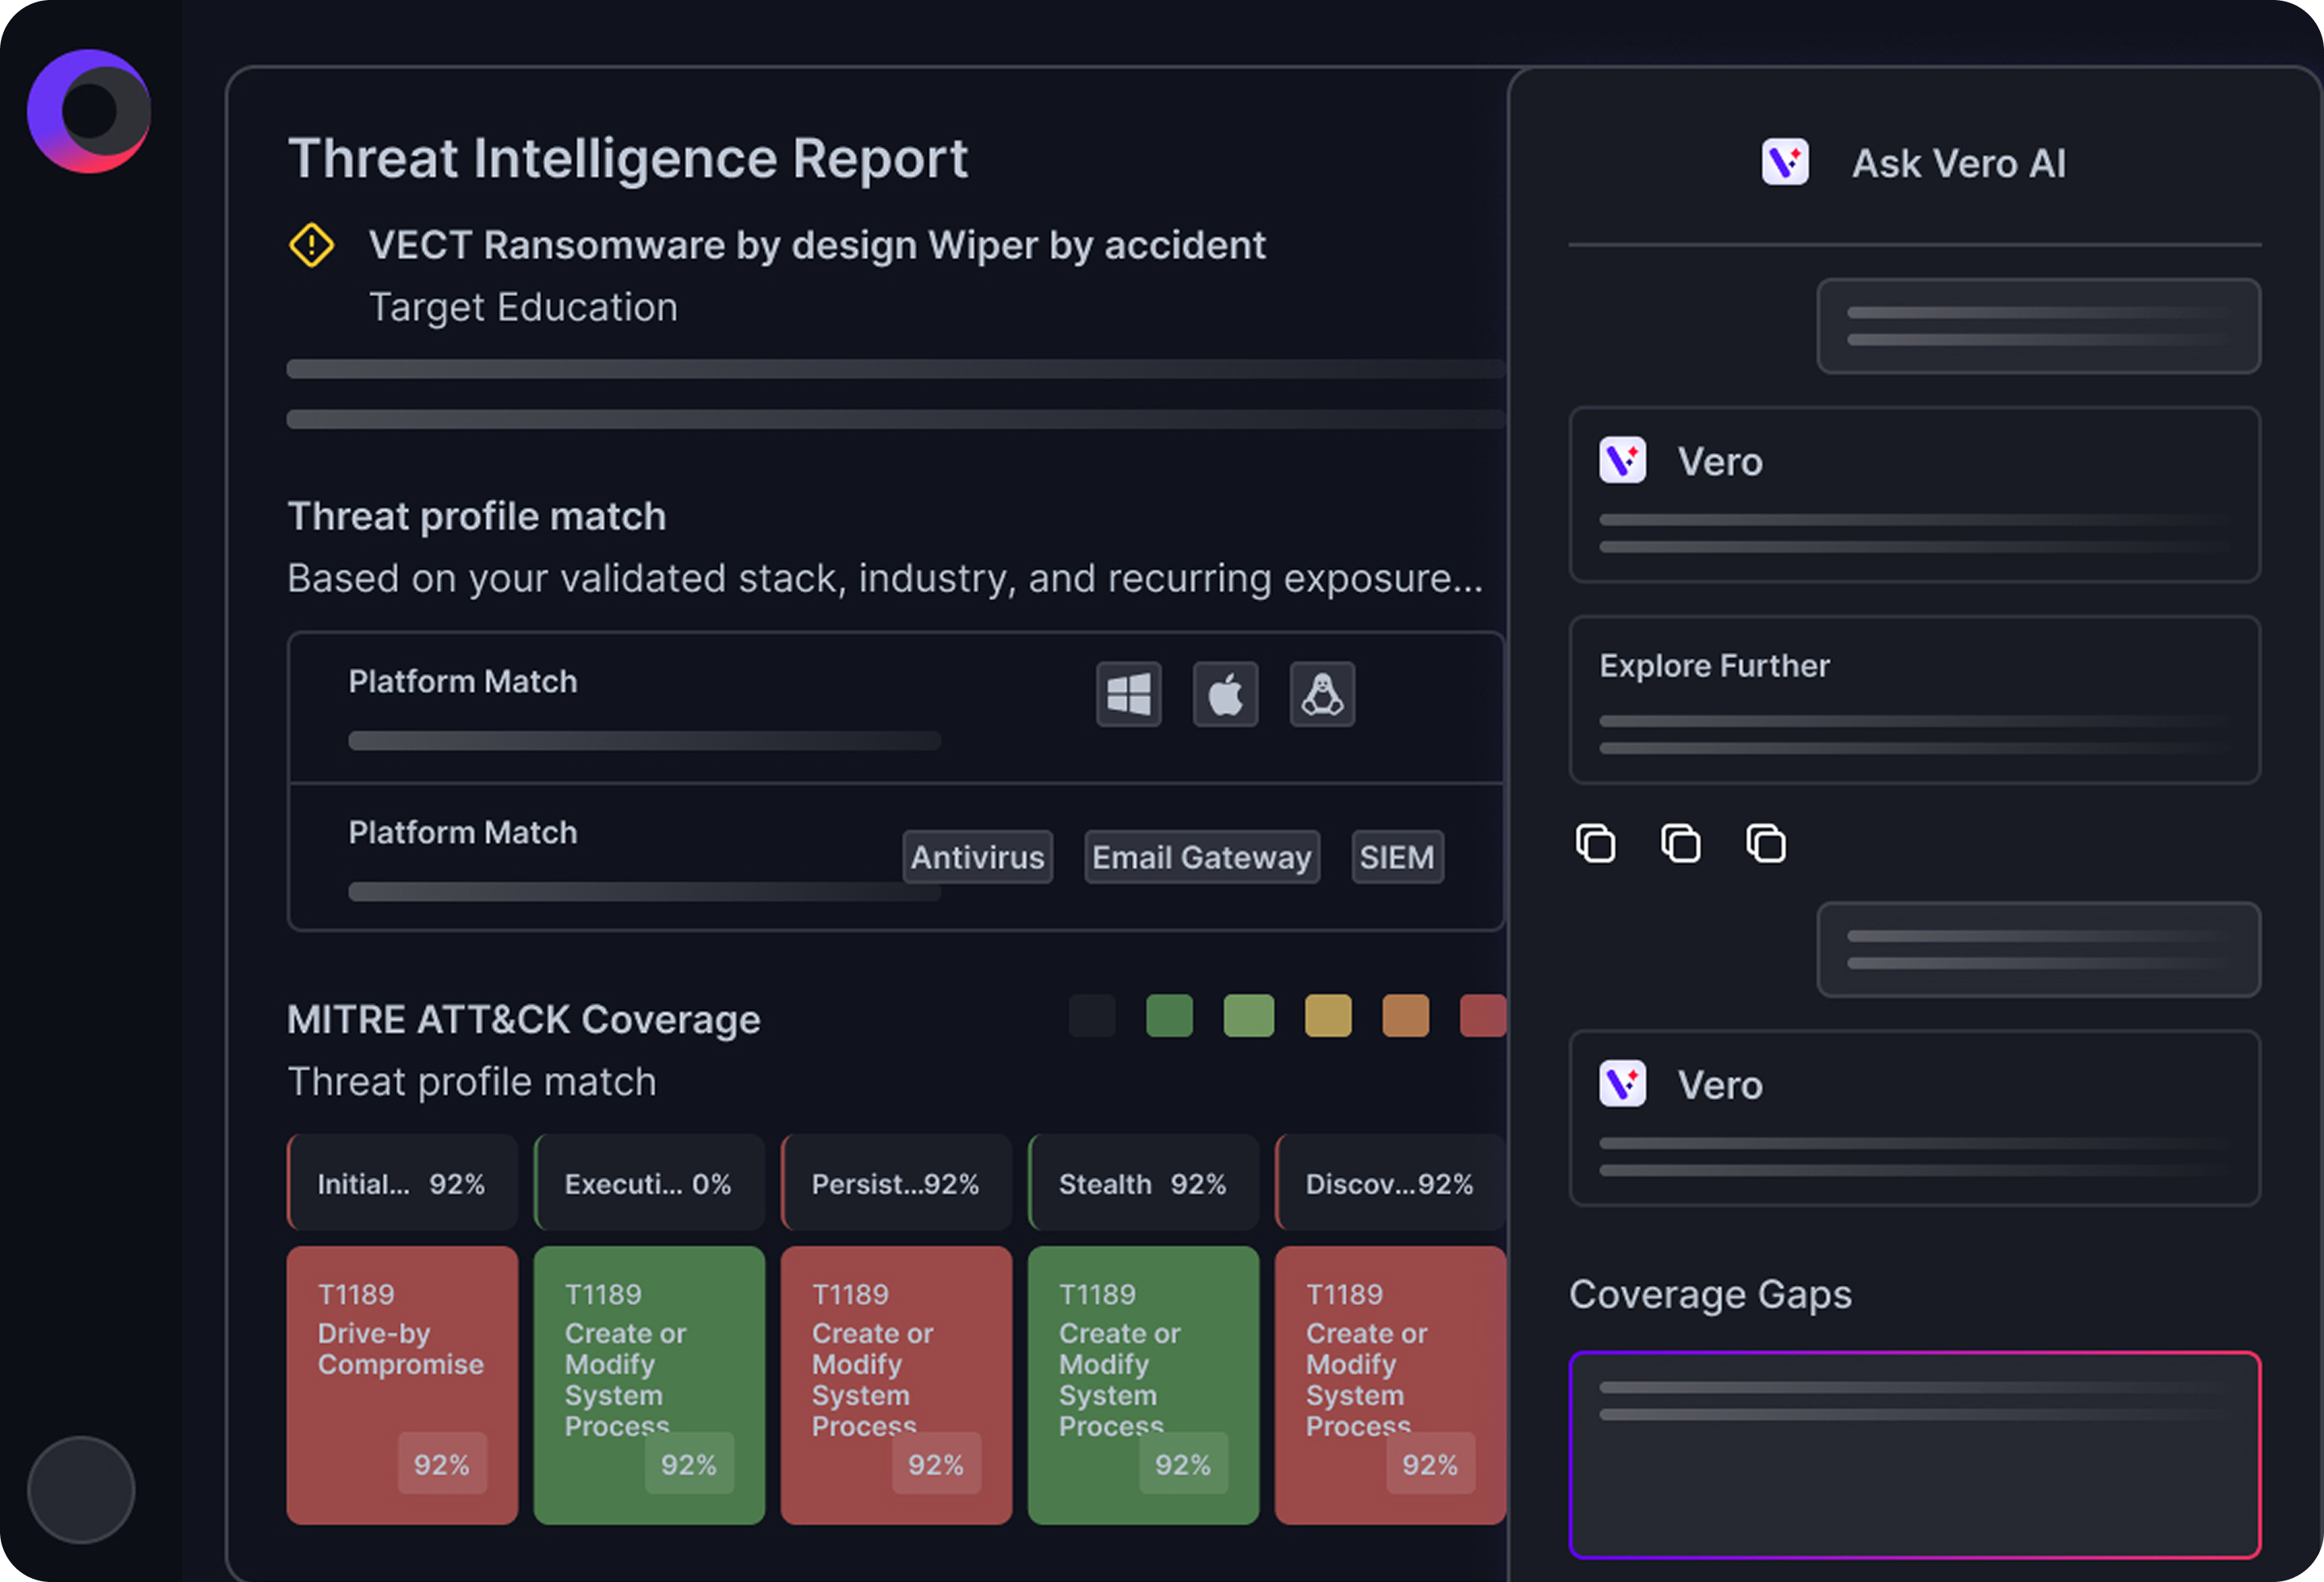
Cymulate uses Vero AI to personalize validation scenarios based on your assets, exposures, security controls, and telemetry sources. This ensures that testing is relevant to your unique environment and adapts as your infrastructure or threat landscape changes. Note: AI-driven scenario generation may require initial configuration and tuning for optimal results.
Features & Capabilities
What are the key features and benefits of Cymulate's security control validation and optimization?
Cymulate offers continuous, production-safe validation of security controls, automated mitigation and tuning, prioritized remediation guidance, and closed-loop retesting. Key benefits include up to 90% threat prevention with existing controls (average of Cymulate customers), 40 hours saved per quarter on control testing, and up to 81% improvement in security risk score within four months (as reported by a transportation customer). Note: Results may vary based on environment complexity and baseline maturity.
How does Cymulate help optimize existing security controls like SIEM, EDR, WAF, and firewalls?
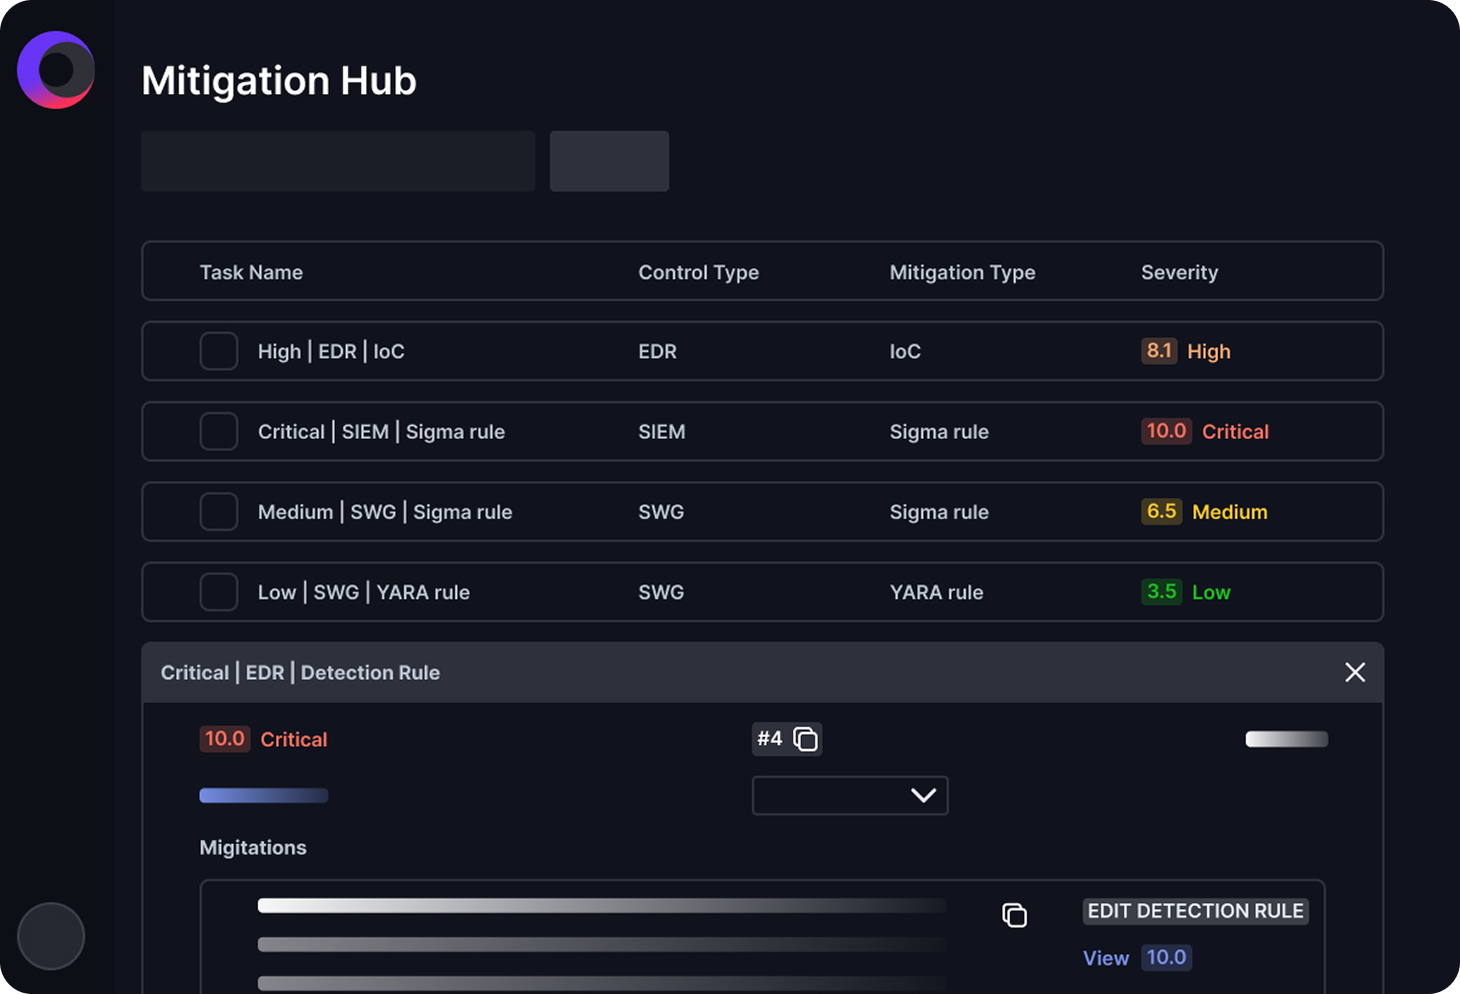
Cymulate continuously tests and validates controls such as SIEM, EDR, WAF, email gateways, secure web gateways, network IPS, and firewalls. After identifying security gaps, the platform provides actionable, vendor-specific remediation guidance and can automate updates via its Auto Mitigation feature. This accelerates the process of strengthening defenses and reduces manual effort. Note: Automated mitigation is available for supported integrations; manual steps may be required for others.
How often should security controls be validated?
Security controls should be validated continuously, not just during annual assessments or after major incidents. Continuous validation helps detect emerging gaps, verify that configuration changes have not weakened defenses, and ensure protection against the latest attack techniques. While periodic penetration tests and compliance assessments are still common, leading organizations supplement these with automated, ongoing validation. Note: Resource constraints may limit the frequency of some validation activities.
What integrations does Cymulate support for security control validation?
Cymulate supports over 50 integrations across SIEM (e.g., CrowdStrike Falcon LogScale), EDR (CrowdStrike Falcon, Carbon Black EDR, Cisco Secure Endpoint), cloud security (AWS GuardDuty, Check Point CloudGuard), web gateways (Cisco Umbrella), vulnerability management (Rapid7 InsightVM), SOAR, Active Directory, and ticketing systems. For a detailed list, visit Cymulate's technology alliances and integrations page. Note: Integration availability may depend on your specific environment and licensing.
Business Impact & Use Cases
What measurable outcomes have Cymulate customers achieved with security control validation?
Cymulate customers report an average of 90% threat prevention with existing controls, 40 hours saved per quarter on testing, and up to 81% improvement in security risk score within four months (as seen in a transportation sector case study). A global retailer achieved a 12x faster security control assessment process. For more details, see the retail case study. Note: Outcomes depend on baseline maturity and implementation scope.
Who can benefit from Cymulate's security control validation and optimization?
Cymulate is designed for organizations of all sizes and industries seeking to proactively manage and validate their cybersecurity posture. Key roles include CISOs, SecOps leaders, detection engineers, red teams, vulnerability management teams, GRC/compliance teams, and IT/cloud teams. The platform provides measurable risk reduction, actionable guidance, and evidence for compliance. Note: Organizations with highly specialized or legacy environments may require additional customization.
Security & Compliance
What security and compliance certifications does Cymulate hold?
Cymulate holds SOC2 Type II, ISO 27001:2013, ISO 27701, ISO 27017, and CSA STAR Level 1 certifications. The platform leverages AWS data centers certified for ISO 27001:2022, PCI DSS Service Provider Level 1, and SOC 2/3 Type II. For more details, visit the security overview page. Note: Certification scope and coverage may vary; review official documentation for specifics.
How does Cymulate protect customer data and support compliance?
Cymulate enforces 2-Factor Authentication (2FA) for all employees and offers it to customers, uses role-based access controls (RBAC), and encrypts all data in transit and at rest. The platform provides end-to-end visibility, continuous testing reports, and evidence for regulatory compliance (e.g., GDPR, PCI DSS). For privacy details, see the privacy policy. Note: Customers are responsible for configuring access controls and reviewing compliance evidence as needed.
Implementation & Ease of Use
How long does it take to implement Cymulate and start validating controls?
Cymulate is built for quick deployment, with an agentless mode that requires no additional hardware or complex configuration. Customers can start running simulations almost immediately after setup. User feedback highlights the platform's intuitive dashboard and ease of use, with practical insights available after just a few clicks. Note: Large or highly segmented environments may require additional onboarding time.
What support and resources are available for Cymulate users?
Cymulate provides email and chat support, webinars, e-books, a knowledge base, solution briefs, and technical documentation. Key resources include the Resource Hub, the Control Validation and Optimization Solution Brief, and the Security Validation Best Practices e-book. Note: Some resources may require registration or a customer account.
Pricing & Plans
How is Cymulate priced for security control validation and optimization?
Cymulate operates on a subscription-based pricing model tailored to each organization's needs. Pricing is determined by the package selected, number of assets, and scenarios chosen. For a detailed quote, you can schedule a demo with the Cymulate team. Note: Exact pricing is not publicly listed and may vary based on requirements.
Competition & Comparison
How does Cymulate's security control validation compare to AttackIQ?
Cymulate offers an expansive adversary simulation library with daily updates, AI-driven remediation guidance, and faster deployment compared to AttackIQ. Cymulate's AI Copilot converts threat intelligence into automated tests, and the platform covers pre- and post-exploitation scenarios, including cloud environments. AttackIQ has a more limited attack library and less frequent updates. Choose Cymulate for rapid, AI-powered validation and remediation; choose AttackIQ if you require a specific legacy integration not covered by Cymulate. Note: Cymulate may require additional configuration for highly customized environments. Read more
How does Cymulate's security control validation differ from Mandiant Security Validation?
Cymulate emphasizes continuous innovation, AI and automation, and a broader approach to exposure validation. Mandiant Security Validation has seen less innovation in recent years and focuses on traditional validation methods. Cymulate is expanding into exposure management and provides modern, automated validation. Choose Cymulate for AI-driven, continuous validation; choose Mandiant if you require legacy validation workflows. Note: Cymulate may not support all legacy Mandiant integrations. Read more