

Cybersecurity Testing: 6 Security Testing Methods Compared
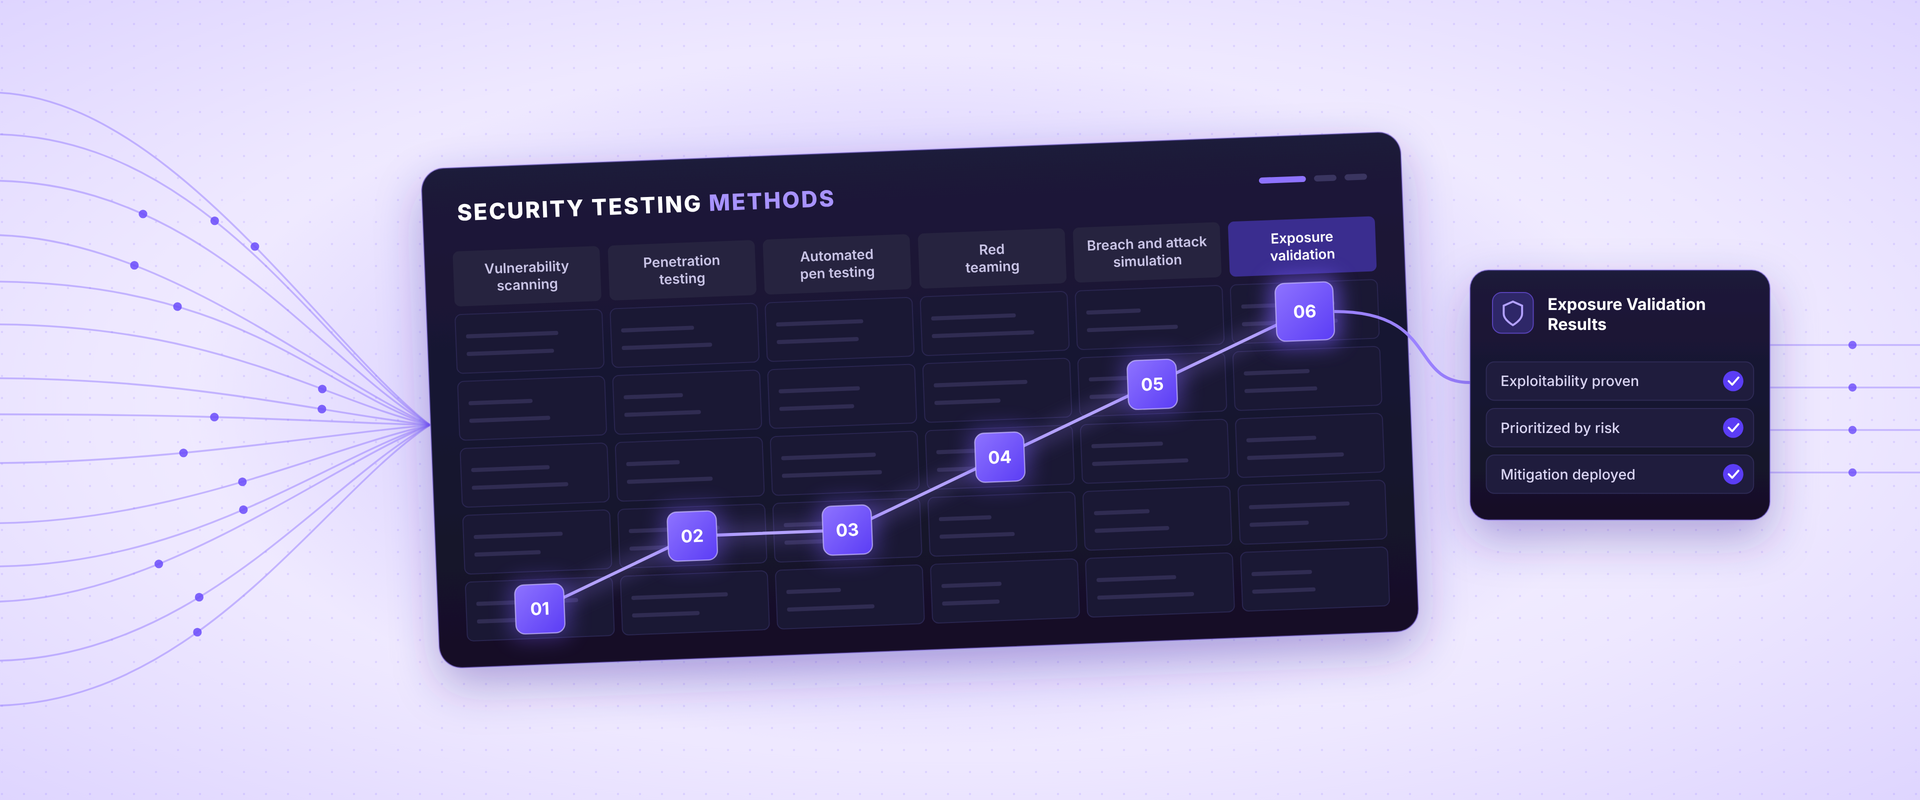
Cybersecurity testing (or security testing) is how security teams check whether their defenses would stop a real attack. The main types of security testing are vulnerability scanning, penetration testing, automated penetration testing, red teaming, breach and attack simulation (BAS) and exposure validation. These methods differ in what they prove, how often they run and how much expertise they need.
No single method answers every question. A scanner tells you a weakness exists. A pen tester tells you whether someone can exploit it. Exposure validation tells you whether your security controls stop the attack today, and what to change if they don't. This guide compares each method and shows how they fit into one program.
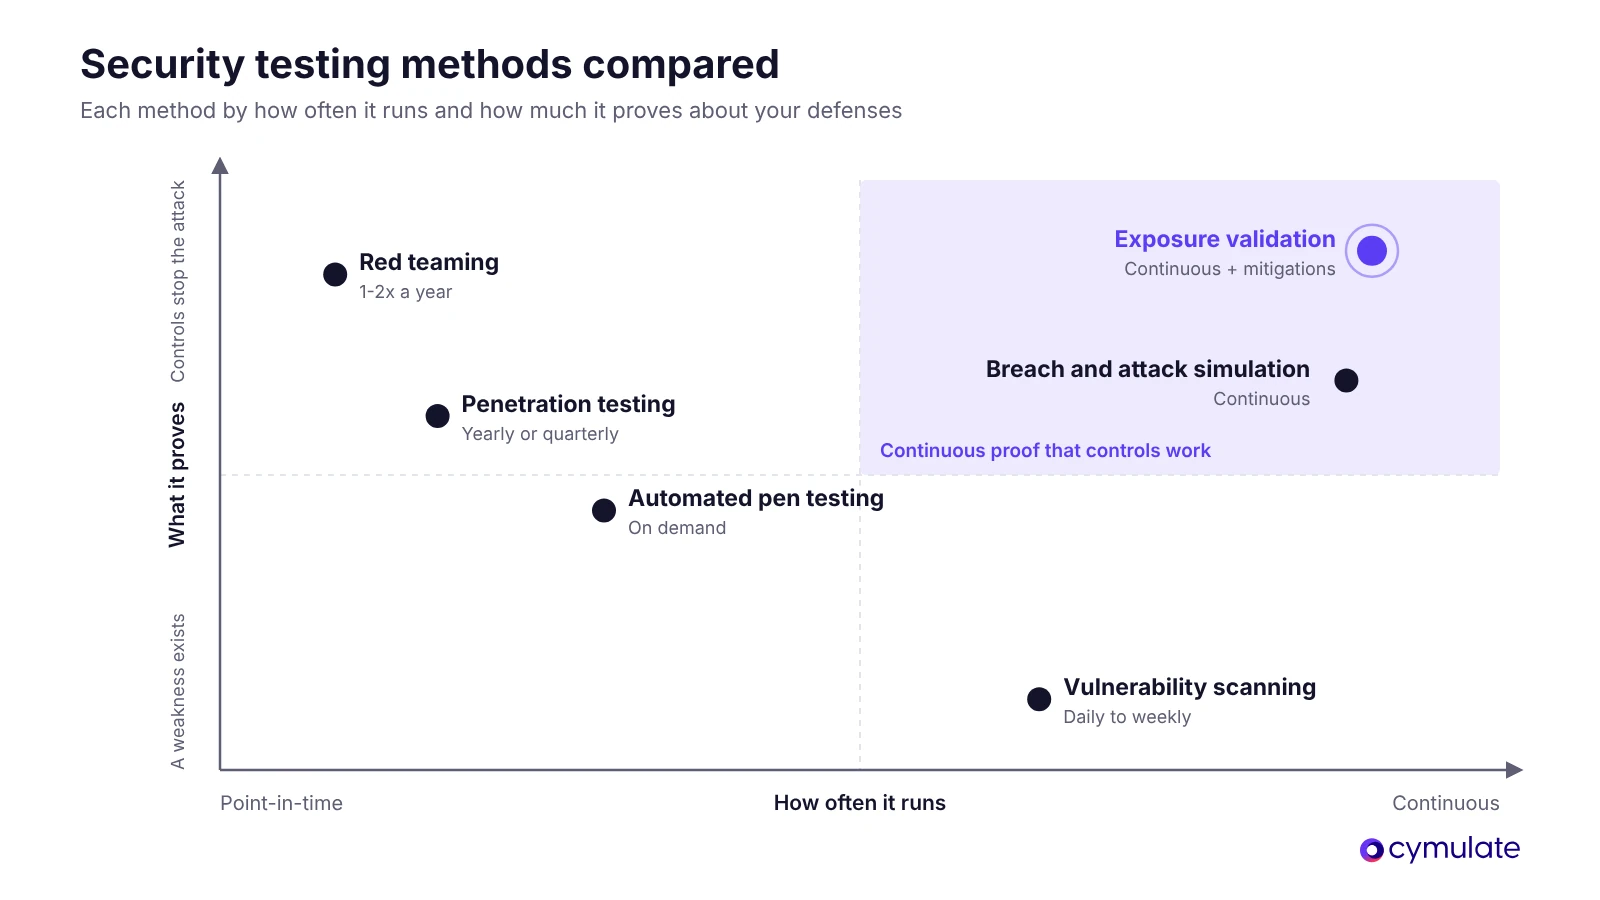
Types of cybersecurity testing at a glance
| Method | Question it answers | How often it runs | Who runs it | Main limitation |
| Vulnerability scanning | Which known weaknesses exist on my assets? | Daily to weekly | IT and vulnerability management teams | Doesn't prove exploitability |
| Penetration testing | Can a skilled tester break in, and how far can they get? | Yearly or quarterly | Internal or third-party testers | Point-in-time, scoped |
| Automated penetration testing | Which attack paths work across my network? | On demand | Security teams | Focuses on paths, not on every control |
| Red teaming | Can we detect and respond to a realistic adversary? | Once or twice a year | Red team vs. blue team | Resource-intensive |
| Breach and attack simulation | Do my controls block and detect known attack techniques? | Continuous | SecOps teams | Results need a process to act on them |
| Exposure validation | Which exposures are exploitable here, and how do I fix them? | Continuous | SecOps, red and blue teams | Needs integration with the security stack |
Vulnerability scanning
Vulnerability scanning uses automated tools to check networks, hosts and applications for known weaknesses, such as missing patches and misconfigurations. Scanning is fast, can be scheduled and covers a large number of assets.
A scanner reports potential vulnerabilities without proving whether they're exploitable in your environment. Teams can spend time patching findings that pose little real risk while exploitable ones wait in the queue. Learn how vulnerability scanning works and how it compares with penetration testing.
Best for: broad, frequent discovery of known weaknesses and meeting scanning requirements such as PCI DSS.
Penetration testing
Penetration testing (pen testing) uses skilled testers to exploit weaknesses the way an attacker would, then report how far they got. A pen test shows real impact and finds issues that scanners miss, such as chained misconfigurations.
Pen testing is scoped and point-in-time, and results depend on the tester. The report often arrives weeks later, describing defenses that may have already changed. Many organizations run pen tests yearly or quarterly to meet compliance requirements. Read more about penetration testing and the types of penetration testing.
Best for: expert depth on a critical application or network segment, and compliance-driven tests.
Automated penetration testing
Automated penetration testing uses software to run pen testing steps, such as discovery, credential use and lateral movement, without a human tester for each run. It lets teams test attack paths more often and across more of the network.
Automated pen testing focuses on whether an attacker can move through the environment. It doesn't test every prevention and detection control against every technique. See automated penetration testing and how it compares with breach and attack simulation.
Best for: checking lateral movement and privilege escalation paths more often than a manual test allows.
Red teaming and blue teaming
Red teaming emulates a specific adversary against your people, processes and technology, often over several weeks. The blue team detects, contains and responds. Together they measure detection and response readiness, not only whether weaknesses exist.
Red team exercises need experienced staff and planning, so most organizations run them once or twice a year. Compare red, blue and purple teams and red teaming vs. pen testing.
Best for: measuring how well the security operations center (SOC) detects, contains and responds to a targeted attack.
Breach and attack simulation
Breach and attack simulation (BAS) continuously runs safe, simulated attacks against your security controls, such as email and web gateways, endpoint detection and response (EDR) and your security information and event management (SIEM). It shows which techniques your controls block and detect, mapped to the MITRE ATT&CK® Framework.
BAS answers "do my controls work?" at scale. On its own, it leaves teams to decide what to fix first and how. Learn more about breach and attack simulation. Gartner now groups BAS and automated pen testing under adversarial exposure validation (AEV). See the 2026 Gartner Market Guide for Adversarial Exposure Validation.
Best for: daily proof that prevention and detection controls stop current threats.
Exposure validation: prove, prioritize and adapt
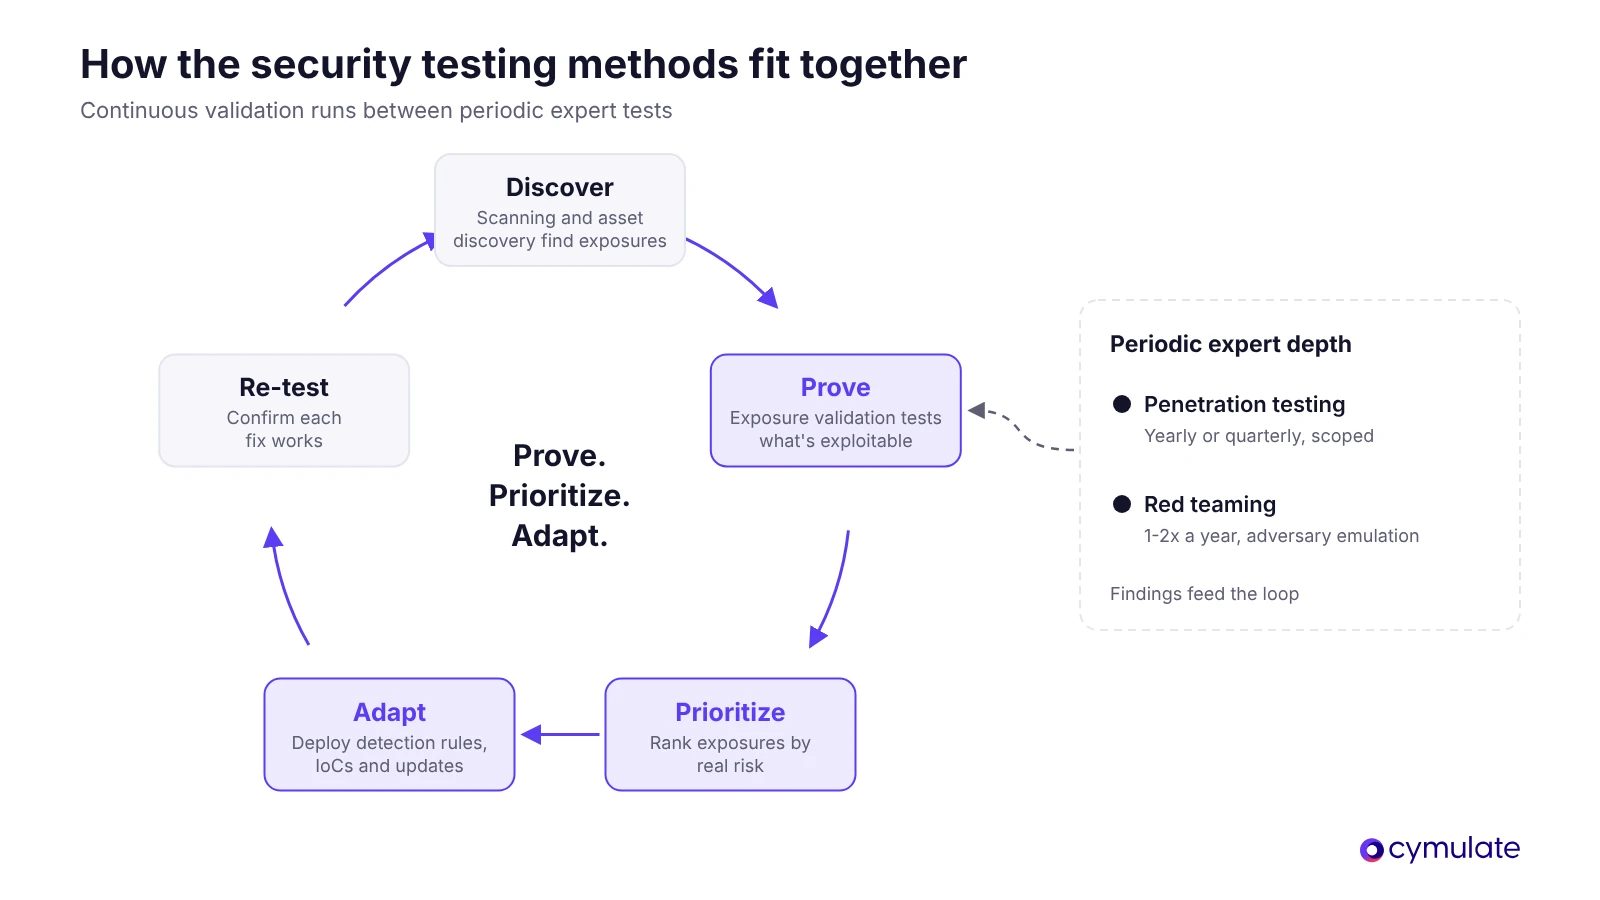
Exposure validation extends BAS from testing into action. It proves which exposures are exploitable in your environment, prioritizes them by real risk and adapts your defenses with the mitigations to close them. Then it re-tests.
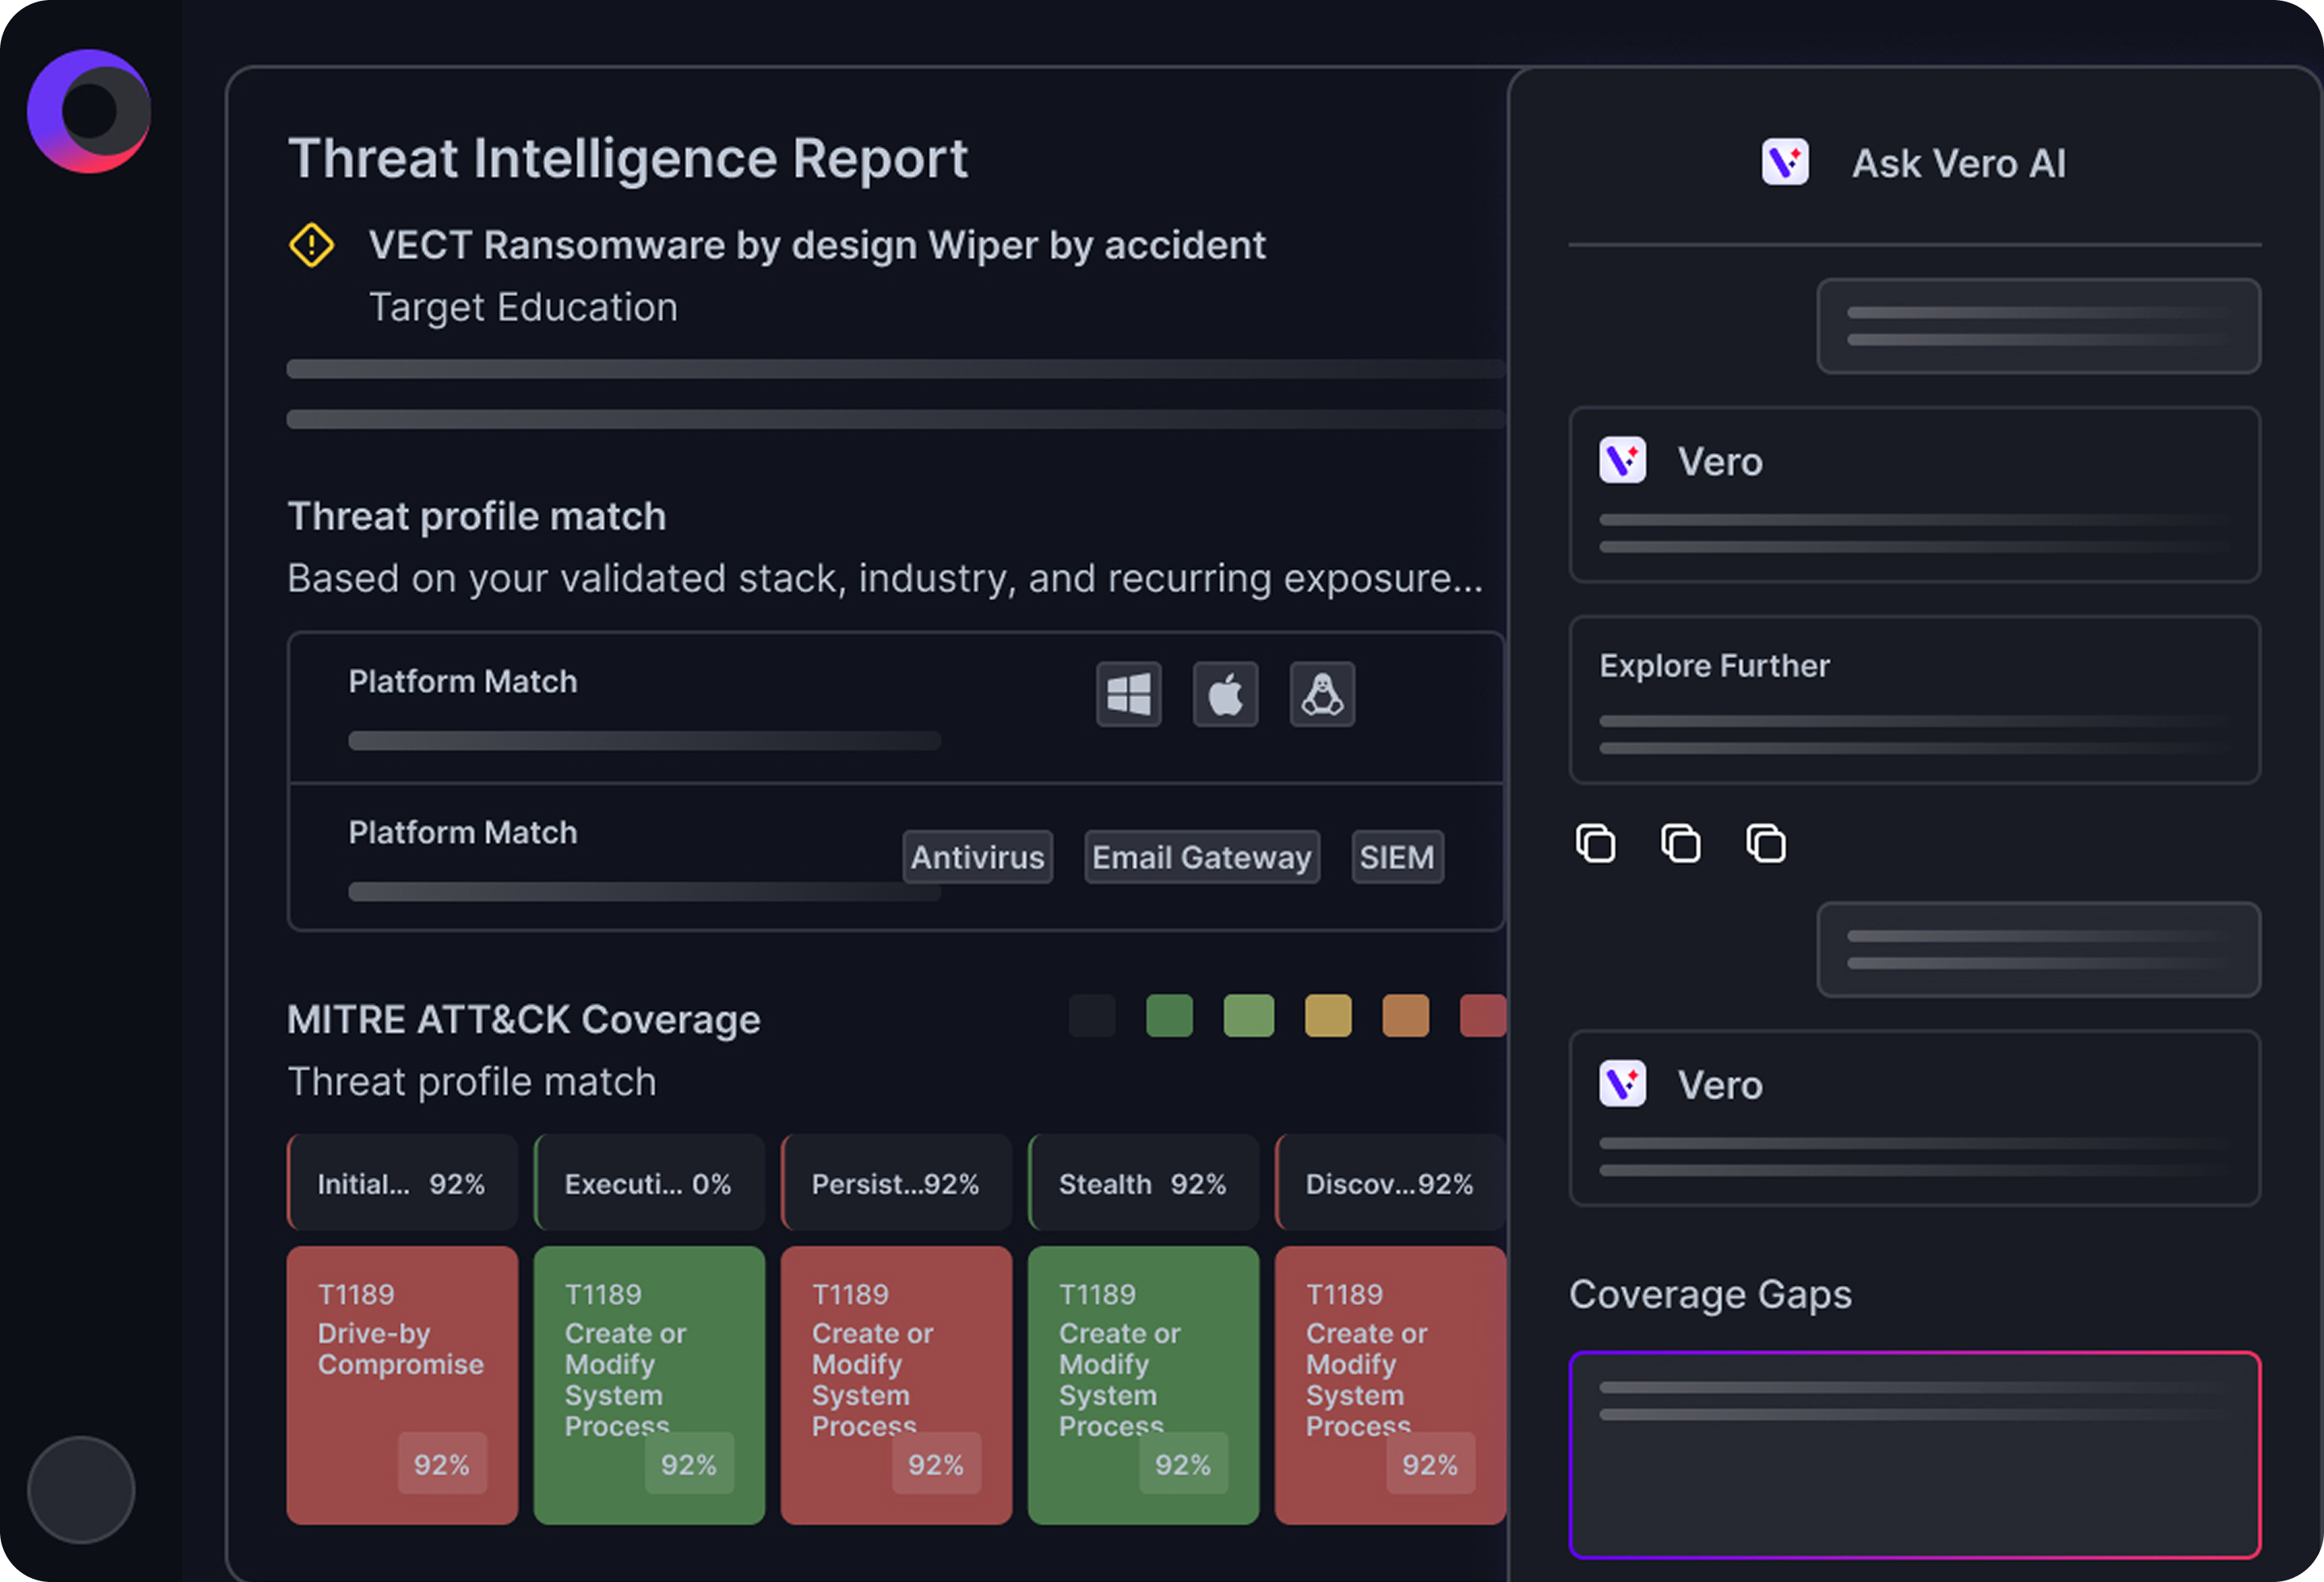
Cymulate Exposure Validation provides autonomous threat validation and cyber defense engineering that proves the state of your security and updates your security controls based on your real-world exposure. With a daily feed of new threats and the most complete attack library, Cymulate continuously tests your security controls against advanced threats and MITRE ATT&CK techniques. It integrates with security controls to understand their response and builds vendor-specific mitigations in the form of detection rules, IoCs and recommended updates. Cymulate Auto Mitigation can deploy those updates to your controls.
The same platform supports each team:
- Red teams use Cymulate Threat Studio to build multi-stage attack chains and save them as reusable templates.
- Detection engineers use Cymulate Detection Studio to map SIEM rules to attack scenarios, benchmark MITRE ATT&CK coverage per rule and get vendor-specific rule recommendations.
- Vulnerability management teams use Cymulate CTEM to test scanner findings for real exploitability, then mobilize the threat updates and detection rules that mitigate them.
On average, Cymulate customers improve threat prevention from about 70% to more than 90%, as measured by Cymulate best practices assessments.
How cybersecurity testing works
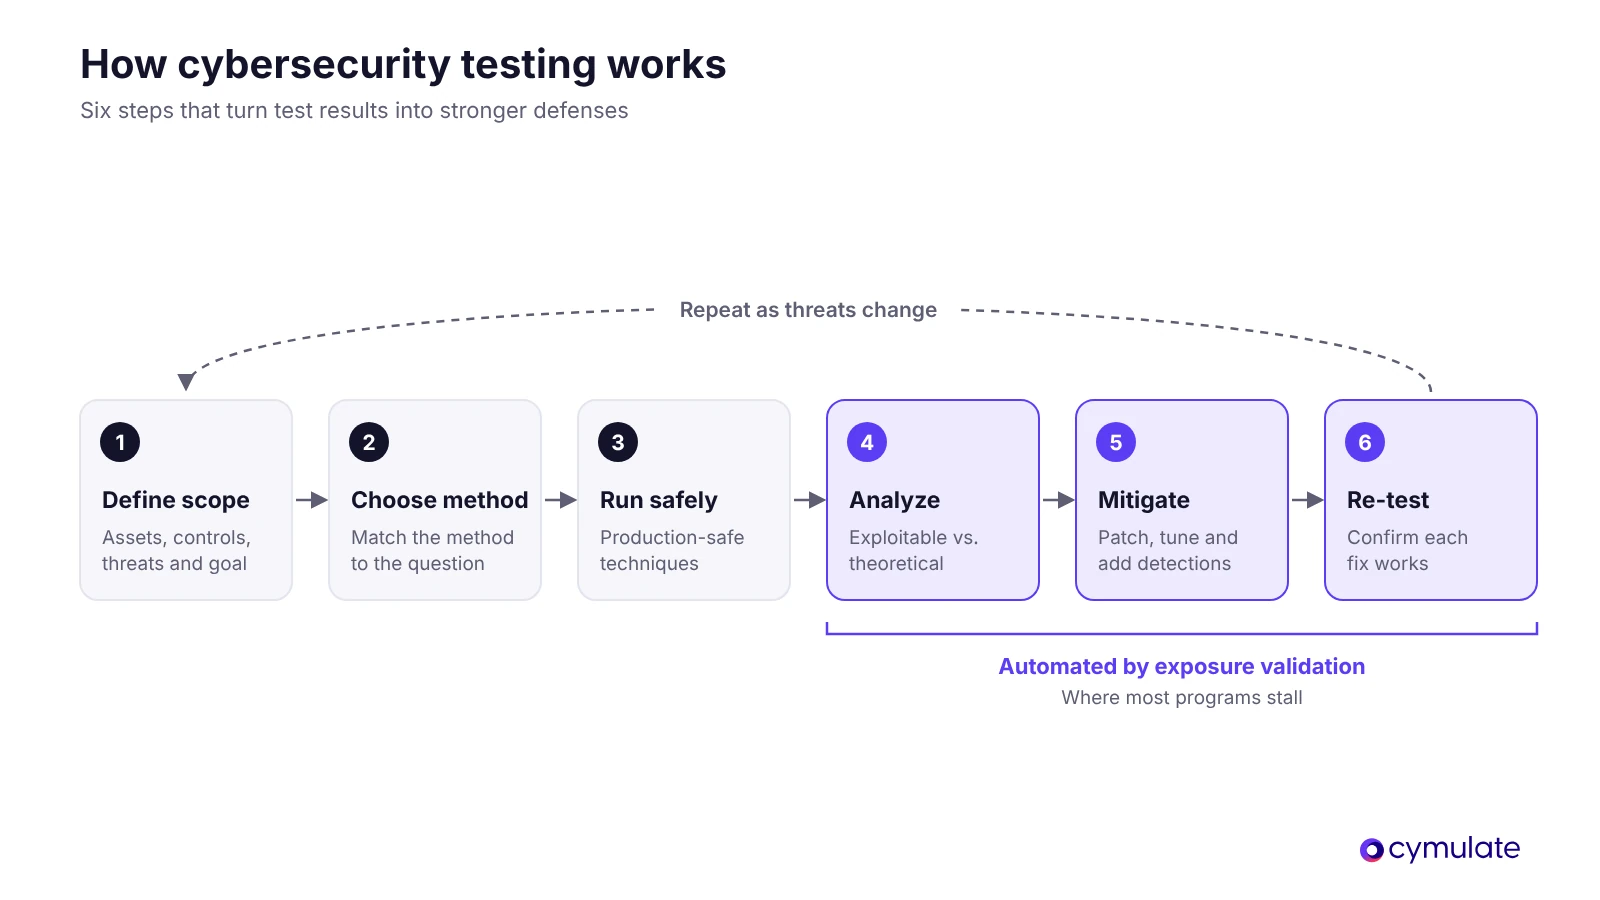
Cybersecurity testing works best as a repeatable cycle rather than a one-off project. Whatever the method, the same six steps turn test results into stronger defenses.
- Define the scope and goal. Decide which assets, controls and threats to test, and what question the test must answer. A compliance pen test and a ransomware readiness check need different scopes.
- Choose the method. Match the method to the question, using the table above. Many programs pair a continuous method with periodic expert tests.
- Run the test safely. Use production-safe techniques, agree on testing windows and tell the teams that could see alerts.
- Analyze the results. Separate exploitable exposures from theoretical ones and map findings to the MITRE ATT&CK techniques they involve.
- Mitigate. Patch, reconfigure or tune controls. Add the detection rules and IoCs that close each validated gap.
- Re-test. Run the same test again to confirm each fix works. Without this step, teams can't tell whether a gap is closed.
Steps 4 to 6 are where most programs stall. Exposure validation automates them, so each validated gap gets a fix and a re-test without waiting for the next scheduled test.
How to choose a security testing method
Pick the method by the question you need answered:
- Find known weaknesses across all assets: vulnerability scanning.
- Meet a compliance requirement for an expert test: penetration testing.
- Check which attack paths work between tests: automated penetration testing.
- Measure detection and response against a real adversary: red teaming.
- Confirm controls block and detect current threats every day: BAS.
- Know which exposures are exploitable and get the fixes: exposure validation.
Most programs use several methods. The question is how the results connect.
Cybersecurity testing and compliance
Many regulations set a minimum security testing schedule. Treat these as the floor, not the full program.
| Framework | What it requires | Frequency |
| PCI DSS v4.0 (Req. 11.3) | Internal vulnerability scans and external scans by an Approved Scanning Vendor | At least once every three months and after significant changes |
| PCI DSS v4.0 (Req. 11.4) | Internal and external penetration testing | At least once every 12 months and after significant changes |
| DORA (Article 26) | Threat-led penetration testing (TLPT) for financial entities identified by their regulator | At least every three years |
| NIST SP 800-115 | Guidance on planning, running and reporting technical security tests | No set frequency |
A yearly pen test meets the PCI DSS requirement, but new threats appear every day. Continuous validation between tests shows whether controls still work and creates evidence auditors can review. See how security validation supports NIS2 compliance.
How the methods fit together
In a continuous threat exposure management (CTEM) program, scanning and asset discovery find exposures. Pen testing and red teaming add expert depth at set points in the year. Exposure validation runs between them: it proves what's exploitable, prioritizes it and adapts defenses, then re-tests to confirm the fix. Read more about continuous threat exposure management and how to build a security testing plan.
Common cybersecurity testing mistakes
- Treating a scan report as a risk list. Unvalidated findings bury the exploitable ones. Validate before you prioritize.
- Testing once a year and calling it done. Controls drift as rules, agents and policies change. Validate between expert tests.
- Testing only for vulnerabilities. A patched system can still sit behind a misconfigured EDR or a SIEM rule that never fires. Test the controls too.
- Stopping at the findings. A finding without a mitigation is a ticket that waits. Pair every gap with the fix and an owner.
- Skipping the re-test. Re-run the test after each fix to prove the gap is closed.
Frequently Asked Questions
Cybersecurity testing is the practice of checking whether an organization’s systems and security controls can withstand real attacks. It ranges from automated vulnerability scans to expert-led pen tests and continuous exposure validation.
The main methods are vulnerability scanning, penetration testing, automated penetration testing, red teaming, breach and attack simulation and exposure validation. Each answers a different question, from “which weaknesses exist” to “do my controls stop this attack.”
Vulnerability scanning automatically lists known weaknesses. Penetration testing uses a skilled tester to exploit them and show real impact. See the full comparison.
Security testing is the umbrella term for every method that checks your defenses. Penetration testing is one type of security testing, where a skilled tester exploits weaknesses in a scoped target. Learn more about penetration testing
Run vulnerability scans and control validation continuously or weekly, and pen tests and red team exercises at least once a year or after major changes. New threats appear daily, so continuous validation closes the gap between expert tests.
No. BAS and exposure validation test controls continuously at scale, while pen testers bring creativity and depth to a scoped target. Most teams use both and use validation results to focus their pen tests.
Teams use vulnerability scanners for discovery, pen testing frameworks for manual testing, and BAS or exposure validation platforms for continuous control testing. Many also map results to the MITRE ATT&CK Framework to compare coverage across tools.
Featured Resources
View More Resources
One Image to Remote Code Execution: The Critical Pillow Zero-Day Our AI Benchmark Found by Accident (CVE-2026-96639)
A critical Pillow zero-day allows crafted images to trigger remote code execution, exposing servers and AI environments.
Triangle InfoSeCon Panel Recap: How Security Leaders Prove Defenses, Respond to Breaches and Recover
Security leaders at Triangle InfoSeCon on proving controls to the board, preparing for breaches and recovering faster.
Across the Kill Chain: How Agents Became the Enterprise's New Front Door
See how attackers chain AI agent vulnerabilities to compromise cloud identities and how security teams can disrupt attacks.