Frequently Asked Questions

Continuous Security Validation Fundamentals

What is continuous security validation?

Continuous security validation is a proactive cybersecurity approach that consistently verifies whether a company's security controls are working as effectively as possible. Unlike traditional point-in-time assessments, it involves ongoing, automated testing to identify weaknesses before attackers can exploit them. This method uses real-world attack simulations, often mapped to frameworks like MITRE ATT&CK, to ensure defenses remain resilient as environments change.

How does continuous security validation differ from traditional penetration testing?

Traditional penetration testing is typically performed once or twice a year and provides a snapshot of an organization's security posture at a single point in time. In contrast, continuous security validation is an ongoing process that persistently tests for vulnerabilities, misconfigurations, and escalation paths using automated tools. This approach ensures that security controls are always up to date and effective against the latest threats.

Why is continuous security validation important for modern organizations?

Continuous security validation is crucial because cyber threats evolve rapidly, and static defenses can quickly become outdated. By continuously testing and validating security controls, organizations can identify and remediate vulnerabilities before attackers exploit them, protect sensitive data, and maintain compliance with industry standards. This proactive approach also helps organizations adapt to changes in their IT environment and regulatory landscape.

What role does the MITRE ATT&CK Framework play in continuous security validation?

The MITRE ATT&CK Framework provides a comprehensive taxonomy of adversarial tactics and techniques used by attackers. Continuous security validation solutions, like Cymulate, map their attack simulations to the MITRE ATT&CK Framework, ensuring that organizations test their defenses against the latest real-world threats and behaviors. This alignment helps both offensive and defensive teams understand and address specific attack vectors.

How does continuous security validation help with zero-day attacks?

Continuous security validation provides organizations with a holistic view of their security posture, allowing them to identify and address vulnerabilities that could be exploited by zero-day attacks. By simulating real-world attack scenarios and continuously updating attack libraries, organizations can ensure their defenses are resilient against both known and emerging threats, including zero-days.

What are the main benefits of continuous security validation?

The main benefits include smarter budget use by identifying redundant controls, enhanced protection for customers and clients, improved brand reputation, and the ability to make data-driven decisions. Automated validation reduces reliance on costly manual testing and helps organizations stay ahead of attackers by continuously identifying and remediating vulnerabilities.

How does continuous security validation support compliance efforts?

Continuous security validation helps organizations maintain compliance with industry standards by providing ongoing evidence that security controls are effective. Automated reports and baselines make it easier to demonstrate compliance during audits and to regulators, reducing the risk of non-compliance penalties.

What types of organizations benefit most from continuous security validation?

Organizations of all sizes and industries benefit from continuous security validation, especially those handling sensitive financial, personal, or medical data. Sectors like finance, healthcare, retail, and critical infrastructure are particularly at risk and can gain significant value from proactive, automated security validation.

How does continuous security validation help protect brand reputation?

By continuously identifying and addressing vulnerabilities, organizations can reduce the likelihood of breaches and data leaks that could damage their reputation. In the event of an incident, having a robust validation program allows companies to respond quickly, communicate transparently, and demonstrate due diligence to customers and stakeholders.

What is the role of breach and attack simulation in continuous security validation?

Breach and Attack Simulation (BAS) is a core component of continuous security validation. BAS tools automate the process of emulating cybercriminal tactics in a safe, production-ready manner, running attack scenarios 24/7 to test the effectiveness of security controls across the entire attack kill chain. This ensures organizations are always prepared for the latest threats.

How does continuous security validation help with smarter budget allocation?

By automating the validation of cybersecurity performance, organizations can identify which security controls are effective, redundant, or unnecessary. This enables smarter budget allocation by eliminating waste and focusing resources on the most impactful security measures.

How does continuous security validation improve response to new threats?

Continuous security validation provides real-time insights into the effectiveness of security controls, enabling organizations to quickly identify and remediate vulnerabilities as new threats emerge. Automated attack simulations and up-to-date threat intelligence ensure defenses are always tested against the latest attack techniques.

How does continuous security validation help with lateral movement attacks?

Continuous security validation includes automated testing for lateral movement, which is when attackers move within a network to access valuable assets. By simulating these attack paths, organizations can identify and remediate weaknesses that could allow attackers to escalate privileges or move undetected within their environment.

What is attack-based patching prioritization?

Attack-based patching prioritization is a process where vulnerabilities discovered during continuous security validation are scheduled for remediation based on their exploitability and potential impact. This ensures that the most critical vulnerabilities are addressed first, reducing overall risk.

How does continuous security validation help with third-party risk?

Continuous security validation can identify vulnerabilities introduced by third-party vendors, such as misconfigured access or outdated software. By continuously testing all aspects of the environment, organizations can ensure that third-party risks are detected and mitigated promptly.

How does continuous security validation support executive decision-making?

Continuous security validation provides actionable, data-driven insights and baselines that help executives and security leaders make informed decisions about risk management, resource allocation, and security investments. These insights can be used to communicate effectively with stakeholders and justify security budgets.

How quickly can organizations see value from continuous security validation?

Organizations can see value from continuous security validation almost immediately after implementation, as automated tools begin identifying vulnerabilities and providing actionable insights right away. This rapid feedback loop enables quick remediation and ongoing improvement of the security posture.

How does Cymulate enable continuous security validation?

Cymulate enables continuous security validation by providing an automated platform that simulates real-world attacks, validates security controls, and delivers actionable insights. The platform integrates with existing security tools, runs 24/7 attack simulations, and provides detailed reports to help organizations optimize their defenses and reduce risk.

What is the primary purpose of Cymulate's platform?

The primary purpose of Cymulate's platform is to help organizations proactively validate their cybersecurity defenses, identify vulnerabilities, and optimize their security posture. It empowers security teams to stay ahead of emerging threats and improve overall resilience through continuous threat validation, exposure prioritization, and automation.

Features & Capabilities

What are the key features of Cymulate's platform?

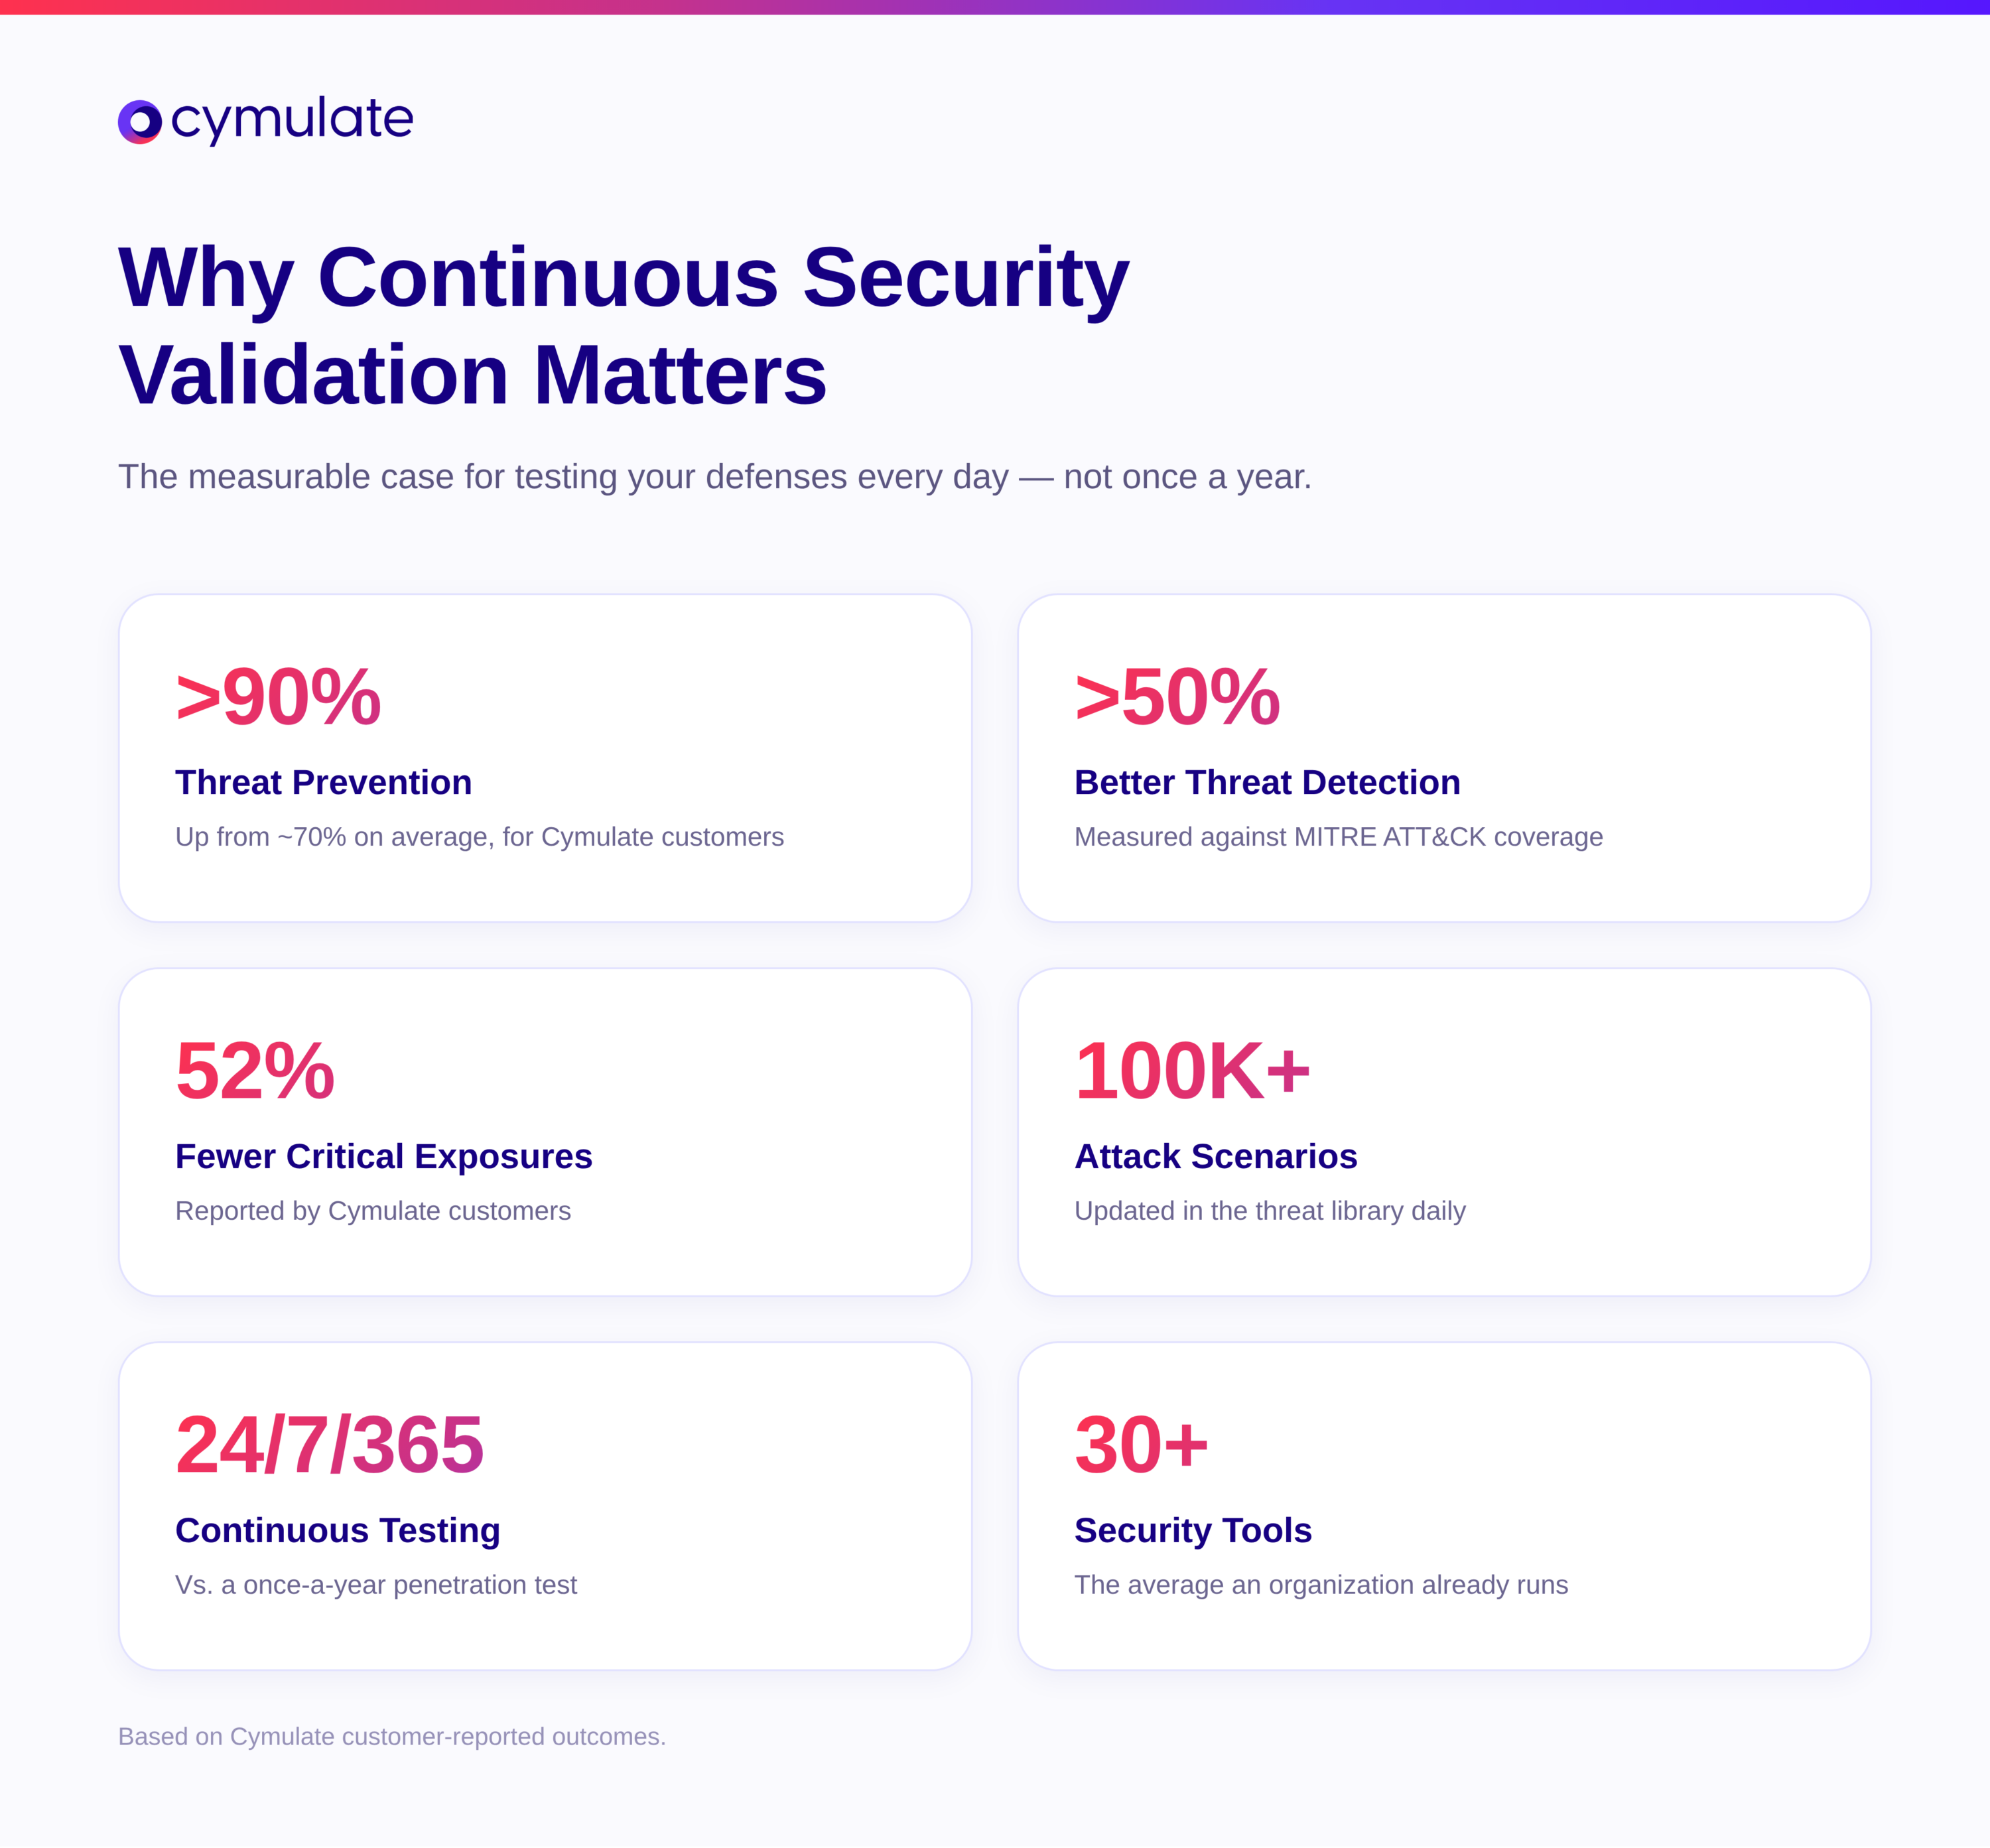
Cymulate's platform offers continuous threat validation, a unified platform combining Breach and Attack Simulation (BAS), Continuous Automated Red Teaming (CART), and Exposure Analytics, attack path discovery, automated mitigation, AI-powered optimization, complete kill chain coverage, ease of use, and an extensive threat library with over 100,000 attack actions updated daily. Learn more.

Does Cymulate integrate with other security tools?

Yes, Cymulate integrates with a wide range of security technologies, including Akamai Guardicore, AWS GuardDuty, BlackBerry Cylance OPTICS, Carbon Black EDR, Check Point CloudGuard, Cisco Secure Endpoint, CrowdStrike Falcon, Wiz, SentinelOne, and more. For a complete list, visit our Partnerships and Integrations page.

How does Cymulate use AI in its platform?

Cymulate leverages machine learning to deliver actionable insights for prioritizing remediation efforts, optimize security controls, and automate threat validation. Features like AI-powered SIEM rule mapping and advanced exposure prioritization help organizations focus on the most critical vulnerabilities.

How easy is Cymulate to implement and use?

Cymulate is designed for rapid, agentless deployment with no need for additional hardware or complex configurations. Customers can start running simulations almost immediately, and the platform is praised for its intuitive, user-friendly interface. Comprehensive support and educational resources are available to help users get started quickly.

What feedback have customers given about Cymulate's ease of use?

Customers consistently praise Cymulate for its ease of use and intuitive dashboard. Testimonials highlight the platform's user-friendly portal, excellent support, and immediate value in identifying security gaps and mitigation options. For example, Raphael Ferreira, Cybersecurity Manager, stated, "Cymulate is easy to implement and use—all you need to do is click a few buttons, and you receive a lot of practical insights into how you can improve your security posture." Read more testimonials.

What security and compliance certifications does Cymulate hold?

Cymulate holds several industry-leading certifications, including SOC2 Type II, ISO 27001:2013, ISO 27701, ISO 27017, and CSA STAR Level 1. These certifications demonstrate Cymulate's commitment to robust security, privacy, and compliance standards. Learn more.

How does Cymulate ensure data security and privacy?

Cymulate ensures data security through encryption for data in transit (TLS 1.2+) and at rest (AES-256), secure AWS-hosted data centers, a tested disaster recovery plan, and a strict Secure Development Lifecycle (SDLC). The platform also includes mandatory 2-Factor Authentication (2FA), Role-Based Access Controls (RBAC), and GDPR compliance measures.

How often is Cymulate's platform updated?

Cymulate updates its SaaS platform every two weeks, introducing new features such as AI-powered SIEM rule mapping and advanced exposure prioritization. The threat simulation library is updated daily to ensure coverage of the latest attack techniques.

Use Cases & Benefits

What business impact can customers expect from using Cymulate?

Customers can expect up to a 52% reduction in critical exposures, a 20-point improvement in threat prevention, a 60% increase in team efficiency, and an 81% reduction in cyber risk within four months. Cymulate also helps save up to 60 hours per month in testing new threats and provides actionable insights for better decision-making. Learn more.

What are common pain points Cymulate helps solve?

Cymulate addresses fragmented security tools, resource constraints, unclear risk prioritization, cloud complexity, communication barriers, inadequate threat simulation, operational inefficiencies in vulnerability management, and post-breach recovery challenges. See case studies.

Are there case studies demonstrating Cymulate's effectiveness?

Yes, for example, Hertz Israel reduced cyber risk by 81% in four months, a sustainable energy company scaled penetration testing cost-effectively, and Nemours Children's Health improved detection in hybrid and cloud environments. Read more case studies.

Who is the target audience for Cymulate?

Cymulate is designed for CISOs and security leaders, SecOps teams, Red Teams, and Vulnerability Management teams in organizations of all sizes and industries, including finance, healthcare, retail, media, transportation, and manufacturing. Learn more.

How does Cymulate address the needs of different personas?

Cymulate tailors its solutions for CISOs (metrics and risk prioritization), SecOps (automation and efficiency), Red Teams (automated offensive testing), and Vulnerability Management teams (in-house validation and prioritization). Each persona receives tools and insights relevant to their role. Learn more.

Competition & Comparison

How does Cymulate compare to other security validation platforms?

Cymulate stands out with its unified platform combining BAS, CART, and Exposure Analytics, continuous 24/7 validation, AI-powered optimization, complete kill chain coverage, ease of use, and rapid innovation. Customers report measurable outcomes such as a 52% reduction in critical exposures and an 81% reduction in cyber risk. See comparisons.

What makes Cymulate different from traditional security validation tools?

Unlike traditional tools that rely on point-in-time assessments, Cymulate offers continuous, automated attack simulations, a unified platform, AI-driven insights, and daily updates to its threat library. This approach provides real-time validation and actionable recommendations, reducing complexity and improving efficiency.

Pricing & Plans

What is Cymulate's pricing model?

Cymulate operates on a subscription-based pricing model tailored to each organization's requirements. Pricing depends on the chosen package, number of assets, and scenarios selected. For a detailed quote, schedule a demo with the Cymulate team.

Support & Implementation

What support options are available for Cymulate customers?

Cymulate offers email support, real-time chat support, a knowledge base with technical articles and videos, webinars, e-books, and an AI chatbot for quick answers. Customers can reach support at [email protected] or via chat support.

How long does it take to implement Cymulate?

Cymulate is designed for rapid deployment, often allowing organizations to start running simulations almost immediately. The agentless mode eliminates the need for additional hardware or complex setup, and comprehensive support resources are available to assist with onboarding.

Resources & Company Information

Where can I find Cymulate's blog, newsroom, and events?

You can stay updated on the latest threats, research, and company news through Cymulate's blog, newsroom, and events & webinars pages.

Does Cymulate offer a resource hub for insights and product information?

Yes, Cymulate's Resource Hub provides a central location for insights, thought leadership, and product information.

What is Cymulate's mission and vision?

Cymulate's mission is to transform cybersecurity practices by enabling organizations to proactively validate their defenses, identify vulnerabilities, and optimize their security posture. The vision is to create a collaborative environment where organizations can achieve lasting improvements in cybersecurity. Learn more.

What is Cymulate's track record for innovation and customer success?

Cymulate is recognized as a market leader in automated security validation, with frequent platform updates and proven customer outcomes such as an 81% reduction in cyber risk for Hertz Israel within four months. See more success stories.

Cymulate named a Customers' Choice in 2026 Gartner® Peer Insights™
Learn More
New: Cymulate Cowork for Agentic Cyber Defense Engineering
Learn More
New Bitsight Integration: Turn Threat Intelligence into Validated Security
Learn More
Introducing Cymulate Vero AI for Agentic Cyber Defense Engineering
Learn More

What Is Continuous Security Validation?
By: Ruben Jami

Last Updated: September 8, 2026

cymulate blog article

Continuous security validation (CSV) is the practice of automatically and repeatedly testing your security controls against real-world attack techniques, instead of once a year, so you always know which defenses actually work, not just which ones you think work.

Security teams don’t lack tools; most run 30+ overlapping products already. What they lack is proof that those tools are holding up. Frontier AI is accelerating both the discovery of new vulnerabilities and the speed at which attackers weaponize them, which means a control validated in January can be meaningfully weaker by September without anyone touching a configuration. Add in constant security drift, new cloud workloads, credential changes, third-party integrations, and the gap between “we bought the control” and “the control still works” only widens.

Continuous security validation closes that gap. It’s the discipline, and increasingly the Gartner-recognized market category, behind proving your defenses hold up against current, real attacker behavior every day, not just on audit day. It also helps teams build exposure-informed defenses instead of hoping last quarter’s pen test still holds.

Continuous Security Validation: The Definition, In Plain Terms

Continuous security validation is an automated, ongoing process of testing whether your already-deployed security controls, such as firewalls, EDR, email gateways, WAFs, SIEM detections, and more, actually stop real attack techniques in your specific environment.

It replaces (or, more often, supplements) point-in-time assessments like annual penetration tests or one-off red team engagements with a persistent, offensive testing loop that runs safely in production. Instead of asking “did we pass an audit six months ago?” it answers “would this control stop today’s attack?” and, in a mature program, immediately closes the risk-to-fix gap by turning that answer into an actual control update.

Gartner now groups this category of tooling, automated, adversarial testing of security controls at scale, under Adversarial Exposure Validation (AEV). If you’ve seen that term in a Gartner Market Guide, it’s describing the same underlying practice as continuous security validation; AEV is the analyst-defined market category, CSV is the outcome security teams are trying to achieve. We break down that relationship, and how both connect to CTEM, later in this article.
Why Continuous Security Validation Matters Right Now

A few converging pressures are pushing continuous validation from “nice to have” to baseline expectation:

AI is accelerating both sides of the threat equation. Frontier AI models are speeding up how quickly new vulnerabilities and exposures are discovered, and how quickly attackers turn them into working exploits. Security teams can no longer assume a gap between “vulnerability disclosed” and “vulnerability exploited” measured in months; validation has to run at a comparable speed.

Security posture drifts constantly. The average organization manages 30+ distinct security controls at once. Every patch, configuration change, new cloud workload, credential rotation, or third-party integration can quietly weaken one of them, long before anyone notices.

Annual testing can’t keep pace. A control validated once a year tells you very little about your exposure the other 364 days. Threat libraries need to reflect new techniques as they emerge, not on a testing cycle.

Regulation is starting to expect it. Frameworks like PCI DSS 4.0, the EU’s DORA, and NIS2 are pushing organizations toward more frequent, evidence-based testing of security controls rather than a single annual checkbox exercise. Continuous validation gives you a running body of evidence instead of a once-a-year snapshot. (Check with your compliance team on the specifics that apply to your organization — requirements vary by framework and sector.)

How Continuous Security Validation Works

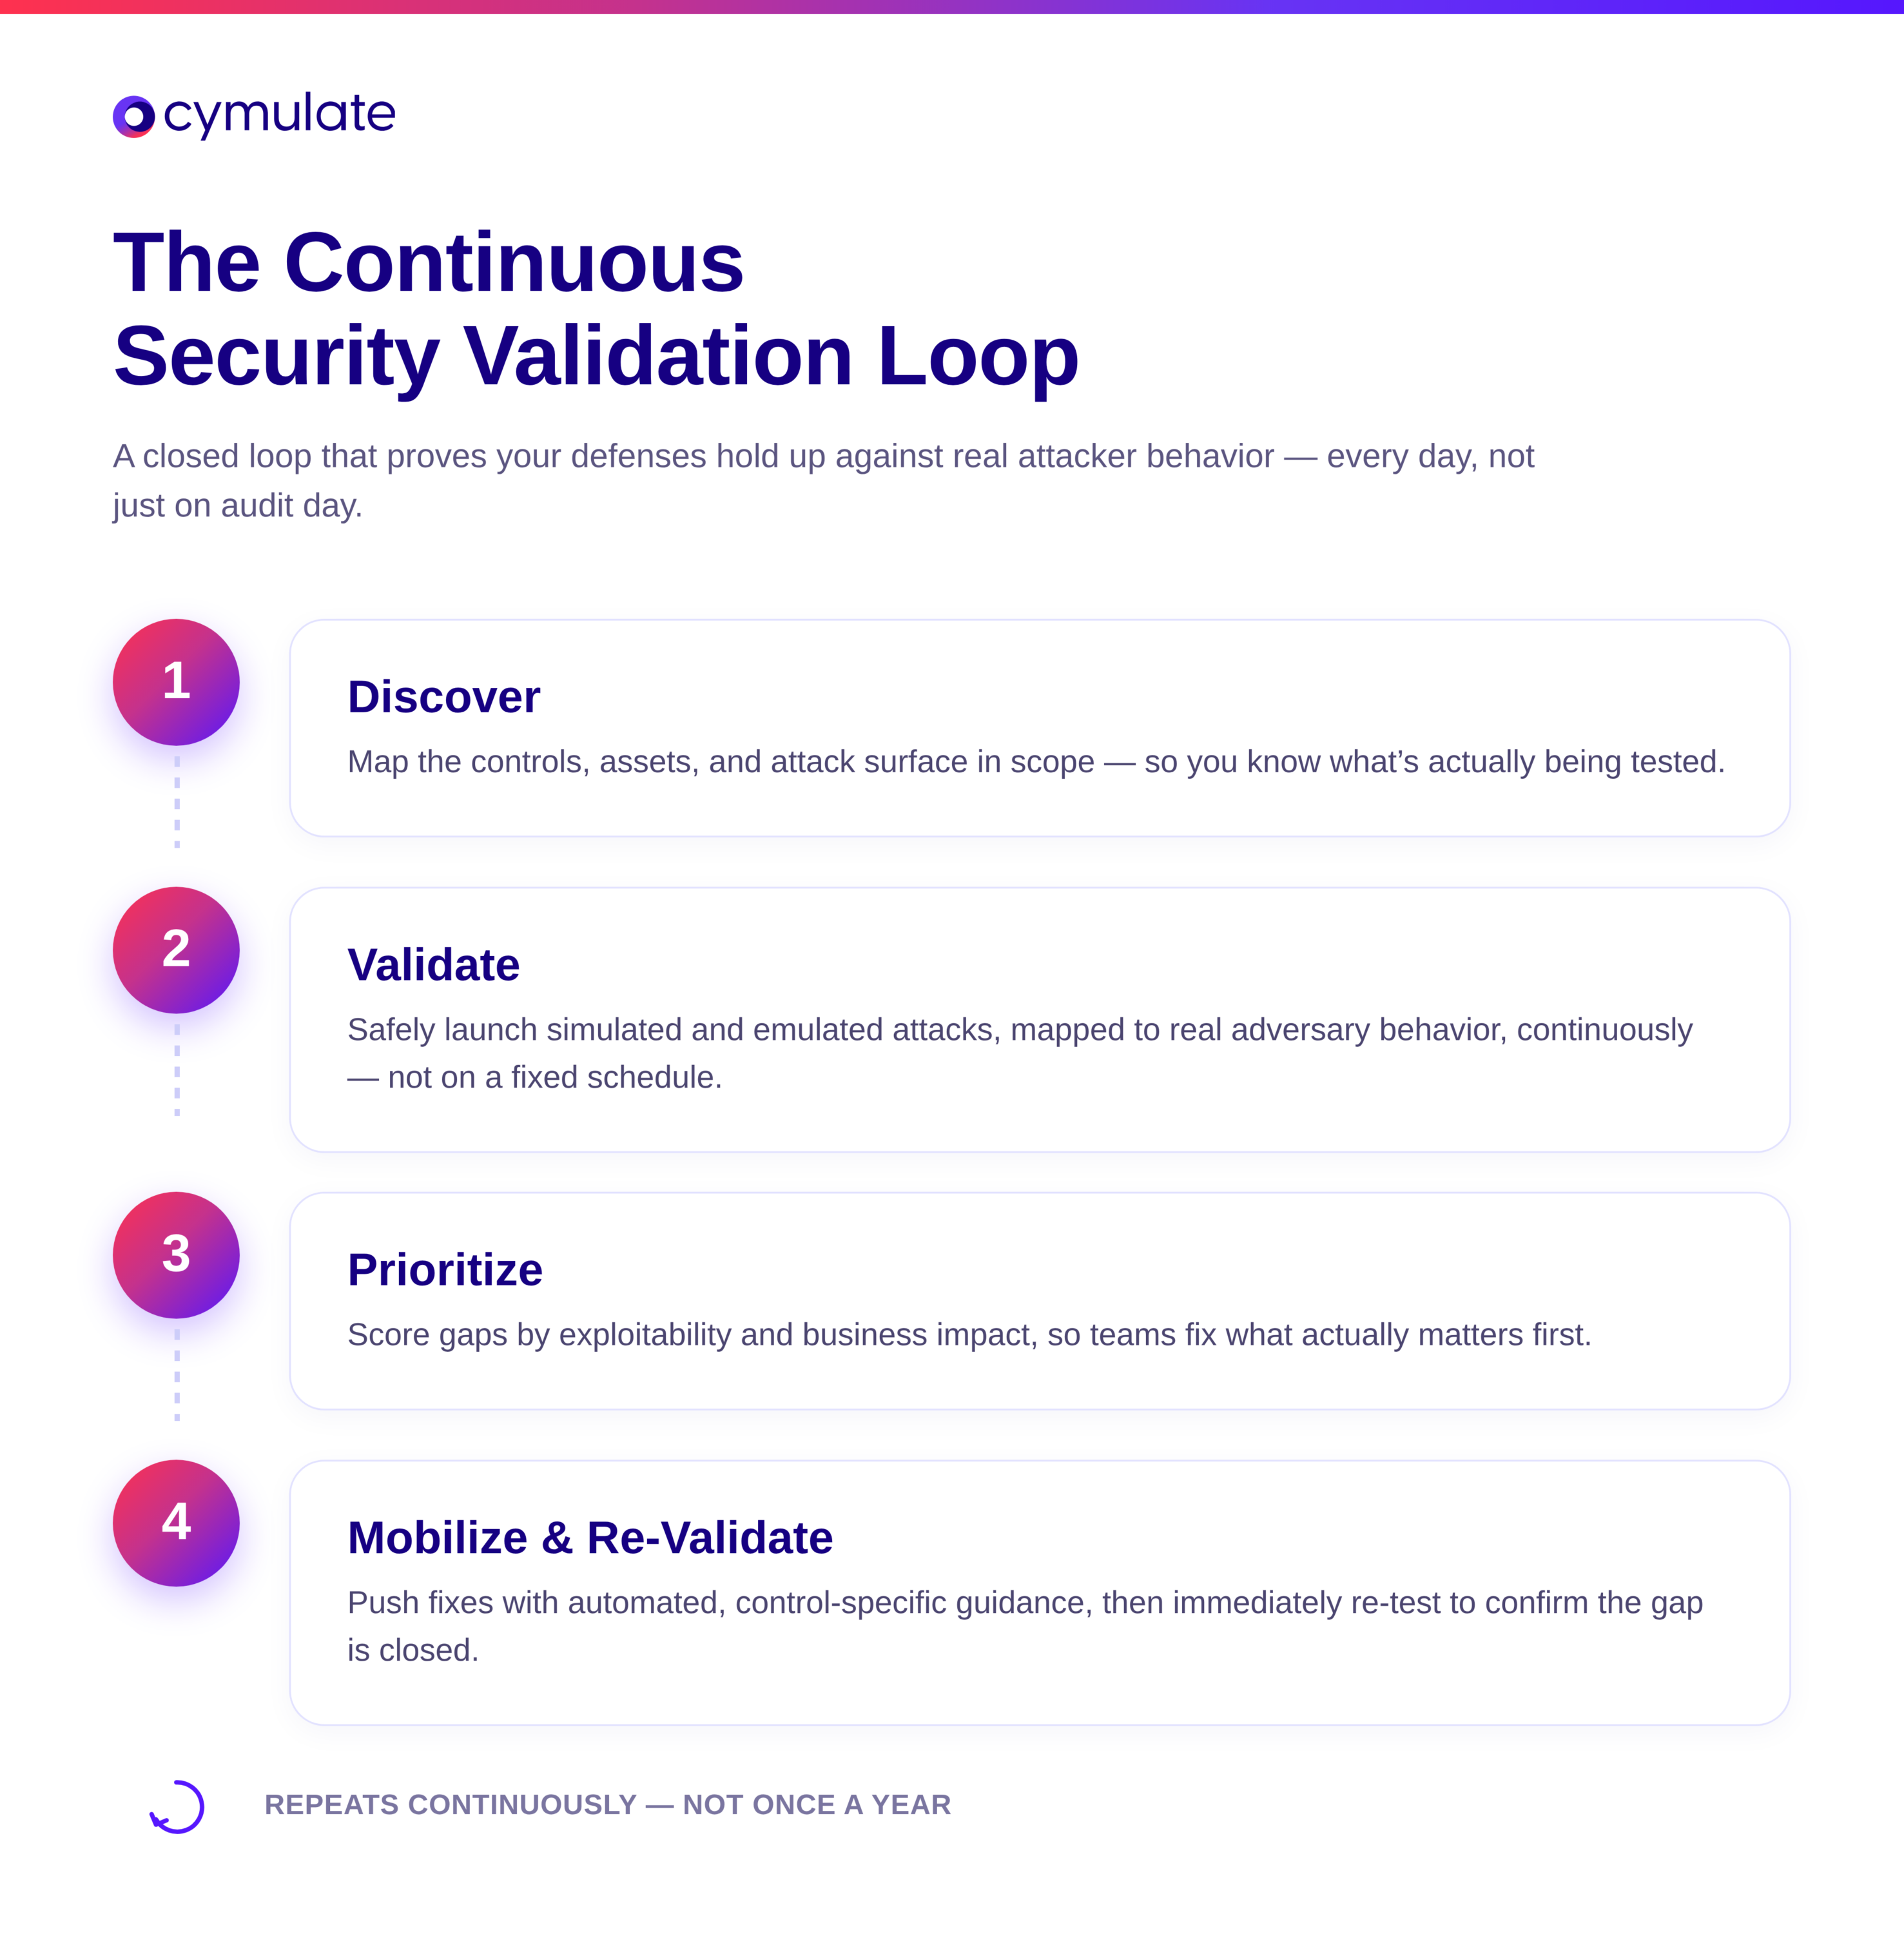
At a high level, a continuous security validation program runs on a repeating loop:

  1. Discover – Map the controls, assets, and attack surface in scope, so you know what’s actually being tested.
  2. Validate – Safely launch simulated and emulated attacks, mapped to real-world adversary behavior, against those controls, continuously rather than on a fixed schedule.
  3. Prioritize – Score the resulting gaps by exploitability and business impact, so teams fix what actually matters first instead of chasing every finding equally.
  4. Mobilize and re-validate – Push fixes (ideally with automated, control-specific remediation guidance), then immediately re-test to confirm the gap is closed — not just marked “resolved” in a ticket.

Cymulate frames this as a closed loop: prove, prioritize, and adapt, where every validation cycle feeds directly back into tuning your defenses, rather than producing a static report that ages the moment it’s delivered.
The Role of Breach and Attack Simulation (BAS)

Breach and Attack Simulation is the engine that makes continuous validation possible at scale. BAS platforms run production-safe automated attacks, mapped to frameworks like MITRE ATT&CK, against your live environment without the risk or cost of a manual red team exercise for every single test.

That automation is what makes “continuous” realistic in practice. A human red team can’t safely or affordably attack your environment every day; a well-designed BAS platform can, running attack scenarios 24/7/365 and updating its attack library daily as new techniques and threats emerge.

These terms get used inconsistently across the industry, so here’s how they actually relate to each other:

Continuous Security Validation vs. traditional penetration testing

A pen test is a manual, point-in-time engagement; it's thorough, but only a snapshot. Continuous security validation is automated and ongoing. Most mature security programs use both periodic deep-dive pen tests for complex, human-led scenarios and continuous validation to catch drift and new exposures in between.

Continuous Security Validation vs. Adversarial Exposure Validation (AEV)

AEV is Gartner’s name for the market category of tools that perform this kind of automated, adversarial testing; it’s the analyst term for the space CSV lives in. When you see “AEV” in a Gartner Market Guide, it’s describing the same underlying capability as continuous security validation.

Continuous Security Validation vs. Continuous Threat Exposure Management (CTEM)

CTEM is the broader program: a five-stage cycle of scoping, discovery, prioritization, validation, and mobilization across your entire attack surface. Continuous security validation is the validation engine inside that cycle - the mechanism that proves which discovered exposures are actually exploitable, rather than theoretical. You can run CSV on its own to harden specific controls; CTEM is what you build once validation is feeding a full exposure management program.
image
Further reading
What is Continuous Threat Exposure Management (CTEM)?

CTEM continuously identifies, validates and prioritizes cyber exposures to reduce risk and strengthen security posture.

Read More

Who Relies on Continuous Security Validation

Different roles lean on continuous validation to answer different questions:

  • CISOs and security leaders use it to move past uncertainty about real-world readiness — replacing “we think we’re covered” with evidence that specific controls actually reduce risk, and a defensible answer when the board asks if the organization is continuously improving, not just reporting.
  • SecOps and detection teams use it to catch security drift as it happens, whether it’s a gap between tools or a control that quietly stopped enforcing a rule, and to turn validation findings into actionable next steps instead of more findings to triage.
  • Detection engineers and blue teams use it to safely test changes before and after they ship, and to measure whether a tuning change actually improved detection coverage rather than assuming it did.

Benefits of Continuous Security Validation

Smarter security spend. When you can see which of your 30+ security tools are actually pulling weight, you stop paying to maintain redundant or misconfigured controls, and can make the case for the investments that matter with evidence, not guesswork.

Measurably lower risk. Organizations using continuous validation report meaningful, measurable improvement. On average, Cymulate customers raise their threat prevention rate from roughly 70% to over 90%, and improve threat detection by more than 50% as measured against MITRE ATT&CK coverage. In one customer case, cyber risk dropped 81% within four months of adopting continuous validation.

Faster, more confident response. Continuous, data-backed visibility into what’s actually exploitable lets teams act on real risk immediately instead of waiting for the next scheduled assessment, and lets security leaders report exposure to the board in concrete numbers rather than a checklist.

Stronger compliance posture. A continuous, evidenced record of control testing is a much easier story to tell auditors than a single annual report.

Protected customer and brand trust. Fewer successful breaches means fewer incidents that erode customer confidence, which is increasingly a competitive differentiator, not just a security metric.

What to Look for in a Continuous Security Validation Platform

Not all “continuous validation” claims are equal. When evaluating a platform, look for:

  • Breadth and depth of the attack library: techniques mapped to MITRE ATT&CK and updated daily, covering the full attack lifecycle rather than a narrow subset of techniques.
  • Safe, production-grade execution testing that won’t take down the systems it’s validating.
  • Prioritization by exploitability, not just severity, so teams aren’t drowning in low-impact findings.
  • A defense engineering control plane: not just a testing engine, but integrations and orchestration that turn validation findings into actual control updates (detection rules, IoCs, configuration changes) across your existing stack.
  • A genuine deploy-and-retest loop: the platform should close the loop by re-validating after a fix ships, not stop at a recommendation.
  • Executive-ready reporting that translates technical findings into business risk.

This is the model behind the Cymulate platform: Cymulate Exposure Validation runs the continuous testing and builds vendor-specific mitigations from the results; Cymulate Auto Mitigation deploys those recommended control updates directly into your stack; Cymulate CTEM ties validation into exposure prioritization and mobilization across your full attack surface; Cymulate Detection Studio validates and tunes SIEM detection rules against real attack scenarios; and Cymulate Threat Studio lets teams build and scale custom offensive testing.

Vero AI powers the agentic layer across all of it - recommending what to test, what matters most, and what to do next, including through Cymulate Cowork, which turns validation into recurring, autonomous workflows. All of it runs on a threat library of 100,000+ attack scenarios, updated daily.

Key Takeaways

Continuous security validation has moved from an emerging best practice to a baseline expectation, driven by AI-accelerated threats, constant security control drift, and growing regulatory pressure for continuous evidence over annual snapshots.

Whether your team calls it CSV, AEV, or “the validation piece of our CTEM program,” the underlying discipline is the same: stop assuming your controls work, and start proving it, continuously. Use that proof to build exposure-informed defenses, not just a longer list of findings.

Book a demo to see continuous security validation running against your own environment.
GET A PERSONALIZED DEMO

Ready to see Cymulate in action?